Need: Code Protection

Powtoon Protects its Core IP and Competitive Advantage with Jscrambler

Powtoon Protects Its Core IP and Competitive Advantage with Jscrambler
Powtoon, a leading visual communication platform, chose Jscrambler to protect its valuable digital assets and stay ahead of the fierce competition.

Overview

Powtoon is a leading video and visual communication platform that was launched in 2012. Powtoon’s mission is to empower individuals, teams, and companies to achieve measurable results by transforming communications into visual experiences that get their audience to care, connect, and act.

Powtoon adds a spark of awesomeness to everyday communications, turning content into substance people want to watch and engage with.

Challenge

For the first 5-7 years of Powtoon’s existence, their e-learning video product was flash-based. However, with the rise of JavaScript, the need to protect their source code arose. With the launch of their HTML5 product, the Powtoon team realized they didn’t want to lose their competitive edge by putting their unprotected source code out there for everyone to see and copy.

Powtoon’s CTO and Co-Founder insisted the team invested in finding and using the best JavaScript protection he could find at the time.

Powtoon needed a solution to protect its core code at runtime and safeguard its digital assets from reverse engineering and IP theft, which would allow it to stay ahead in a competitive market.

Solution

Before choosing Jscrambler, the Powtoon team looked at open-source solutions and found Jscrambler to be the most comprehensive client-side solution with best-of-breed features.

Powtoon started using Jscrambler’s Code Integrity from the very beginning, so their product never went live unprotected at any stage. The polymorphic JavaScript obfuscation was one the biggest factors in choosing Jscrambler as it proved to be very comprehensive and customizable. Additionally, the variety of runtime protections was deemed helpful.

The Powtoon team also enjoyed using Code Integrity’s dashboard and web interface which they preferred instead of having to use some kind of command line tools that they would need to integrate in a complicated way into their build. However, the biggest deal breaker for Powtoon was the performance aspect. They strived to balance the performance of a very complex application with the need to protect it.

“With Jscrambler, we wanted to protect our competitive advantage. We weren’t the first HTML5 product in the market, but we were the only one that was already an established brand. And we didn’t want to risk it as we were already subject to copycats. Some clones were almost identical to us and they were stealing our graphical assets, which are much more difficult to protect.”
Sven Hoffmann, CTO and Co-Founder at Powtoon

“You do not go for the heaviest protection because it just doesn’t fly with our performance requirements. So you look for the right ratio of reasonable price and a reasonable level of protection with a minimal performance impact. That’s what we got with Jscrambler.”
Sven Hoffmann

CTO and Co-Founder at Powtoon

Top Jscrambler Features and Capabilities

  • State-of-the-art first-party JavaScript obfuscation
  • Smooth integration into the existing CI/CD pipeline
  • Minimal impact on website performance

Results

Powtoon’s platform is protected from IP theft and code tampering. Jscrambler provided a comprehensive first-party code protection solution with a minimal performance impact. The Powtoon team is happy with the solution Jscrambler offers, as well as with customer support and the stress-free relationship.

FlippingBook Ensures its Code is Protected from Tampering and Reverse Engineering

FlippingBook Ensures its Code is Protected from Tampering and Reverse Engineering
Jscrambler protects a specific, state-of-the-art component of FlippingBook’s web application to shield it from IP theft and copying.

Overview

FlippingBook offers a suite of powerful products for creating, sharing, and managing digital documents online. The company helps businesses improve communication with their audience through engaging digital documents.

FlippingBook’s technology takes plain PDFs to the next level, making them interactive, easy to share as links, and trackable. Companies across various use cases and industries boost audience engagement with their content, deliver their message in a better format, and understand how their documents perform, making informed decisions to enhance their marketing or sales strategy.

Challenge

In the Digital Marketing industry where FlippingBook operates, there’s fierce competition and a constant need to stay innovative. A successful feature can attract the unwanted attention of competitors, so protecting the technology behind it is vital to remain at the top of the field.

Before implementing Jscrambler’s Code Integrity, FlippingBook’s team used basic security measures, which left their code vulnerable to theft. To protect their intellectual property, they decided to look for a strong, reliable, and advanced-level outsourced solution.

Solution

FlippingBook found Jscrambler through a simple Google search while exploring various JavaScript security solutions. Jscrambler’s extensive set of features, combined with positive feedback from other users, made it clear that it was a reliable choice that would give FlippingBook the level of protection they needed without impacting the performance of their platform. Jscrambler’s focus on comprehensive security, especially protecting intellectual property in web apps, led the team to believe it was the right fit for FlippingBook.

Tim shares, ‘We were looking for a solution that would provide an advanced level of protection against code theft and copying. At the same time, it had to be efficient enough not to interfere with the performance of our own application. Plus, a straightforward CLI integration was a must, and Jscrambler covered that need as well.’ In addition to the seamless CLI integration and trustworthy code protection, FlippingBook’s team appreciates that Jscrambler doesn’t require constant maintenance, so they can focus on internal workflows and innovations while the Code Integrity product keeps their code secure in the background.

“Several years ago, we discovered that our code had been copied by a third party, and we knew we needed to take serious action. Our research indicated that JavaScript obfuscation would be an effective measure to protect our code from such incidents in the future.”
Tim Akhmetvaleev

Head of Sales at FlippingBook

“Our main objective for implementing Code Integrity was to prevent any future code theft attempts and secure the unique, state-of-the-art components of our technology that differentiate us in the market. By using Jscrambler, we wanted to create a robust line of defense around our code, ensuring that it couldn’t be copied or reverse-engineered.”
Tim Akhmetvaleev

Head of Sales at FlippingBook

Top Jscrambler Features and Capabilities

  • Advanced protection through code obfuscation
  • Convenient CLI integration
  • Reliable and responsive customer support

Results

The Code Integrity product gives FlippingBook a competitive edge. By keeping FlippingBook’s code secure from the prying eye of third-party tools, Jscrambler maintains FlippingBook’s image as the innovator and front-runner in the market of digital flipbooks.

Thus, their unique flipbook tech remains unmatched in its sophistication and authenticity compared to other tools out there.

How Bionano Genomics Increased Compliance with Regulations Using Jscrambler

Bionano Increases Compliance with Regulations Using Jscrambler
Jscrambler provided Bionano with the most resilient JavaScript protection and satisfied the regulatory requirements for code protection.

Overview

Bionano is a biotechnology company specializing in genome mapping and analysis and can enable researchers and clinicians to reveal answers to challenging questions in biology and medicine. Bionano’s mission is to transform how the world sees the genome through optical genome mapping (OGM) solutions, diagnostic services, and software. Bionano also offers an industry-leading, platform-agnostic genome analysis software solution and nucleic acid extraction and purification solutions using proprietary isotachophoresis (ITP) technology.

Challenge

Each time Bionano engages in an enterprise-level clinical environment, they are subjected to a rigorous security audit. By interacting with many security organizations globally, they gained an in-depth understanding of what these security organizations expected.

Bionano chose Node.js as its visualization platform as it facilitated reaching the widest audience of users (macOS, PC, and Linux). It also provided an extensive array of visualization tools such as D3js, ThreeJS, and ChartJS that allow the creation of rich interactive genomic maps for customers to explore. Bionano software is free to encourage the use of Saphyr-generated data. Anyone can download and start their own Bionano Access Server. Bionano needed a way to protect their downloaded client and server-side JavaScript logic to satisfy multiple security regulations

Solution

The Bionano system itself is designed not to hold protected private information (PPI), so the company did not face significant liability to be concerned with. However, as an extra precaution and to be as compliant as possible, the company understood the need for JavaScript code protection. In search of the optimal solution, Bionano tested some JavaScript obfuscation solutions but found out that these could be easily reversed or debugged. Jscrambler was the only solution that passed all their tests and which they could not reverse.

This implementation of Jscrambler was greatly derived from the need to comply with several different regulatory requirements. In the specific case of Bionano, the regulations that apply to their clinical customers vary depending on their local principalities. Some regulations, like ISO 27001 and 27002, specifically require source code protections, while others have more general data protection and/or encryption requirements.

Jscrambler does not solve all of Bionano’s security concerns, but it provides what the company needs to protect the source code enough to satisfy all regulations in that regard. Then, there’s also the matter of protecting intellectual property. Bionano’s system provides comprehensive genomic variation data for review.

“Jscrambler was the only product we found that could not be cracked.”
Scott Way

Director of High-Performance Computing and Genome Visualization at Bionano

“We needed our Node.js application protected to satisfy multiple data protection regulations in customer clinical environments. Jscrambler did that for us, and it was easy to incorporate into our tech landscape.”
Scott Way

Director of High-Performance Computing and Genome Visualization at Bionano

Top Jscrambler Features and Capabilities

  • Resilient JavaScript obfuscation
  • Built-in protection against reverse-engineering tools
  • Anti-tampering and antidebugging capabilities

Results

Thanks to the source code protection provided by Jscrambler, Bionano now obfuscates its code and can prevent debugging. This allows them to satisfy the security concerns of their clinical customers and continue using the platform that gave them the best value.

Jscrambler Helps Neobanks Protect JavaScript

How Neobanks Strengthen Client-Side Security with Jscrambler
Several of the world’s leading neobanks and challenger banks turned to Jscrambler to strengthen the security of their web applications as digital channels became central to customer experience and revenue growth. Operating in highly regulated environments and handling sensitive financial data at scale, these institutions needed to protect their client-side JavaScript from reverse engineering,
tampering, and logic abuse.

Overview

Neobanks defy traditional banking by betting everything on digital and delivering customer-centric services for payments and money management. Today, over 90% of consumer interactions with banks are digital. Neobanks typically release new features more frequently, often every few weeks, while traditional banks tend to take several months to bring similar innovations to market. As a result, user satisfaction ratings for neobanks in the US (63%) are higher than those of traditional banks (55%).

Neobanks’ technological flexibility stems from investing in cloud-based infrastructure and advanced web and mobile applications built with modern JavaScript frameworks such as React Native. With this approach, they cut product development cost and time, paving the way for rapid iteration and innovation. This is greatly aided by relying on third-party integrations rather than developing every piece of code in-house. In software development, pursuing agility and speed often means widening security gaps. Despite JavaScript’s numerous advantages, neobanks must be aware that client-side JavaScript is exposed and can be used to launch attacks, including intellectual property theft, code tampering, application abuse, and data exfiltration. Unless protected with an enterprise-grade solution, this exposed JavaScript poses a key business threat.

Challenge

In recent years, several neobanks from North and South America, Europe, and Asia have approached Jscrambler due to significant security challenges. With web and mobile apps built with JavaScript — and a strong adoption of cross-platform frameworks for mobile development like React Native and Ionic — security teams understood early on that client-side logic would pose a significant security risk. There was a high likelihood of having to run sensitive logic on the client-side, so it became paramount to ensure that this logic would be concealed using the most potent and resilient technology available today. It was also mandatory to ensure that automated reverse-engineering tools would always fail to reverse the concealed code, while making it extremely unfeasible for attackers to achieve it manually. As these neobanks’ apps would handle sensitive services, another key challenge was ensuring that malicious actors couldn’t tamper with the code. JavaScript had to react in runtime to mitigate these attacks. And since both the web and mobile apps would handle sensitive data, such as credentials, personally identifiable information, and financial details, an additional pre-eminent requirement was to ensure that JavaScript couldn’t serve as a gateway for attackers to steal user data.

With each neobank offering multiple applications to their end customers, it was also essential to ensure that JavaScript protection would integrate seamlessly with their CI/CD and integration testing. Finally, in such a heavily regulated sector, another significant challenge was achieving compliance with regulations such as PSD2, NIST, the PCI DSS requirements 6.4.3 and 11.6.1, and specific requirements for operation like those of Bank of Brazil, for example, with a special focus on client-side attacks.

Solution

To meet the highest standards for JavaScript protection, these neobanks sought a holistic solution that would fit their processes and scale. Jscrambler presented a mature, proven client-side security product suite that, like noobanks themselves, is defined by continuous innovation.

The first step towards securing JavaScript was Jscrambler’s polymorphic obfuscation. With this critical security layer, all of the source code of neobanks’ apps was concealed beyond possible recognition. Jscrambler’s set of the most potent and resilient transformations was key to guaranteeing cutting-edge obfuscation. Its inherent polymorphism ensured that each new code deployment would be completely different—an extra line of defense against reverse-engineering attempts. For example, one of the banks had their fingerprinting script collect information from the session/browser, and wanted to protect it as it was exposed. Jscrambler provided the neobank with advanced polymorphic obfuscation to allow it to serve its fingerprinting script (practically unique) in each user session.

Security teams implemented critical OWASP recommendations, including the OWASP Mobile Top 10, which highlights that “to prevent effective reverse engineering, you must use an obfuscation tool” and that “the app must be able to react appropriately at runtime to a code integrity violation.” At the same time, they ensured compliance with PSD2 mandates, including transaction monitoring and strong customer authentication, as well as PCI DSS v4 requirements to safeguard payment pages and credit card data from client-side tampering. In addition, they aligned their client-side security measures with NIST guidelines, strengthening code integrity, runtime protections, and risk management practices in line with industry-standard cybersecurity frameworks. Jscrambler mostly worked with Security Engineers at these banks who were well aware of the problem and the required steps for solving it. After the initial setup of the Jscrambler instance, it took on average 2 weeks and 2 meetings with Jscrambler’s engineers to integrate Jscrambler seamlessly into their CI/CD pipeline. From there, Jscrambler became an automated part of their application build process.

Top Jscrambler Features and Capabilities

  • Polymorphic obfuscation
  • Anti-Tampering
  • Compliance with financial regulations and standards

Results

Securing JavaScript code requires awareness of the threats posed by exposing important logic on the client-side. Neobanks have had this pain from the very start of the business, as their main assets depend on it. By opting for Jscrambler’s proven JavaScript protection technology, product teams met their primary requirement: integrating a code protection solution seamlessly into their CI/CD. Now, these neobanks deploy secure code to production, knowing that each build has a fresh set of the most potent and resilient JavaScript protection available today. Jscrambler helped neobanks rethink key and critical data management in the applications, moving keys into JavaScript and applying Jscrambler Code Integrity to protect them effectively.

Through advanced obfuscation techniques, anti-debugging protections, and tamper detection, the solution prevented key theft, code tampering, and reverse engineering, ensuring the web application remained protected even when running on the client side. For management, safeguarding their applications’ source code from reverse engineering and tampering translates into a clear competitive advantage. Investors also recognized the reduced liability associated with exposed JavaScript in neobanking; with Jscrambler, these banks strengthened their position in future funding rounds and earned the trust of millions of potential customers. In a results-driven industry, the outcome was unequivocal: 0 integration issues, 0 successful attacks on JavaScript code.

How Jscrambler Helps dotConnect Deliver Secure Banking Apps

How Jscrambler Helps dotConnect Deliver Secure Banking Apps
Jscrambler successfully protects and secures the source code of the banking applications.

Overview

dotConnect is a fintech with the vision to empower financial institutions to provide their clients with a platform that delivers an exceptional digital banking experience. Via cloud-native solution architecture that is built for scale and resilience, dotConnect allows banks to accelerate their digital transformation and automation journeys. This enables these banks to provide a modern, customer-focused digital experience, reduce operational service requirements, and achieve low and predictable operational costs while also guaranteeing flexible integration with new and legacy banking systems using a decoupled approach.

Challenge

Today, 73% of all consumer interactions with banks are done digitally. And when it comes to banking, security is a prime directive. When asked about the most important attributes when choosing a bank, 82% of consumers say, “ensures my transactions are safe/secure.” Being aware of how security is one of the key drivers in the ongoing banking digitalization, dotConnect wanted to ensure that they were developing secure banking apps. This meant covering every inch of the attack surface.

Regarding web and hybrid mobile banking apps, one key security challenge is protecting the JavaScript code, which can be targeted by reverse-engineering, tampering, and injection attempts. This layer of protection is essential to reduce exposure to data exfiltration and transaction fraud, which can originate from client-side attack vectors.

Solution

The answer to dotConnect’s challenges in terms of source code protection was the cutting-edge technology provided by Jscrambler. Both founders had previously used Jscrambler in a previous solution within the banking sector a few years ago. So, when embarking on this new venture, they revisited the market to compare vendors and found that Jscrambler was still the market-leading solution in this sector. Thus, it was the obvious choice. Because dotConnect had to ensure maximum protection of the JavaScript source code, its team decided to combine two of Jscrambler’s most effective clientside security layers: JavaScript Obfuscation and Self-Defending.

Jscrambler’s Polymorphic JavaScript Obfuscation includes several different techniques that transform the original source code into a new version that is extremely hard to understand and reverse-engineer while keeping its original functionality. Included in this layer is Jscrambler’s Code Hardening feature, which provides up-to-date protection against all reverse-engineering tools and techniques.

dotConnect uses Jscrambler Self-Defending, a security layer that adds integrity checks and other runtime defenses that prevent attackers from debugging or tampering with the code. As such, if anyone tries to debug the protected banking app at runtime, the app will immediately break. Likewise, if an attacker tries to modify the code to dynamically understand its logic at runtime, the application will break to stop the attack. This advanced runtime protection reduces the attack surface to data exfiltration attacks by making it much harder for attackers to understand how the software works and plan/ automate these attacks

“When you have a financial product out in the public domain, you’re a prime target for attackers.”
Mohamed Gamil

CEO & Founder of dotConnect

“The protection layer that Jscrambler provides is very, very difficult to interpret, break, or bypass.”
Mohamed Gamil

CEO & Founder of dotConnect

Top Jscrambler Features and Capabilities

Polymorphic JavaScript Obfuscation
Self-Defending
Code Hardening

Results

dotConnect development team had no issues integrating Jscrambler into the CI build process, thanks to detailed documentation and support. One requirement of dotConnect was to pass their clients’ and their own strict penetration testing rounds. Jscrambler helped them achieve that by passing 5 penetration testing rounds.

Jscrambler 101 – Code Watermarking

Updated on July 15, 2025

Welcome back to Jscrambler 101! A collection of tutorials on how to use Jscrambler to protect your JavaScript. This tutorial covers the Code Watermarking feature, included in the Jscrambler version 8.5.


Introduction

In this article, we’ll explore Code Watermarking, a new Jscrambler feature released in version 8.5. Code Watermarking is a self-service feature that empowers customers to verify ownership of JavaScript code using robust, nearly unremovable watermarks, akin to a digital signature. This feature addresses intellectual property (IP) theft and supports forensic tracing for enterprises.


About the Code Watermarking Protection Feature


How was the feature inspired?

The feature was created to address Jscrambler’s customers’ need for a self-service verification method. Many users are unaware of embedded watermarks, limiting their ability to address IP theft or investigate leaks in web applications. The feature focuses on self-service verification for JavaScript.


How does the Code Watermarking feature work?

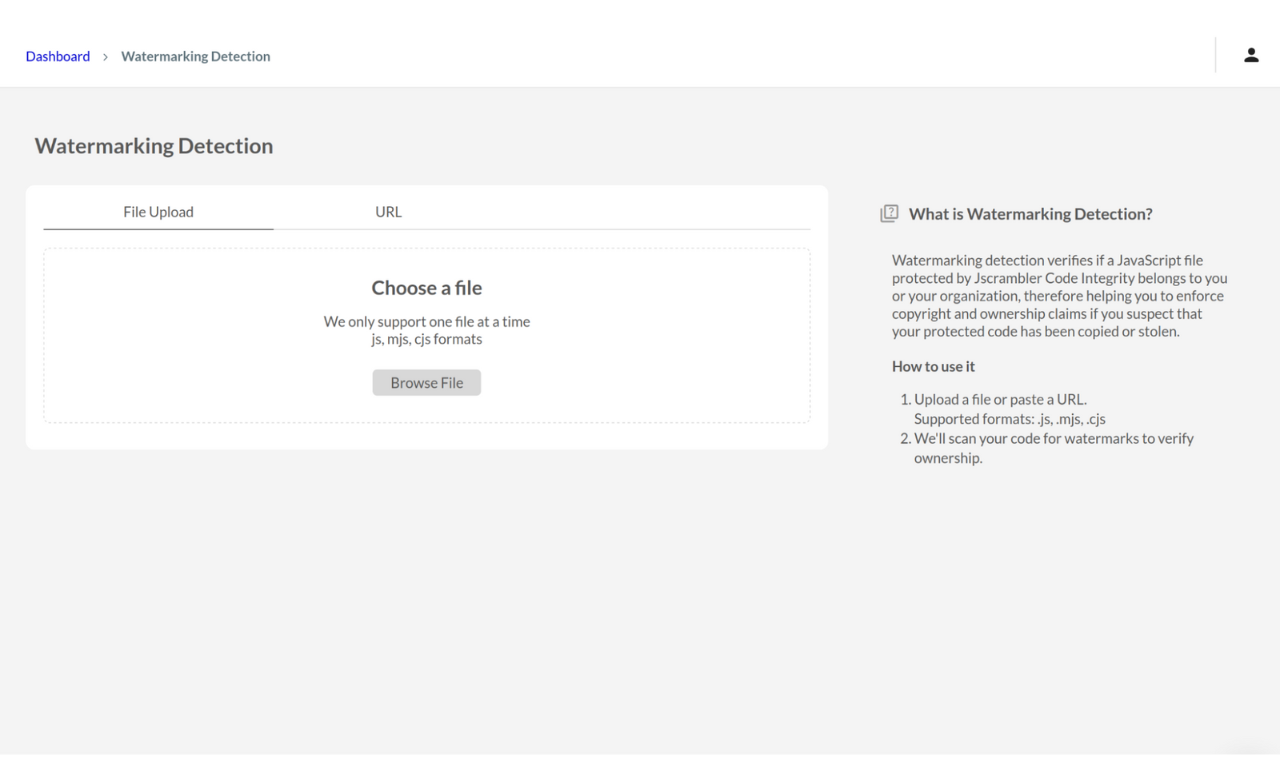
The feature enables users to confirm JavaScript code ownership independently, leveraging watermarks’ signature-like persistence to protect frontend logic and trace code origins without manual support. The “Watermark” UI, as shown in the screenshot, provides an intuitive interface for watermark detection:


code-watermarketing-code-integrity-feature-explanation


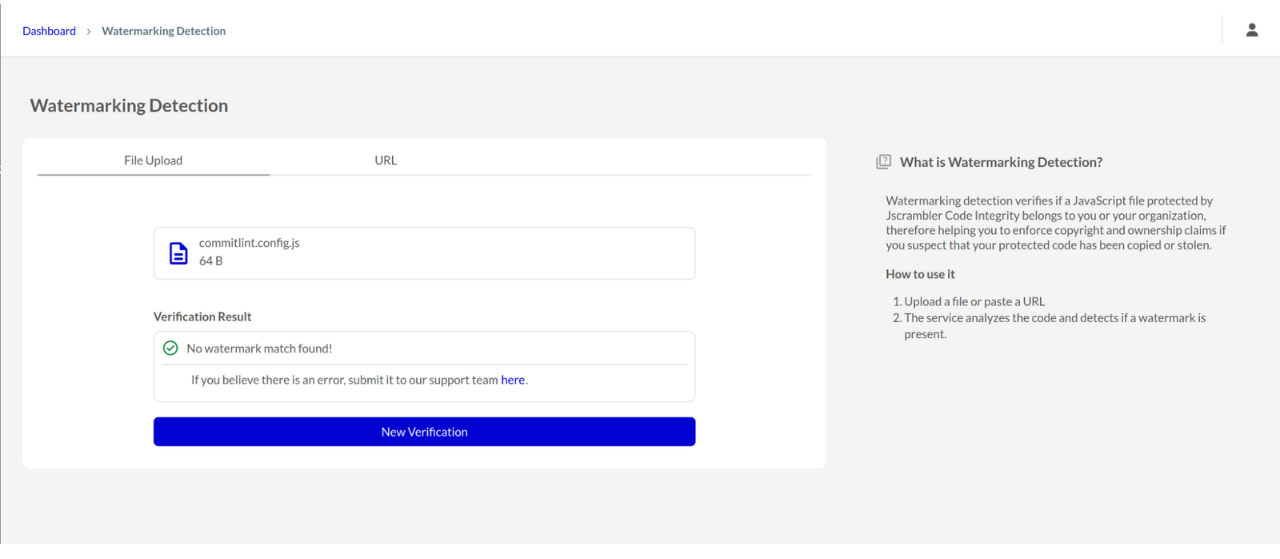
It allows users to upload JavaScript files (.js, .mjs, .cjs formats) or input a URL. The system checks for robust, embedded watermarks (already included in protected code) and displays results: “Code belongs to [Organization], protected on [Date]” or “No watermark match found.” If the user disagrees with Jscrambler’s assessment that a piece of code is theirs, even if no watermark was found, they can submit the file for analysis by clicking a link that appears after our response.


watermarking-detection-example

Code Watermarking Benefits


  • Ownership Verification: confirms if suspect JavaScript is yours, akin to verifying a signature, streamlining IP dispute resolution.
  • IP Theft Deterrence: near-unremovable watermarks discourage copying by ensuring traceability, mirroring a signature’s trust signal.
  • Legal Evidence: provides signature-like proof of ownership for legal disputes.
  • Forensic Tracing: traces leaked JavaScript to its source, supporting breach investigations, similar to signatures that identify origins.
  • Increased Awareness: educate customers about watermarking’s signature-like capabilities.

Conclusion

Code Watermarking offers a robust, signature-like solution to verify JavaScript ownership. By enabling self-service verification within the organization, it delivers immediate value while laying the groundwork for future capabilities, such as automated code scanning, ownership certificates, and AI code attribution. This feature not only strengthens JavaScript security where traditional code signing falls short but also sets Jscrambler apart in a crowded market.

With ongoing customer feedback and planned integrations, Code Watermarking showcases the signature-like robustness of watermarks, emphasizing ownership verification, deterrence, and forensic tracing.


Jscrambler 101 — Self-Healing

Last updated on July 16th, 2024.

Welcome back to Jscrambler 101! A collection of tutorials on how to use Jscrambler to protect your JavaScript. This tutorial covers Jscrambler version 8.3.

Introduction

Last time, on Jscrambler 101 — Countermeasures, we covered one of Jscrambler’s more powerful features: automated anti-debugging and anti-tampering reactions.

This time, we’re going to dive into a new Jscrambler layer: Self-Healing. We’ll explain how Self-Healing works, why it’s a valuable layer, how you can set it up, and in which cases you should use it.

Self-Healing

As you may be aware, one of our main protective layers is Self-Defending, which does an integrity check on the app during runtime, breaking it whenever a debugging or tampering attempt is detected. With the need for more anti-tampering features in mind, in Jscrambler 6.1 we released a new anti-tampering layer: Self-Healing.

Self-healing can regenerate the original code after a tampering attempt by using checksum techniques to verify its integrity. As so, an application protected with self-healing does not break if someone tampers with its code; instead, it guarantees that only the correct code is executed. The app breaks into extreme tampering scenarios.

With Jscrambler’s Self-Healing JavaScript, you can thwart code tampering while keeping the application’s user experience undisturbed.

As an added benefit, Self-Healing’s behavior is likely to frustrate attackers even more when they’re trying to debug or tamper with the app. The application will only break in extreme tampering scenarios.

Self-Healing is also completely integrated with Jscrambler’s JavaScript Threat Monitoring, so you’ll be able to see (in real-time) every occurrence of Self-Healing coming into action to protect your code.

Setting Up Self-Healing

Jscrambler Web App

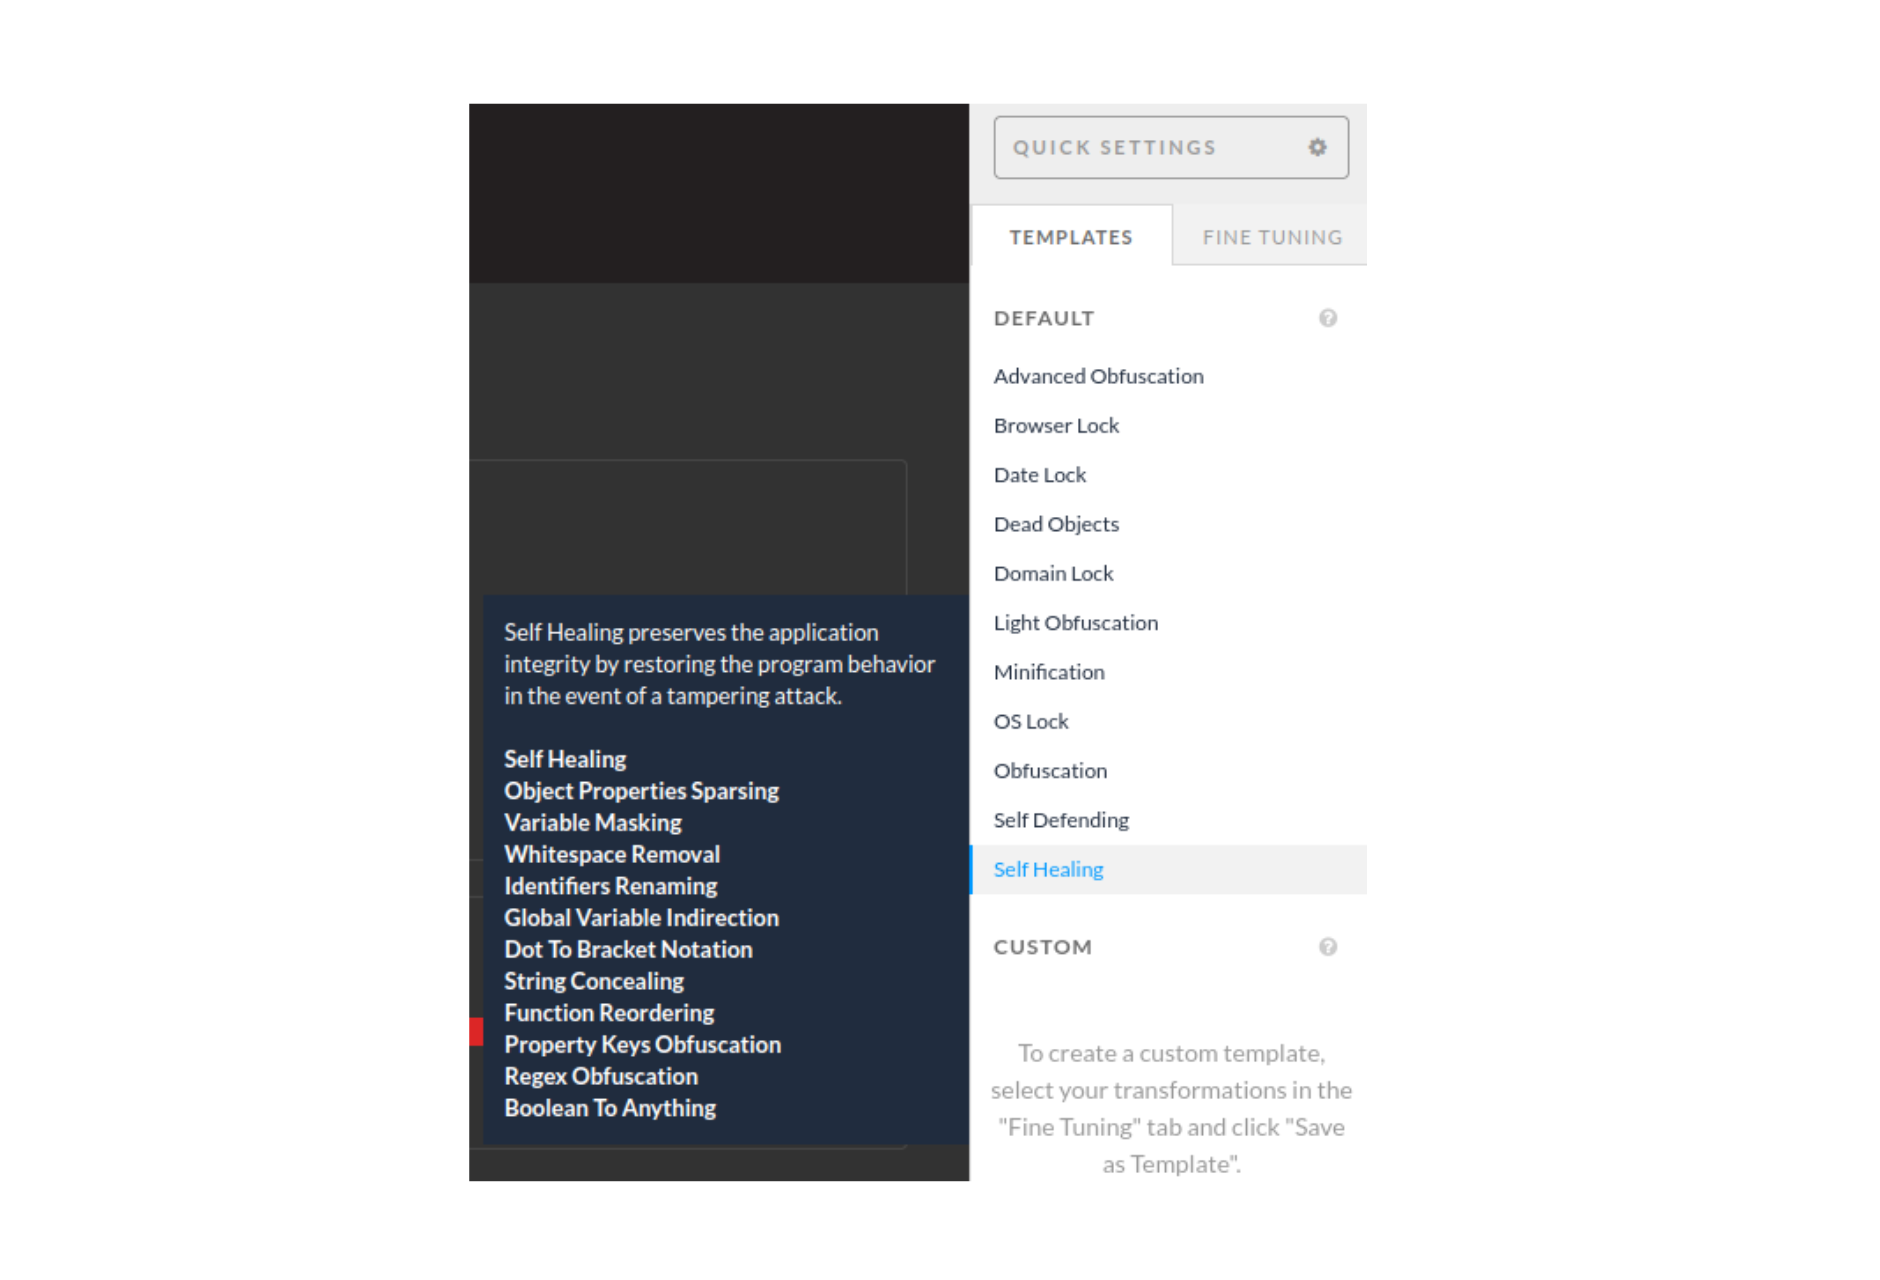
The most straightforward way of getting Self-Healing up and running is through the Jscrambler Web App. Once you’re on your app’s Protection page, you can either select the Self-Healing template, as shown below:

self healing template-jscrambler-tutorial

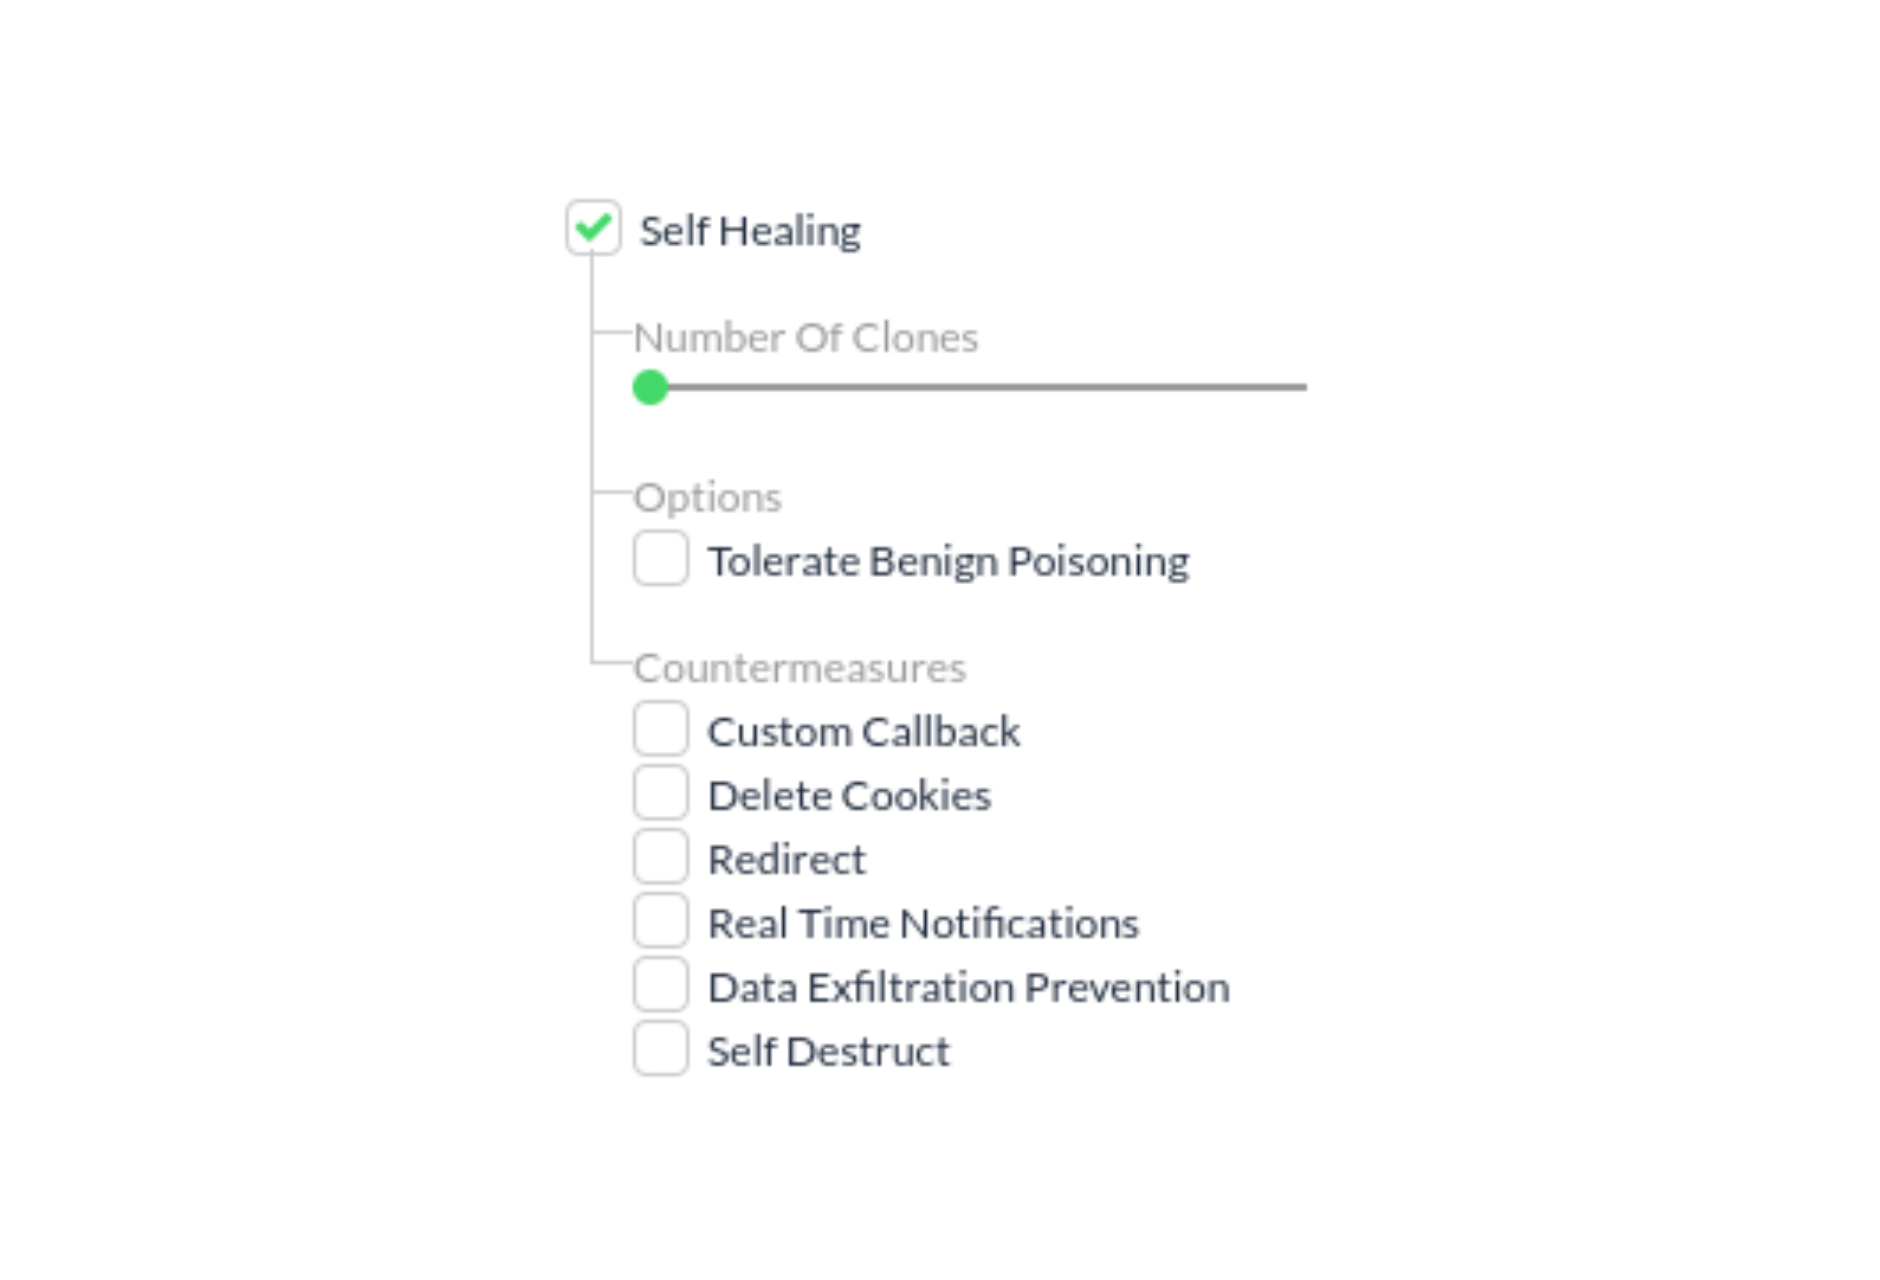
Or you can individually select Self-Healing in the Fine-Tuning tab, which will display several Self-Healing parameters that you can configure:


Self-Healing-Fine-Tuning-tab-explanation

Jscrambler API Parameters

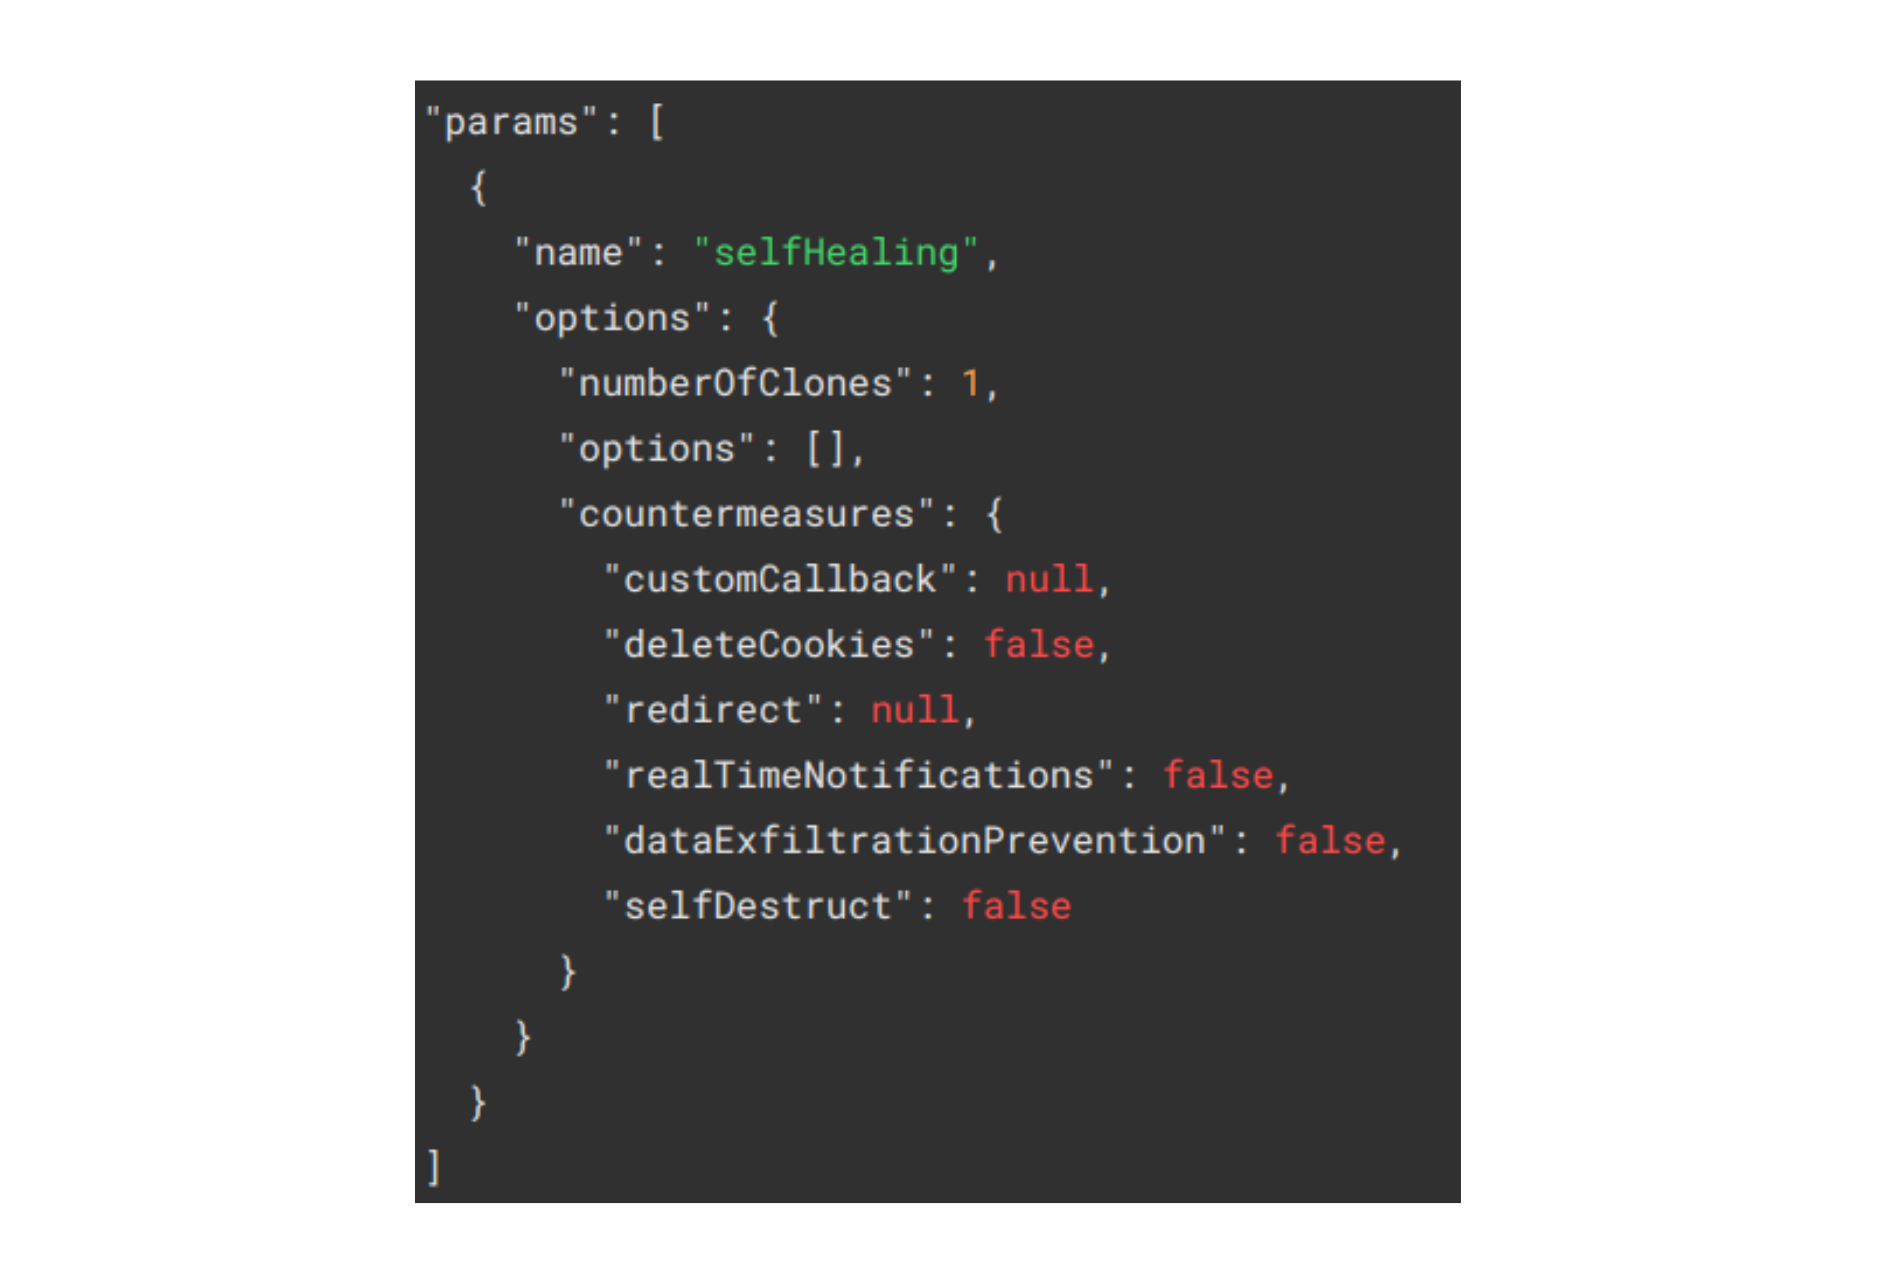
If you’re using the Jscrambler CLI, you simply have to set Self-Healing in the params section of the Jscrambler config file, as below:

jscrambler-api-parameters-jscrambler


Self-Healing vs. Self-Defending

Both Self-Healing and Self-Defending have anti-tampering features. However, they work differently.

First, it’s useful to keep in mind that Self-Defending provides both anti-tampering and anti-debugging features (Self-Healing only tackles the former). Second, they tackle tampering attacks with different approaches and objectives; both check the code integrity during runtime, but:

  • Self-defending breaks the app immediately if the integrity check fails.
  • Self-healing actively seeks to replace the compromised code with the original code. The application will only break if no replacement is found, avoiding the execution of unsafe code.

Because they both tackle tampering attempts, generally speaking, it doesn’t make sense to apply both Self-Defending and Self-Healing globally to the app. However, it does make sense to apply Self-Defending to some parts of the code and Self-Healing to others using code annotations.

Knowing where to apply each of these techniques will vary according to your app, as we’ll discuss below.

Self-Healing Use Cases

Knowing how Self-Healing tackles tampering attempts, a general use case would be to apply Self-Healing to portions of the code for which you want to ensure that the app doesn’t break (code that’s vital to the user experience) and Self-Defending to the most sensitive portions of the code, for which you want the app to break in response to tampering or debugging attempts.

This behavior can be especially important in industries that rely on critical apps, such as Healthcare, Manufacturing, or IoT. In these cases, downtime for the affected website or app can lead to huge costs.

With Self-Healing’s approach, tampering attacks can be successfully mitigated while keeping systems operational.

Conclusion

This sums up Jscrambler’s Self-Healing. Remember that you can test the Self-Healing template using our Playground app, or even in your app if you have an active Jscrambler license.

Enjoy your testing and start protecting your Applications ASAP! If you have any additional questions, feel free to contact us.
Jscrambler 101 – Collaborative Workspace

Welcome back to Jscrambler 101! A collection of tutorials on how to use Jscrambler to protect your JavaScript. This tutorial is about the Collaborative Workspace feature and covers Jscrambler version 8.4.

Introduction


This article will explore the Collaborative Workspace, a new Jscrambler feature released in version 8.4. This feature allows multiple users to work on the same app seamlessly.


About the Collaborative Workspace feature


How was the feature inspired?

It’s a normal scenario for many of our customers to have one developer assigned to log into the Jscrambler dashboard to work on protecting the application. However, with more and more of our clients adhering to strict security measures and involving their whole security teams, it was apparent that a feature for collaborative work was much needed.
Now Jscrambler’s Code Integrity supports assigning more than one user to access the same app and apply protections. This means that when one person from a team logs in to Code Integrity using their individual account credentials and uploads a given code/app to Code Integrity, other team members can see, access, and protect that same app, as well as check the history log.


The Collaborative Workspace feature facilitates teamwork and removes the limitation that might lead users to share their login credentials, reinforcing a bad security practice. It also prevents users from manually looking for the latest protection recipe applied to an app every time there is a need to revise the protection.


How does the Collaborative Workspace feature work?

With this “multiple users” reality, a new concept of “organization” is introduced to Code Integrity.

An “organization” represents a customer and each “organization” can have several apps and several “users” under its umbrella. Each user has their individual account for logging in to Code Integrity. Each user can be assigned to one or several apps and each app can have one or more users assigned. There are different degrees of permissions granted to each user.


It is important to note that the “organization” must have an administrator. The user with this responsibility has access to an “administration screen”, through which it is possible to manage the users, roles, and permissions, as well as add new users to the organization and remove existing users from the organization.


code-integrity-new-feature-collaborative-workspace

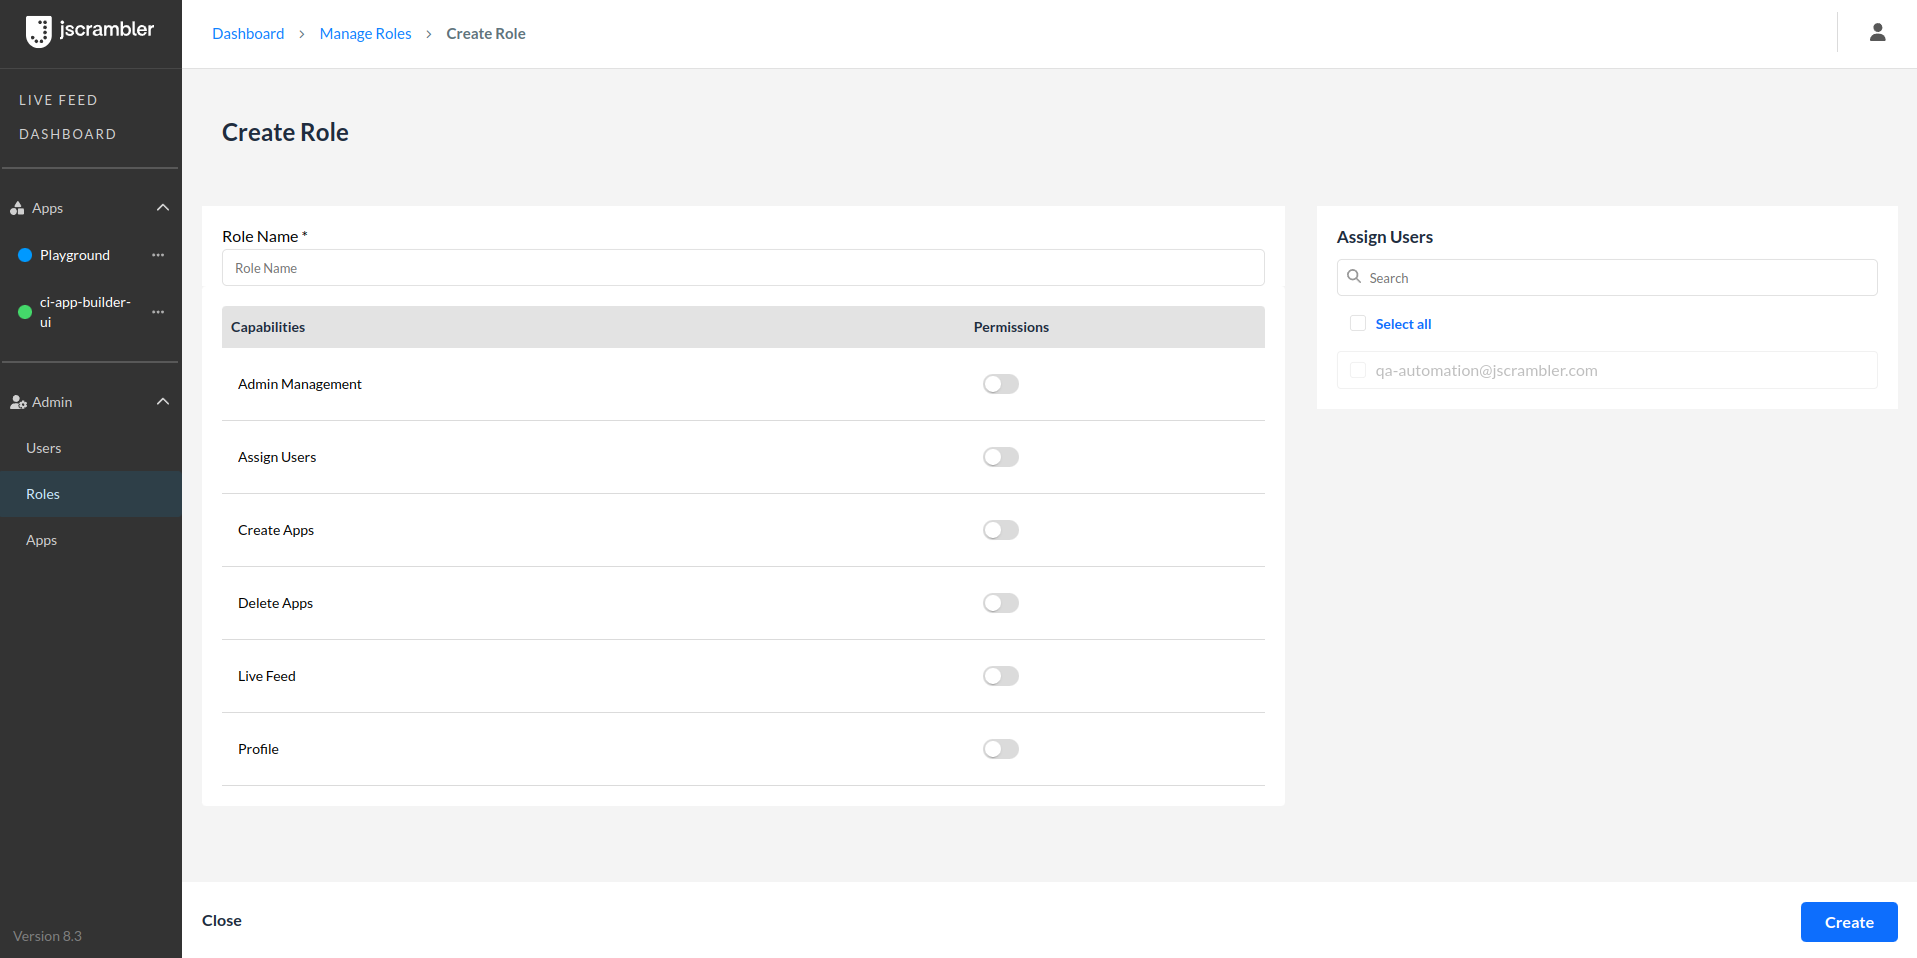
An Admin user can create a new role for a user and apply all the relevant permissions.
  

admin-user-create-new-role-for-users

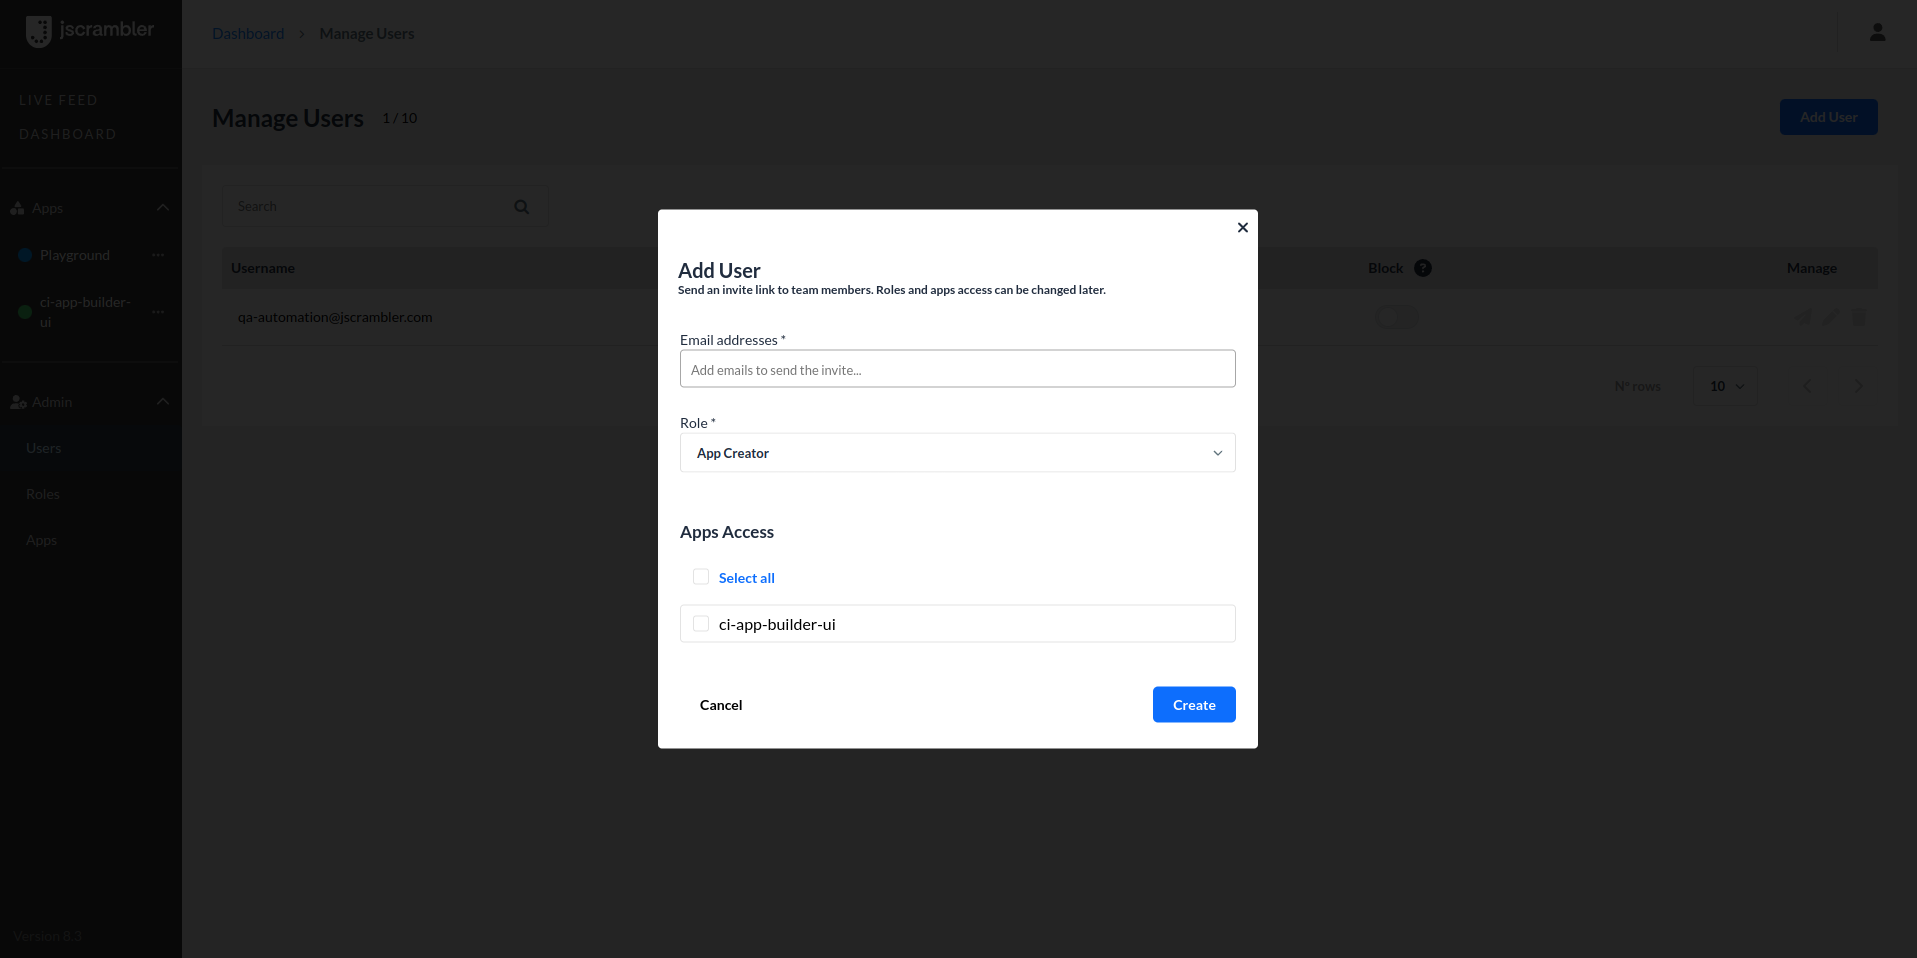
Adding users and assigning them to specific app/s is quick and easy.


manage-roles-tutorial
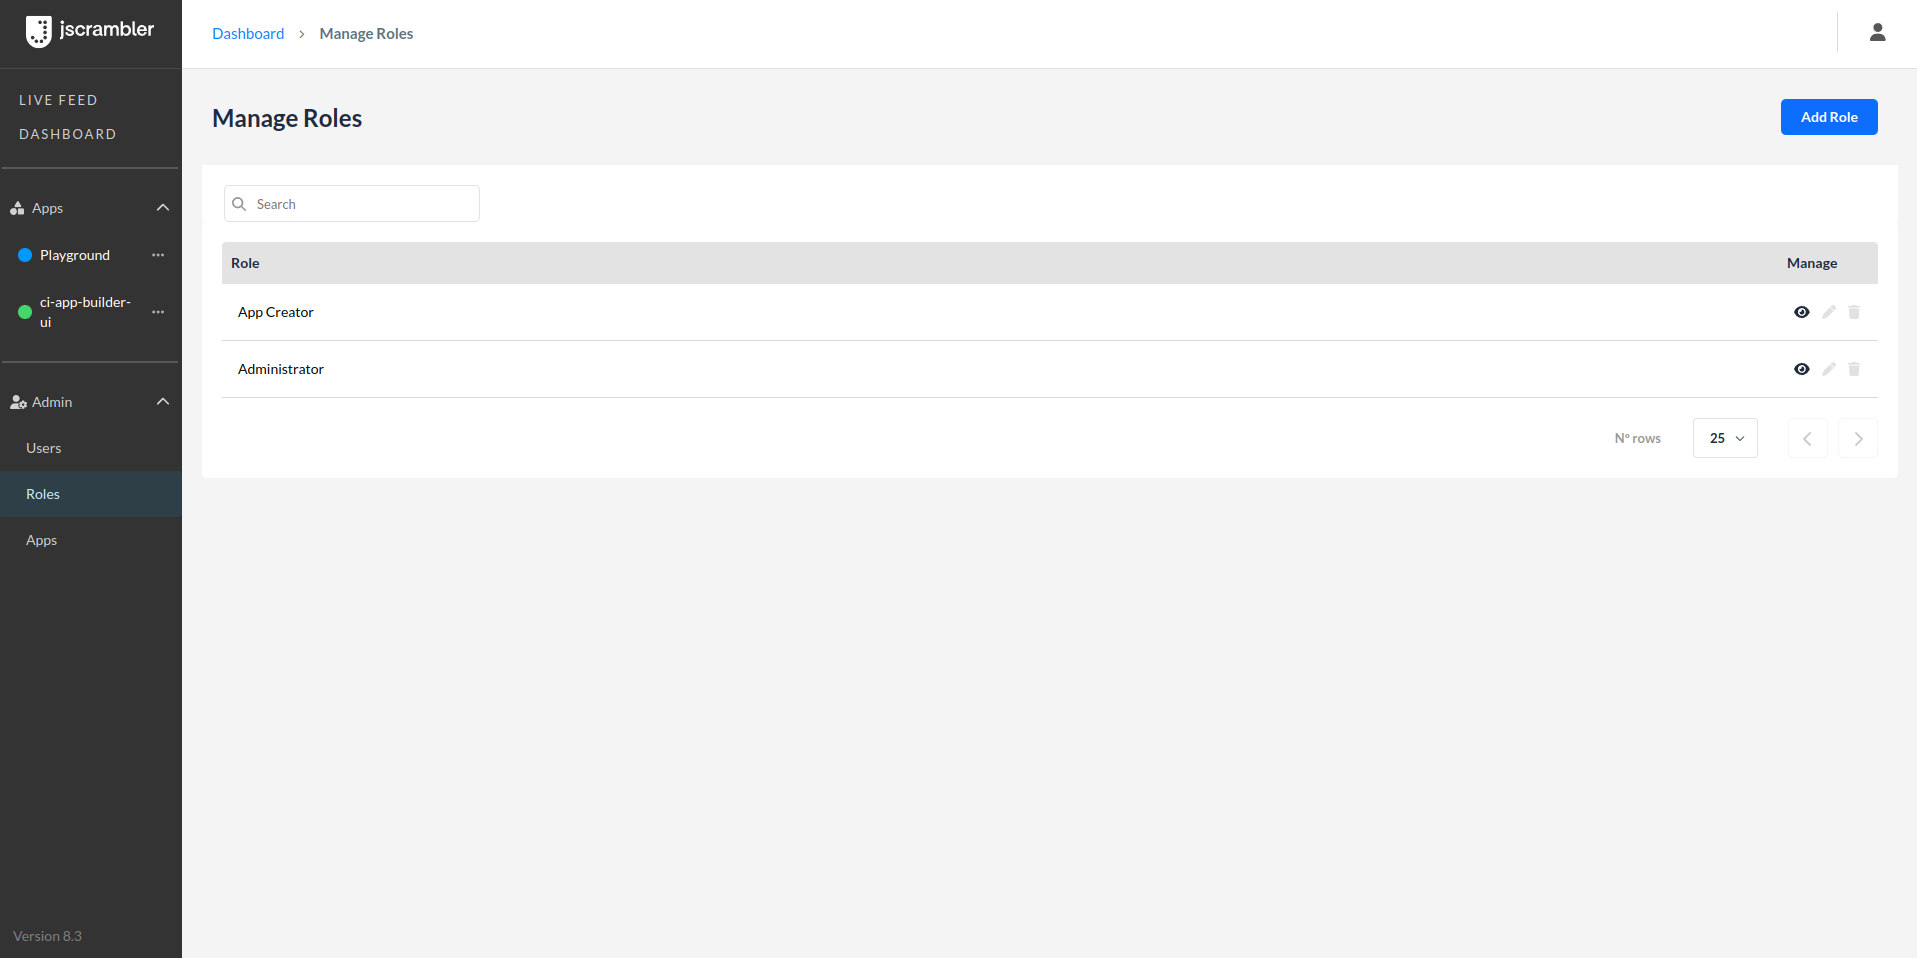
An Admin user can manage roles and change permissions.


All users assigned to the same “organization” see the same information, however, one user cannot be assigned to more than one “organization” at the same time.


Benefits of Collaborative Workspace


  • Enhanced Collaboration
    • Shared Access: Multiple developers can seamlessly work on the same app, eliminating the need for sharing login credentials or manual reassignments.
    • Unified View: All users assigned to an app can see the same information, including uploaded files, transformation parameters, and protection history.


  • Improved Security Practices
    • Individual Accounts: Each user has their login, reducing the security risks associated with sharing credentials.
    • Detailed Activity Logs: Enhanced protection history tracks who made specific changes, ensuring accountability and traceability.


  • Scalability for Large Security Teams
    • Scalable for Large Teams: Supports complex organizational structures by allowing multiple users and roles within an organization, making it ideal for large enterprises.
    • Role-Based Access Control: Flexible permissions allow precise control over what each user can do, ensuring that security and operational needs are met.

Conclusion

This new feature empowers teams with a shared vision to safeguard their applications collaboratively. Whether it’s creating or deleting apps, assigning or removing users, or inviting new team members, our platform ensures efficient and secure app management for your organization.

Jscrambler 101 — Code Annotations

Last updated on May 28th 2024.

Welcome back to Jscrambler 101! A collection of tutorials on how to use Jscrambler to protect your JavaScript. These tutorials cover Jscrambler version 8.3.

Introduction

Last time, on Jscrambler 101 — First Use, we talked about using our web app, applying transformations, creating templates, and learning how to export transformations as a JSON file, among other tips.

This time, we’re going to talk about Code Annotations.

What are Code Annotations?

Code Annotations are JavaScript comments you can add to your code. They are used to change Jscrambler’s behavior when protecting your app.

Sometimes, the transformations that you apply to protect your code can cause performance issues or obfuscate your code in an undesired way. Code Annotations can be used to counteract these situations.

Streamline This Process with Jscrambler Profiling

Using the Profiling feature, you can let Jscrambler do most of the heavy lifting towards minimizing eventual performance impact. Then, you can still tweak the final result using code annotations.

The existing Code Annotations directives are:

  • enable — enables transformations and transformation aliases
  • define — defines a transformation alias with custom options
  • disable — disables transformations, transformation targets, and transformation aliases
  • order — enables transformations and transformation aliases in a specific order (allows repetition)
  • target — enables all transformations available for a transformation target

To show you how Code Annotations work, we’re going to use several code snippets. Each snippet will focus on a certain directive.

Enable

Starting with the getSecret function, let’s assume we have a string with sensitive information such as a secret:

function getSecret() {
    return 'This is the secret.';
}

We want to specifically encode this string which has sensitive information, so we add the enable directive locally.

// @jscrambler enable stringEncoding
function getSecret() {
    return 'This is the secret.';
}

This will enable the String Encoding transformation on our string.

function getSecret() {
    return 'u0054u0068u0069u0073u0020u0069u0073u0020u0074u0068u0065u0020u0073u0065u0063u0072u0065u0074u002e';
}

It still looks a bit too easy to decode, so we’re going to add String Concealing as well:

// @jscrambler enable stringEncoding, stringConcealing
function getSecret() {
    return 'This is the secret.';
}

This will become:

var uPIi = {
//string concealing and encoding
};
//...
function getSecret() {
    return uPIi.o(0);
}

Let’s say you’ve added other strings with sensitive information and found it best to simply encode and conceal every string in the file.

function getSecret() {
    return 'This is the secret.';
}
//…

function getAnotherSecret() {
    return 'This is another secret.';
}

We can use global enable to affect the whole file, like this:

// @jscrambler global enable stringEncoding, stringConcealing
function getSecret() {
    return 'This is the secret.';
}
//…

function getAnotherSecret() {
    return 'This is another secret.';
}

This will be transformed into:

var pLZi = {
//string concealing and encoding
};
//...
function getSecret() {
    return pLZi.n(1);
}
function getAnotherSecret() {
    return pLZi.n(0);
}

Now, both displayed secrets have been transformed by String Concealing and String Encoding.

Disable

Imagine you’re using a file that has a global String Encoding, and you have a code block that does operations on a string.

// @jscrambler global enable stringEncoding, numberToString
var a = 'some string';
var b = 1;

//...
for (i = 0; i < 1000; i++) {
    //something happens with strings
    var s = 'disable string encoding here';
    //...
}
var t = 'should be transformed';

Say you don’t want String Encoding to transform the strings inside the loop — as it would affect code performance — but you want all the other strings outside of this loop to be transformed. You can use the disable annotation.

// @jscrambler global enable stringEncoding, numberToString
var a = 'some string';
var b = 1;
//...
// @jscrambler disable stringEncoding
for (i = 0; i < 1000; i++) {
    //something happens with strings
    var s = 'disable string transformations here';
    //...
}
var t = 'should be transformed';

Now Jscrambler will act so that the strings inside the loop won’t be affected by the transformations, but everything else will be affected.

As we only have the String Encoding disabled, you’ll notice that Number to String still works on the for loop.

var a = 'u0073u006fu006du0065u0020u0073u0074u0072u0069u006eu0067';
var b = "1" + 0;
//...
for (i = "0" * 1; i < "1000" - 0; i++) {
    var s = 'disable string transformations here';
}
var t = 'x73x68x6fx75x6cx64x20x62x65x20x74x72x61x6ex73x66x6fx72x6dx65x64';

If you don’t want transformations to occur at all in a code block, use //@jscrambler disable *

// @jscrambler global enable stringEncoding, numberToString
//...
// @jscrambler disable *
function foo() {
    var a = 'I won't be affected';
    function bar() {
        var b = 'I won't be affected either';
    }
    // @jscrambler global enable stringEncoding, numberToString
    var c = 'But I wan't to be affected';
    var d = 2;
}

You will notice that the strings in var a and var b aren’t affected by any transformation. We wanted var c to be affected by these transformations though, so we had to insert a new Jscrambler to enable annotation.

function foo() {
    var a = 'I won't be affected';
    function bar() {
        var b = 'I won't be affected either';
    }
  var c = 'x42x75x74x20x49x20x77x61x6ex27x74x20x74x6fx20x62x65x20x61x66x66x65x63x74x65x64';
  var d = 2;
}

If we want var d=2; to be affected by Number to String though, we’ll have to add another code annotation directly above it, as so:

// @jscrambler enable stringEncoding, numberToString
var c = 'But I wan't to be affected';
// @jscrambler enable stringEncoding, numberToString
var d = 2;

This would become:

var c = 'x42x75x74x20x49x20x77x61x6ex27x74x20x74x6fx20x62x65x20x61x66x66x65x63x74x65x64';
var d = "2" * 1;

Define

Define can be used for transformations that include options, such as Self-Defending, CharToTernaryOperator, and ControlFlowFlattening.

Define works by using both define and enable.

//@jscrambler define charToTernaryOperator {tern: [0,1]} as iR1
//@jscrambler enable iR1
var a = 'o';
var b = 'o';

Here, we’re using the Char to Ternary Operator transformation and setting its option tern, which is the minimum number of ternary operators between 0 and 1. This includes 0 and 1 as the minimum number of ternary operators and generates a random output.

var a = (730.08, 860.34) < 4.43 ? 0x13c4 : 'o';
var b='o';

We could use other numbers such as 2 and 3, so that:

//@jscrambler define charToTernaryOperator {tern: [2,3]} as iR1
//@jscrambler enable iR1
var a = 'o';
var b = 'o';

Would become:

var a = (5523, 8821) < (634, 4753) ? 108.94 < (230.23, 2050) ? 2880 <= 9190 ? 610.76 : (4.35e+2, 521.21) : (false, 6.46e+2) : 'o';
var b='o';

Define is local and will only affect the code block below it — so remember to use global when you want to affect more than one location. For example:

//@jscrambler define charToTernaryOperator {tern: [0,1]} as iR1
//@jscrambler enable iR1
var a= 'o';
//@jscrambler enable iR1
var b= 'o';

Won’t affect var b. But, if we use global, iR1 can be reused in var b.

//@jscrambler global define charToTernaryOperator {tern: [0,1]} as iR1
//@jscrambler enable iR1
var a= 'o';
//@jscrambler enable iR1
var b= 'o';

The transformed code will look like this:

var a = (730.08, 860.34) < 4.43 ? 0x13c4 : 'o';
var b = (273.32, 907.6) === (1500, 5782) ? (9.92e+2, false) : 'o';

Aliases — as all other code annotations — are inherited from upper blocks. So, if you define an alias for a block, you can enable it not only in that block but also in any of the inner statements and blocks without using global.

// @jscrambler define charToTernaryOperator {tern: [0,1]} as iR1
function foo() {
 function bar() {
   // @jscrambler enable iR1
   function baz() {}
 }
}

In this case, only baz() will be affected by the charToTernaryOperator.

Order

Order allows transformations to be executed in a set order. As an example:

// @jscrambler order numberToString, stringEncoding
var strNum= 123;
// @jscrambler order stringEncoding, numberToString
var numStr= 456;

The strNum variable will first be affected by numberToString, followed by stringEncoding, while numStr will first be affected by stringEncoding, then numberToString.

You’ll notice that numStr was only affected by numberToString since at the time stringEncoding was performed, there wasn’t any string to act on.

var strNum = +'x31x32x33';
var numStr = "456" | 0;

Order is best used to handle situations such as these — where the order in which the transformations are applied severely affects the outcome.

Imagine you want to set a specific order for the whole JavaScript source code. To do this, you can use the global modifier.

// @jscrambler global order numberToString, stringEncoding
var strNum = 123;
var numStr = 456;

Will become:

    var strNum = +'u0031u0032u0033';
    var numStr = 'u0034u0035u0036' - 0;

You can also repeat transformations, but the same transformation can only be repeated up to 3 times. Something like:

// @jscrambler order dotToBracketNotation, numberToString, stringEncoding, numberToString, stringEncoding
map.moveTo(0, 0);

It is transformed to:

map['u006du006fu0076u0065u0054u006f'](+'u0030', 'u0030' - +'u0030');

By repeating numberToString and stringEncoding, the numeric arguments produced by the first stringEncoding were transformed and all strings were encoded twice.

Some transformations can only be used once per node. These are:

  • charToTernaryOperator
  • selfDefending

The order can also be inherited — so if you define a specific order for a block, any inner statement and block will inherit it and combine it with any directive defined at that point. This means that:

// @jscrambler order A, B, C
function foo() {
 // @jscrambler order D, E
 function bar() {}
}

Will be applied in the following order:

// [A, B, C]
function foo() {
 // [D, E, A, B, C]
 function bar() {}
}

Code annotations prioritize local order, so D and E will always be performed before A, B, and C.

Transformations are also merged if they are repeated such as:

// @jscrambler order A, B, C
function foo() {
 // @jscrambler order A, A
 function baz() {}
 // @jscrambler order B
 function qux() {}
}

This will be merged to act in the following manner:

// [A, B, C]
function foo() {
 // [A, A, B, C]
 function baz() {}
 // [B, A, C]
 function qux() {}
}

For the baz function, transformation A is executed twice, as it was defined locally that way.

For the qux function, B is executed before A and C, because the local code annotation has priority over the global annotations and the global B ends up being merged with the local B.

Target

Now, say you have the following function.

function foo() {
    var reallySuperMegaHugeBigLongVar = 'target me!!';
}

You want to target the strings and identifiers in the function but aren’t sure what transformations you should apply. If you were to add a target strings, and identifiers as we do below:

//@jscrambler target strings, identifiers
function foo() {
    var reallySuperMegaHugeBigLongVar = 'target me!!';
}

Then run a protection, you’ll notice that both the string and identifiers are affected. This happens because Jscrambler will target strings and identifiers, applying transformations accordingly.

var aWua = {
//string transformations
};
//...
function foo() {
    var i = aWua["f"](0);
}

The available targets are:

  • booleans
  • controlFlow
  • functions
  • identifiers
  • numbers
  • objects
  • predicates
  • regularExpressions
  • statements
  • strings
  • variables

Target is equivalent to a global enable of a set of transformations, so it will affect all functions in a file. It’s easy to use — especially if you don’t know what transformations are available but know what you want to protect.

You can test all these Code Annotations on your Dashboard. Simply create a new app, insert the code snippets, and run protection without selecting any transformations.

You’ll see that the resulting code has the protections applied according to the used code annotations. Since we didn’t apply powerful sets of transformations, you can easily see how each code annotation affected each snippet.

Conclusion

You should now be able to use Code Annotations to change Jscrambler’s behavior when protecting specific code blocks.

Don’t forget to use the global modifier when you want to affect the whole source file. Feel free to proceed to one of our other 101 Tutorials:

Enjoy your testing and start protecting your Applications ASAP! If you have any additional questions, feel free to contact us.

Jscrambler 101 — Countermeasures

Last updated on April 9th, 2024

Welcome back to Jscrambler 101! A collection of tutorials on how to use Jscrambler to protect your JavaScript. This tutorial covers Jscrambler version 8.3.

Introduction

Last time, on Jscrambler 101 — Source Maps, we detailed how you can leverage Jscrambler’s Source Maps to achieve painless debugging of protected apps.

This time, we’re going to talk about one of Jscrambler’s most valuable capabilities: Client-Side Countermeasures. We will show you how to set up these countermeasures and highlight some common use cases where they help you ensure that your applications remain protected.

Countermeasures

As you’ve read in our previous 101 tutorials, two of Jscrambler’s protection layers are Code Locks and Self-Defending.

By locking your code to specific browsers, domains, OS’es, and date ranges, you can prevent someone from breaking the lock and trigger an action when a lock-breaking attempt is made.

The same goes for the self-defending module. This feature prevents someone from trying to debug the code or tamper with it and also enables you to trigger specific actions when these debugging/tampering attempts occur.

These actions, which we call countermeasures, come in seven flavors: Break Application, Custom Callback Function, Delete Cookies, Redirect, Real-Time Notifications, Self-Destruct, and Data Exfiltration Prevention. Let’s go over each of them.

Break Application

Breaking the application is Jscrambler’s default client-side countermeasure.

The way it works is straightforward: every time that someone tries to break a lock in your code or whenever the self-defending module is triggered, the application will completely stop working.

This behavior is always enabled on the self-defending module.

Custom Callback Function

This countermeasure gives you full control over the desired triggered action.

To get it to work, you need to have a specific function inside your original source code with the desired behavior. Then, you supply the name of that function when setting up the custom callback, and it will be triggered as a countermeasure.

Delete Cookies

The delete cookies functionality immediately deletes all end-user cookies that don’t have a path property set nor have been created with the HttpOnly flag.

We will cover a specific use case for this countermeasure further below.

Redirect

As the name implies, with this option you are able to automatically redirect the user to a specified URL, such as a warning page.

This countermeasure is supported for browser versions that were released after Internet Explorer 9 but can be adapted to earlier versions as described in our docs.

Real-Time Notifications

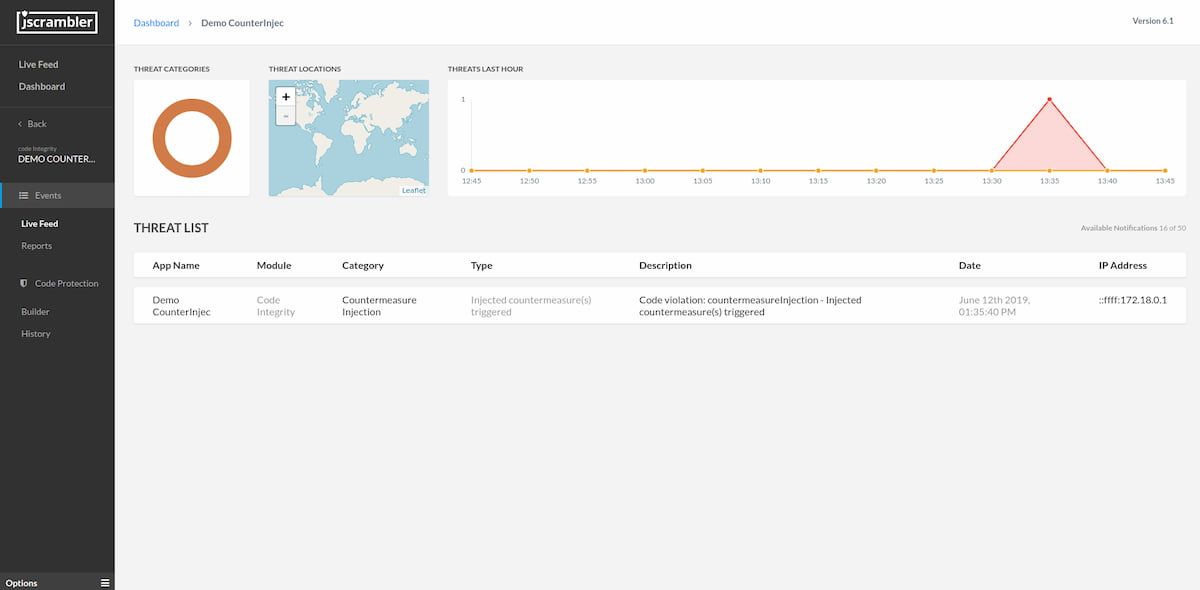
This countermeasure enables you to receive notifications in the Web App’s Live Feed whenever a violation occurs to the specified lock or self-defending code.

All instances contain details to enable a better understanding of each violation, as seen below:


Live-Feed-example- countermeasures-tutorial

Self-Destruct

Self-destruct enables going beyond breaking the app. A combination of actions, such as crashing the memory, destroying the session, and destroying objects, destroys your app and its environment for every malicious user – possibly even crashing the attacker’s machine.

Attackers will lose all progress in a reverse engineering attempt, including all data from the app’s memory and from objects.

Data Exfiltration Prevention

This countermeasure will block the application from sending data to external services as soon as it is triggered. It provides another layer for protecting sensitive data and preventing data leakage, which is especially useful when dealing with data protection use cases.

The Data Exfiltration Prevention works for browsers, Node.js, and hybrid applications (React Native, NativeScript, etc).

Setting Up Countermeasures

Specifying Countermeasures Globally

As we mentioned before, client-side countermeasures are triggered when one of two possible scenarios occurs: either when someone breaks a code lock or when the self-defending module is activated (during a tampering or debugging attempt).

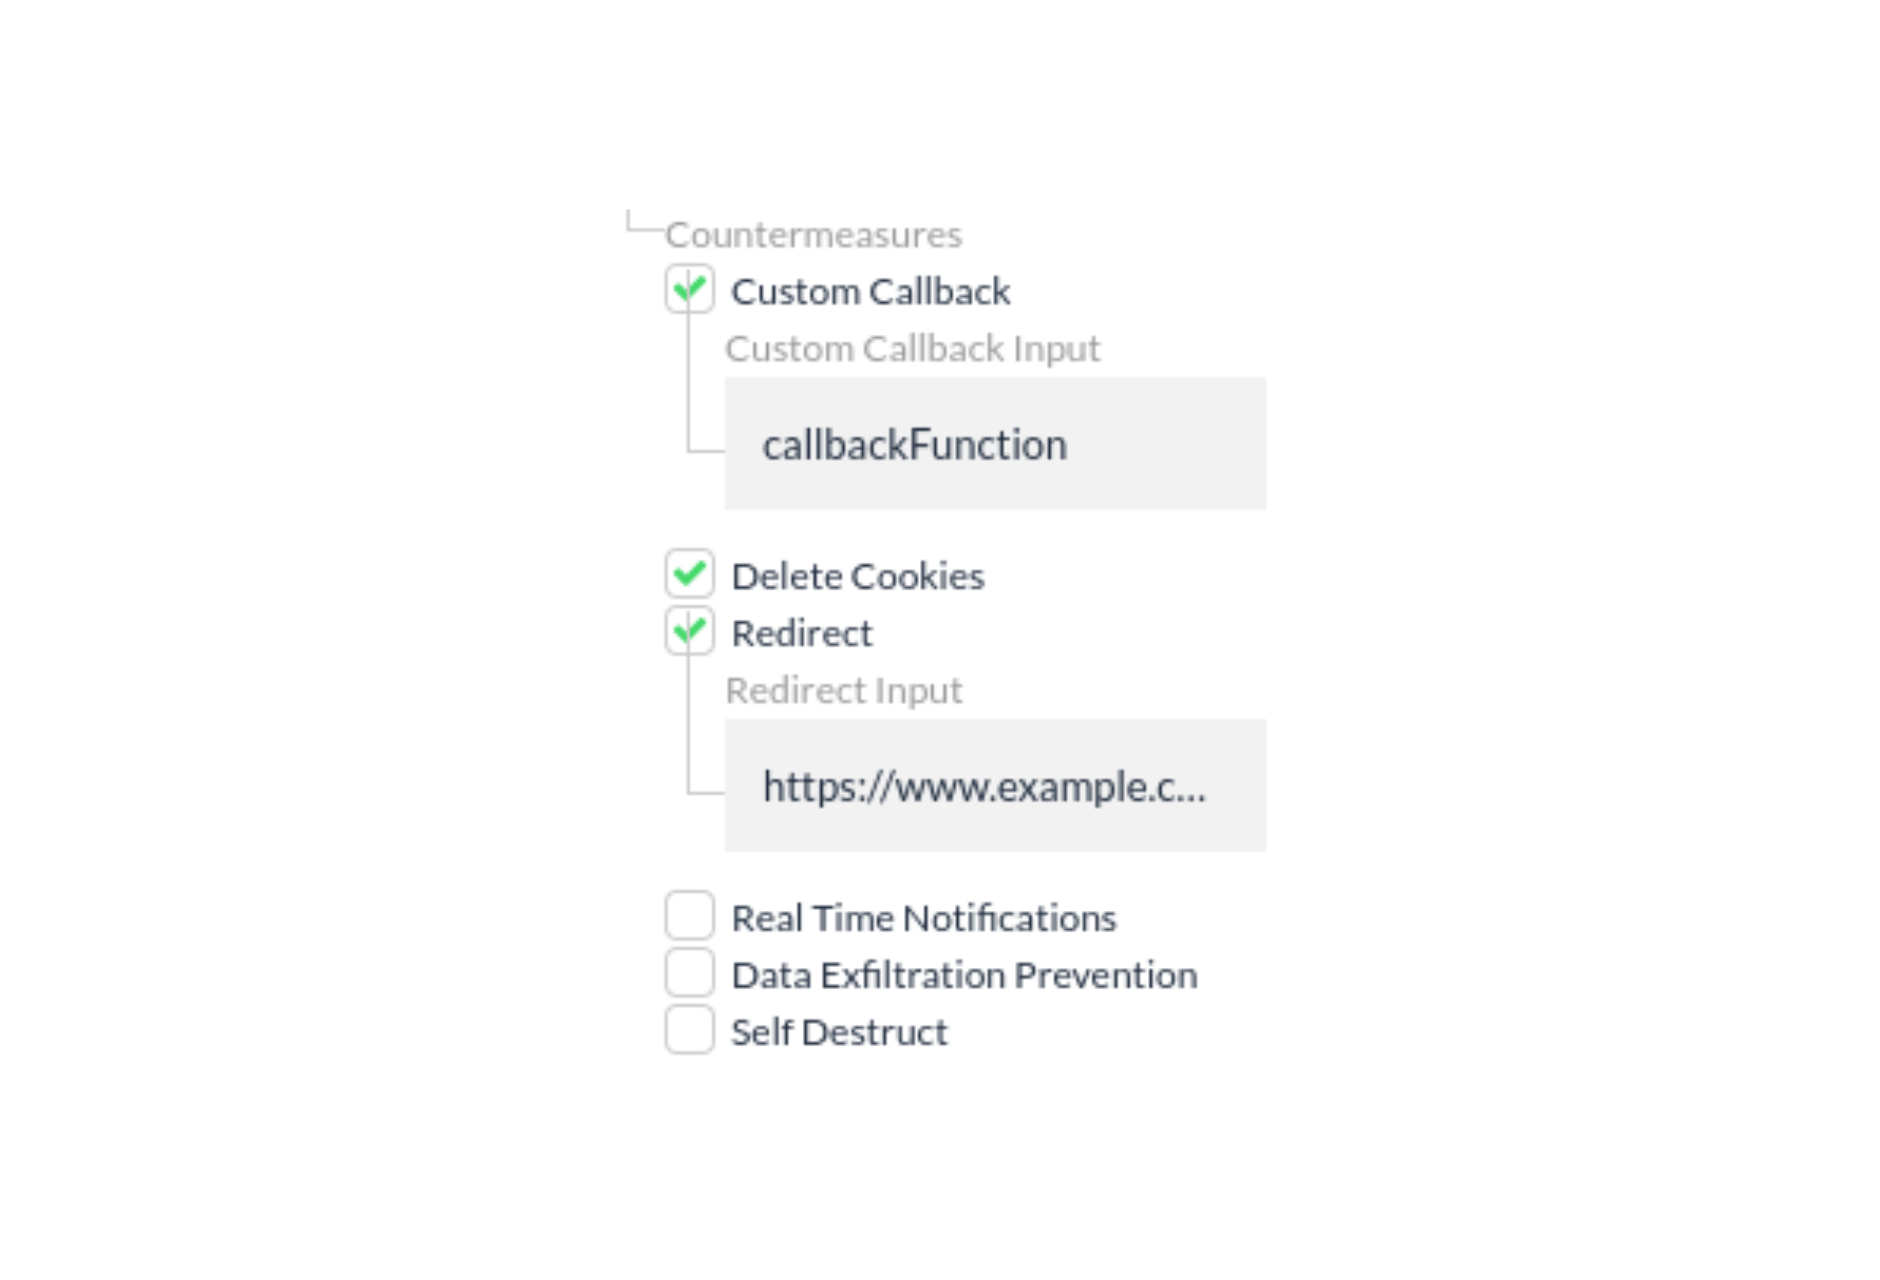
You can set up countermeasures easily via the Jscrambler Web App. When you’re on the screen with the application you want to protect, in the Fine-Tuning tab, ensure that you have selected either the self-defending feature or a code lock.

In either case, you’ll see a “Countermeasures” section, where you can specify which countermeasures you wish to apply.

Specifying-Countermeasures-Globally-jscrambler-code-integrity-tutorials

You can also set up countermeasures directly through the Jscrambler CLI and the Jscrambler packages for webpack and gulp. You can specify countermeasures directly in the Jscrambler configuration file, as shown below:


{
  "keys": {
    "accessKey": "myAccessKey",
    "secretKey": "mySecretKey"
  },
  "applicationId": "myApplicationID",
  "params": [
    {
      "name": "browserLock",
      "options": {
        "browsers": [
          "firefox"
        ],
        "countermeasures": {
          "customCallback": "callbackFunction",
          "deleteCookies": true,
          "realTimeNotifications": true,
          "redirect": "https://www.example.com",
          "breakApplication": true
        }
      }
    }
  ],
  "areSubscribersOrdered": false,
  "applicationTypes": {
    "webBrowserApp": true,
    "desktopApp": false,
    "serverApp": false,
    "hybridMobileApp": false,
    "javascriptNativeApp": false,
    "html5GameApp": false
  },
  "languageSpecifications": {
    "es5": true,
    "es6": false,
    "es7": false
  }
}


Specifying Countermeasures Locally

From Jscrambler 6.1 onwards, countermeasures can be specified and triggered for specific portions of the code by using Countermeasure Injection. This gives you additional control over countermeasures which you can tailor to your specific needs.

To set this up, you have to use code annotations like shown below:

// @jscrambler define countermeasureInjection { countermeasures: { breakApplication: 1, deleteCookies: 1 } } as cmi
// @jscrambler enable cmi

Note that, if you don’t specify countermeasures in this code annotation, only Break Application will be applied.

Countermeasures Use Cases

Now that we have covered what countermeasures are and how to set them up, let’s go through some examples of use cases where using Jscrambler’s countermeasures can be vital to ensure the security and integrity of your applications.

Redirect to the Warning Page

Sophisticated attacks like malvertising or adware try to redirect the users of a legitimate website to a malicious copycat page that asks for user credentials.

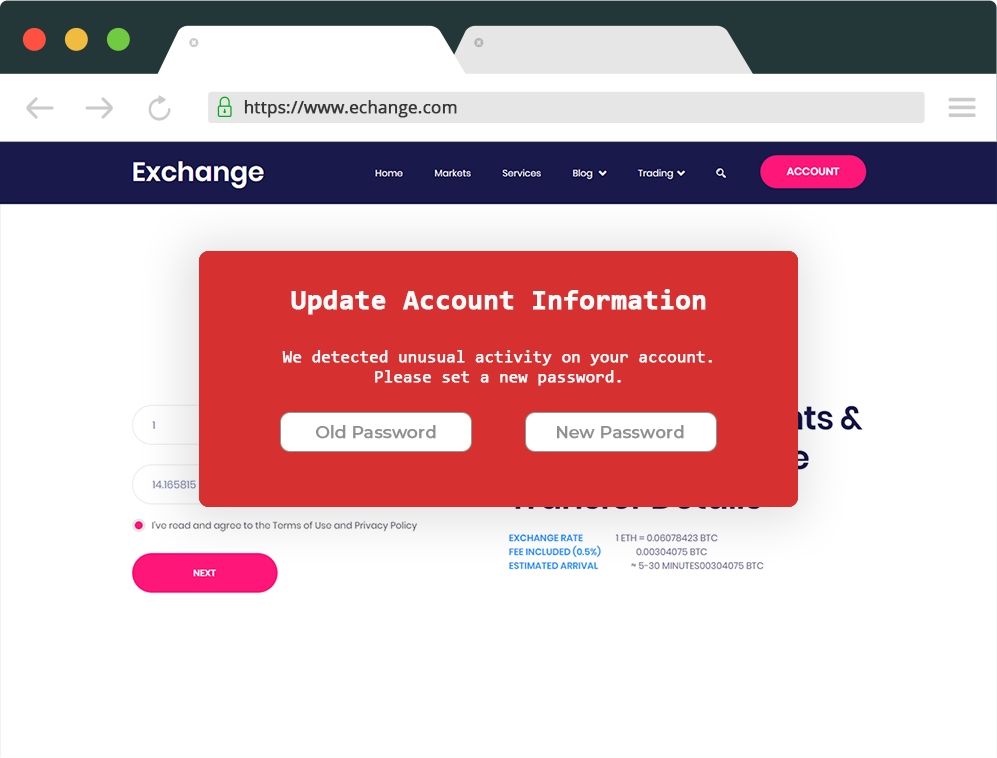
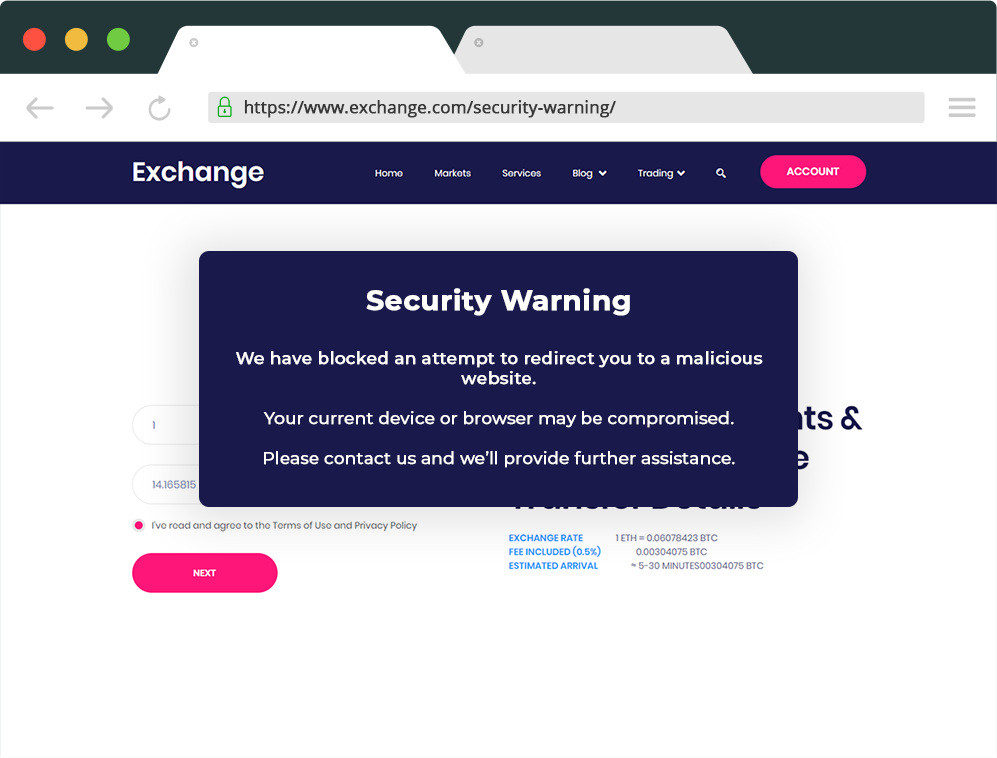
One such example would be a cryptocurrency exchange under the domain www.exchange.com. If some users have compromised devices (for example with a malicious browser extension), they may be redirected to an external website that is copying the original one (under a similar domain such as www.echange.com, and the same user interface).

The external website can display a warning asking the user to create a new password or to set up 2FA again. Users may be unaware of the malicious intent and insert the requested data, which is sent to attackers.

Example-of-PhishingNow, assuming that this cryptocurrency exchange was using a client-side monitoring solution like Webpage Integrity, it would be possible to set up an automatic redirect when such an attack is detected. So, infected end-users would not reach the malicious website and instead see a warning message such as the one shown below.
 

Example-Preventing-Phishing

Custom Callback to a SIEM

Picking up on the example above, a redirect to a warning page would be one of many viable countermeasures to be applied.

Another possible reaction mechanism would be to set up a custom callback to an SIEM, with the goal of sending an immediate alert to security teams whenever someone tries to run the code outside of the specified environment.

This would be a valid approach for any of the other locks (domain, OS, browser, and date range) and the self-defending feature as well.

Delete Cookies to Prevent Scraping

Several web apps require authentication in order to access user-specific pages. Imagine a social media platform or even a SaaS web app with a trial plan. In both cases, the user has to log in before accessing the platform’s content.

Automated scraping attacks may seek to obtain this (often private) information to feed it to an external platform or exploit the web app itself.

When the attack starts, Jscrambler’s anti-tampering features come into play, detecting the tampering attempt and enabling a countermeasure. In this case, an effective one would be to delete cookies — this would immediately end the user session and deny access to private pages.

Custom Callback to Prevent App Features Abuse

For this last use case, let’s consider an application with a free and premium mode, such as an HTML5 game.

While the “premium” state is often managed on the server-side, there are several cases where this must be done on the client-side, such as with offline apps.

In these cases, an attacker would be able to easily access the app’s core logic, which resides in the JavaScript code. Then, it’s a matter of time until the attacker is able to identify how the premium state is managed and force it to “premium” instead of “free”. This effectively grants the attacker a tampered version of the app with all the premium features, bypassing the need to pay in order to unlock them.

App developers could set up a custom callback when a tampering or debugging attempt is detected by Jscrambler.

A practical example of this scenario is the tampering of the “Space Shooters” game, which we detailed in our Jscrambler 101 — Self-Defending article.

Custom Anti-Cheat Mechanism with Countermeasure Injection

Let’s consider that you have a mobile game that implements a custom anti-cheat mechanism. When a cheater is detected, using a Jscrambler countermeasure injection, you could also set the code to supplement the custom anti-cheat actions with existing countermeasures:


if (detectCheat()) {
    customAntiCheat();
    // @jscrambler define countermeasureInjection { countermeasures: { breakApplication: 0, realTimeNotifications: 1 } } as cmi
    // @jscrambler enable cmi
}

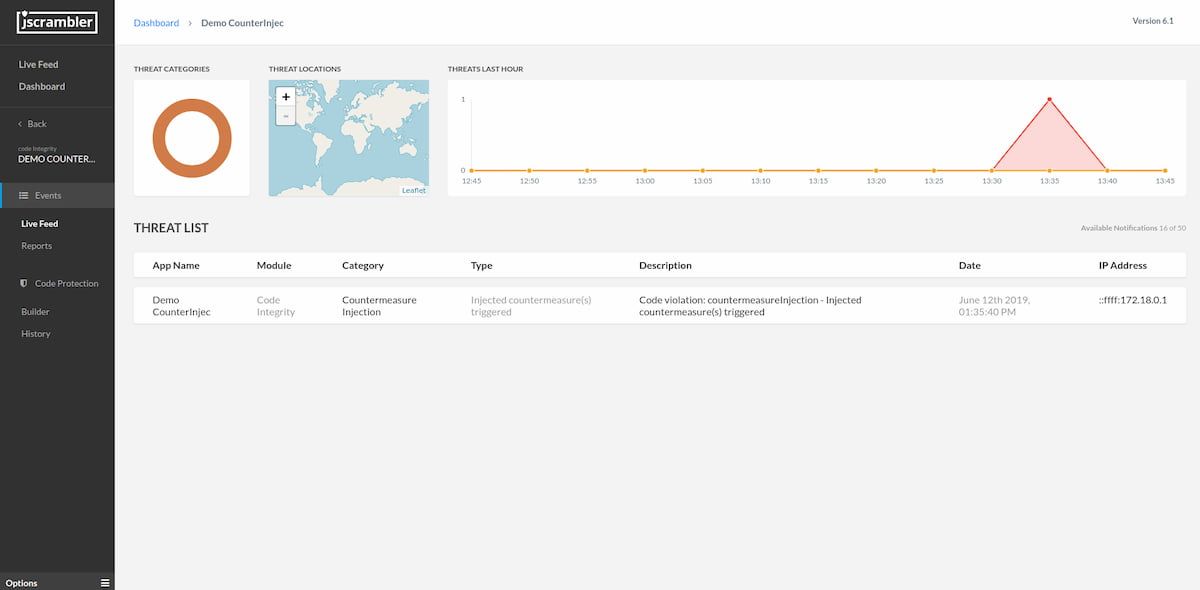
By setting realTimeNotifications: 1, every time this injected countermeasure is triggered, it will also appear in your Jscrambler Live Feed, with details of the incident.


Countermeasure-injection-live-feed

Conclusion

And we’re done! Now you can unleash the full power of using Client-Side Countermeasures to protect your applications.

Enjoy your testing and start protecting your Applications ASAP! If you have any additional questions, feel free to contact us.