Need: Compliance Enforcement

Top European Airline Ensures Stellar Client-Side Protection with Jscrambler

Top European Airline Ensures Stellar Client-Side Protection with Jscrambler
Jscrambler’s advanced script and form security protection ensures sensitive form data is protected and malicious scripts cannot load.

Overview

This European airline is a global leader in air transportation that operates an extensive flight network connecting Europe to the world through its hubs in European capitals. With over 70,000 dedicated employees and a commitment to diversity, the airline serves millions of passengers across 300 destinations in 120 countries. A large portion of these passengers uses the company’s websites and mobile apps to book flights, check in online, chat with customer service, and redeem loyalty points.

Challenge

The client’s decision to search for client-side protection technology was initially triggered by a credit card data breach at another airline.

Before implementing Jscrambler, the client relied on more traditional security processes that involved checklists and paperwork. However, this manual approach left room for vulnerabilities: “We had security people who could decompile libraries, but they were usually too busy to do it.”.

When the client’s team needed to go fast and add new scripts, innovation sometimes took priority, which meant they would find workarounds to circumvent the documentation-heavy process, leaving them potentially open to attack.

Solution

In search of a comprehensive JavaScript monitoring and protection solution, the client considered various factors, including features and cost. Jscrambler stood out as the only solution that met their security requirements.

The client was particularly impressed by Jscrambler’s Form Fencing feature, which offers fine-grained behavioral control over third-party tag access to form data based on high-level assumptions and user-defined rules. Unlike other solutions, Jscrambler allowed the airline to authorize or block scripts individually.

The company put Jscrambler’s Webpage Integrity solution to the test in multiple Magecart attack scenarios. They ran dozens of tests to see if the solution could detect if content was added, modified, or removed from pages illicitly (DOM tampering), if form events were poisoned, or if data was exfiltrated to a drop server. Jscrambler’s technology passed every single test with flying colors and outperformed all the other available solutions. Adding Jscrambler to a page had little to no impact on its performance.

“Other solutions allow you to monitor cross-site scripting or visit CSP policies, but that’s all they do. They won’t protect forms. They won’t ask, “Is this sensitive data? Yes or no?” For us, Jscrambler was the best platform because they do it all.”

Information Analyst and Product Owner Mobile at Top European Airline

“With most companies, you buy a product, you get support for one or two months, and then you’re on your own. But with Jscrambler, we meet regularly twice a month. We know when new features are coming, even if they haven’t been released yet because they’ll tell us about them on our call and ask us what we think. It’s a nice dialogue to have. You really feel the personal touch. Jscrambler’s customer support is definitely a big plus.”

Information Analyst and Product Owner Mobile at Top European Airline

Top Jscrambler Features and Capabilities

Full Visibility and Control

Form Fencing

PCI DSS Compliance

Results

With zero security incidents, increased efficiency, and peace of mind, Jscrambler has become an integral part of the airline’s strategy for maintaining the highest security standards in today’s evolving digital landscape. The client attests, “We sleep easier at night because we know that the people at Jscrambler are looking out for us and our clients.”

Download Case Study

Jscrambler Helps Neobanks Protect JavaScript

How Neobanks Strengthen Client-Side Security with Jscrambler
Several of the world’s leading neobanks and challenger banks turned to Jscrambler to strengthen the security of their web applications as digital channels became central to customer experience and revenue growth. Operating in highly regulated environments and handling sensitive financial data at scale, these institutions needed to protect their client-side JavaScript from reverse engineering,
tampering, and logic abuse.

Overview

Neobanks defy traditional banking by betting everything on digital and delivering customer-centric services for payments and money management. Today, over 90% of consumer interactions with banks are digital. Neobanks typically release new features more frequently, often every few weeks, while traditional banks tend to take several months to bring similar innovations to market. As a result, user satisfaction ratings for neobanks in the US (63%) are higher than those of traditional banks (55%).

Neobanks’ technological flexibility stems from investing in cloud-based infrastructure and advanced web and mobile applications built with modern JavaScript frameworks such as React Native. With this approach, they cut product development cost and time, paving the way for rapid iteration and innovation. This is greatly aided by relying on third-party integrations rather than developing every piece of code in-house. In software development, pursuing agility and speed often means widening security gaps. Despite JavaScript’s numerous advantages, neobanks must be aware that client-side JavaScript is exposed and can be used to launch attacks, including intellectual property theft, code tampering, application abuse, and data exfiltration. Unless protected with an enterprise-grade solution, this exposed JavaScript poses a key business threat.

Challenge

In recent years, several neobanks from North and South America, Europe, and Asia have approached Jscrambler due to significant security challenges. With web and mobile apps built with JavaScript — and a strong adoption of cross-platform frameworks for mobile development like React Native and Ionic — security teams understood early on that client-side logic would pose a significant security risk. There was a high likelihood of having to run sensitive logic on the client-side, so it became paramount to ensure that this logic would be concealed using the most potent and resilient technology available today. It was also mandatory to ensure that automated reverse-engineering tools would always fail to reverse the concealed code, while making it extremely unfeasible for attackers to achieve it manually. As these neobanks’ apps would handle sensitive services, another key challenge was ensuring that malicious actors couldn’t tamper with the code. JavaScript had to react in runtime to mitigate these attacks. And since both the web and mobile apps would handle sensitive data, such as credentials, personally identifiable information, and financial details, an additional pre-eminent requirement was to ensure that JavaScript couldn’t serve as a gateway for attackers to steal user data.

With each neobank offering multiple applications to their end customers, it was also essential to ensure that JavaScript protection would integrate seamlessly with their CI/CD and integration testing. Finally, in such a heavily regulated sector, another significant challenge was achieving compliance with regulations such as PSD2, NIST, the PCI DSS requirements 6.4.3 and 11.6.1, and specific requirements for operation like those of Bank of Brazil, for example, with a special focus on client-side attacks.

Solution

To meet the highest standards for JavaScript protection, these neobanks sought a holistic solution that would fit their processes and scale. Jscrambler presented a mature, proven client-side security product suite that, like noobanks themselves, is defined by continuous innovation.

The first step towards securing JavaScript was Jscrambler’s polymorphic obfuscation. With this critical security layer, all of the source code of neobanks’ apps was concealed beyond possible recognition. Jscrambler’s set of the most potent and resilient transformations was key to guaranteeing cutting-edge obfuscation. Its inherent polymorphism ensured that each new code deployment would be completely different—an extra line of defense against reverse-engineering attempts. For example, one of the banks had their fingerprinting script collect information from the session/browser, and wanted to protect it as it was exposed. Jscrambler provided the neobank with advanced polymorphic obfuscation to allow it to serve its fingerprinting script (practically unique) in each user session.

Security teams implemented critical OWASP recommendations, including the OWASP Mobile Top 10, which highlights that “to prevent effective reverse engineering, you must use an obfuscation tool” and that “the app must be able to react appropriately at runtime to a code integrity violation.” At the same time, they ensured compliance with PSD2 mandates, including transaction monitoring and strong customer authentication, as well as PCI DSS v4 requirements to safeguard payment pages and credit card data from client-side tampering. In addition, they aligned their client-side security measures with NIST guidelines, strengthening code integrity, runtime protections, and risk management practices in line with industry-standard cybersecurity frameworks. Jscrambler mostly worked with Security Engineers at these banks who were well aware of the problem and the required steps for solving it. After the initial setup of the Jscrambler instance, it took on average 2 weeks and 2 meetings with Jscrambler’s engineers to integrate Jscrambler seamlessly into their CI/CD pipeline. From there, Jscrambler became an automated part of their application build process.

Top Jscrambler Features and Capabilities

  • Polymorphic obfuscation
  • Anti-Tampering
  • Compliance with financial regulations and standards

Results

Securing JavaScript code requires awareness of the threats posed by exposing important logic on the client-side. Neobanks have had this pain from the very start of the business, as their main assets depend on it. By opting for Jscrambler’s proven JavaScript protection technology, product teams met their primary requirement: integrating a code protection solution seamlessly into their CI/CD. Now, these neobanks deploy secure code to production, knowing that each build has a fresh set of the most potent and resilient JavaScript protection available today. Jscrambler helped neobanks rethink key and critical data management in the applications, moving keys into JavaScript and applying Jscrambler Code Integrity to protect them effectively.

Through advanced obfuscation techniques, anti-debugging protections, and tamper detection, the solution prevented key theft, code tampering, and reverse engineering, ensuring the web application remained protected even when running on the client side. For management, safeguarding their applications’ source code from reverse engineering and tampering translates into a clear competitive advantage. Investors also recognized the reduced liability associated with exposed JavaScript in neobanking; with Jscrambler, these banks strengthened their position in future funding rounds and earned the trust of millions of potential customers. In a results-driven industry, the outcome was unequivocal: 0 integration issues, 0 successful attacks on JavaScript code.

How Bionano Genomics Increased Compliance with Regulations Using Jscrambler

Bionano Increases Compliance with Regulations Using Jscrambler
Jscrambler provided Bionano with the most resilient JavaScript protection and satisfied the regulatory requirements for code protection.

Overview

Bionano is a biotechnology company specializing in genome mapping and analysis and can enable researchers and clinicians to reveal answers to challenging questions in biology and medicine. Bionano’s mission is to transform how the world sees the genome through optical genome mapping (OGM) solutions, diagnostic services, and software. Bionano also offers an industry-leading, platform-agnostic genome analysis software solution and nucleic acid extraction and purification solutions using proprietary isotachophoresis (ITP) technology.

Challenge

Each time Bionano engages in an enterprise-level clinical environment, they are subjected to a rigorous security audit. By interacting with many security organizations globally, they gained an in-depth understanding of what these security organizations expected.

Bionano chose Node.js as its visualization platform as it facilitated reaching the widest audience of users (macOS, PC, and Linux). It also provided an extensive array of visualization tools such as D3js, ThreeJS, and ChartJS that allow the creation of rich interactive genomic maps for customers to explore. Bionano software is free to encourage the use of Saphyr-generated data. Anyone can download and start their own Bionano Access Server. Bionano needed a way to protect their downloaded client and server-side JavaScript logic to satisfy multiple security regulations

Solution

The Bionano system itself is designed not to hold protected private information (PPI), so the company did not face significant liability to be concerned with. However, as an extra precaution and to be as compliant as possible, the company understood the need for JavaScript code protection. In search of the optimal solution, Bionano tested some JavaScript obfuscation solutions but found out that these could be easily reversed or debugged. Jscrambler was the only solution that passed all their tests and which they could not reverse.

This implementation of Jscrambler was greatly derived from the need to comply with several different regulatory requirements. In the specific case of Bionano, the regulations that apply to their clinical customers vary depending on their local principalities. Some regulations, like ISO 27001 and 27002, specifically require source code protections, while others have more general data protection and/or encryption requirements.

Jscrambler does not solve all of Bionano’s security concerns, but it provides what the company needs to protect the source code enough to satisfy all regulations in that regard. Then, there’s also the matter of protecting intellectual property. Bionano’s system provides comprehensive genomic variation data for review.

“Jscrambler was the only product we found that could not be cracked.”
Scott Way

Director of High-Performance Computing and Genome Visualization at Bionano

“We needed our Node.js application protected to satisfy multiple data protection regulations in customer clinical environments. Jscrambler did that for us, and it was easy to incorporate into our tech landscape.”
Scott Way

Director of High-Performance Computing and Genome Visualization at Bionano

Top Jscrambler Features and Capabilities

  • Resilient JavaScript obfuscation
  • Built-in protection against reverse-engineering tools
  • Anti-tampering and antidebugging capabilities

Results

Thanks to the source code protection provided by Jscrambler, Bionano now obfuscates its code and can prevent debugging. This allows them to satisfy the security concerns of their clinical customers and continue using the platform that gave them the best value.

Securing One of the Biggest E-Commerce Websites with Jscrambler

Securing One of the Biggest E-Commerce Websites with Jscrambler
In a landscape where cyber threats are constantly evolving, the Fortune 500 Retail Company’s success with Jscrambler serves as a testament to the efficacy of dedicated client-side protection.

Overview

Established in the 1960s, this client is an iconic American brand boasting four flagship labels. The company recently also expanded its portfolio. As a Fortune 500 company, the company’s commitment to innovation extends beyond the retail industry, delving into the digital realm with a strong online presence and a high-traffic e-commerce platform.

Challenge

In the past decade, the client’s e-commerce traffic has soared, paralleling the rise in online shopping. However, this increase also attracted more frequent and more sophisticated cyber threats. The company witnessed a surge in malicious scripts targeting customer data through various methods, including keylogging, card skimming, and credential hijacking. Confronted with this escalating threat, the client sought robust client-side security solutions to shield its web applications.

The retailer’s broad digital exposure, especially during peak shopping periods like Black Friday, left them vulnerable to attack vectors like JavaScript data exfiltration and script hijacking. To counter these threats, the client required a system that provided comprehensive control to mitigate these kinds of attacks. Additionally, their collaborations with third-party vendors necessitated a security tool that could precisely regulate the data accessible to these third-party tags.

Solution

The retailer sought the right solution to secure its client-side applications against the evolving threat landscape. For an e-commerce platform of their scale, they needed more than just the basics.

The retailer required a security solution that would continue to monitor their website just as effectively in real-time and take appropriate automated action against threats, regardless of traffic volume. Flexibility was equally crucial, especially the ability to restrict data access through form fencing and to oversee all data points on their site comprehensively. Moreover, swift response times were imperative, as the retailer’s success hinged on transforming website visits into sales through an exceptional user experience.

The client’s criteria extended to adaptability and enduring protection. After a thorough evaluation, the retailer identified Jscrambler as the sole contender to meet all of their stringent criteria. Jscrambler’s R&D continuously monitors emerging threats, ensuring the platform evolves to effectively react to the ever-changing cyber threat environment.

As the final deal clincher, Jscrambler gave the retailer a security tool fully focused on client protection. The team already had security tools in their arsenal but didn’t want to rely solely on default security features or add-ons to existing solutions. They believed strongly in a clear separation of responsibilities and were specifically looking for a platform that focused solely on client-side protection, independent of their web application firewall, tag manager, and other existing tools.

“With the kind of traffic we see, data protection for JavaScript, the ability to stop data exfiltration, and field-level protection for sensitive information like credit card details and PII are just the beginning. We also need a solution that can scale up and continue to perform optimally as our business grows. This is absolutely critical.”
Director of Product Security at the Fortune 500 Retail Company

“With Jscrambler, we can maintain the level of security that is critical to running a multinational business and preserving our customer’s trust. The unique layer of security it adds is definitely an integral part of our defense strategy. I’d highly recommend Jscrambler to any other business with a full-blown e-commerce platform that hosts millions of customers daily.”
Director of Product Security at the Fortune 500 Retail Company

Top Jscrambler Features and Capabilities

  • Comprehensive client-side protection
  • Real-time threat mitigation
  • Real-time alerts and reporting

Results

Adopting Jscrambler has provided the retailer with several benefits. Protection from Magecart and skimming risks is crucial for e-commerce platforms, and having Jscrambler covering them on this front helps the client breathe a little easier. They know that sensitive data is protected from exfiltration and hijacking when customers shop on the retailer’s website and that banking and PCI information will remain secure.

Scentbird Ensures Customer Trust with the Jscrambler PCI DSS solution

Scentbird Ensures Customer Trust with the Jscrambler PCI DSS solution
Scentbird takes a proactive approach to PCI DSS v4 compliance and protects its payment page with Jscrambler’s compliance solution.

Overview

Scentbird is a subscription service for perfumes, colognes, candles, and car fresheners. Scentbird was founded in NYC in early 2013 and established as a subscription business in 2014. Scentbird enables its users to choose and receive a supply of sample designer fragrances monthly before buying them. It has grown to have more than 700,000 active subscribers.

Challenge

Scentbird has been developing its e-commerce subscription platform in-house. That came with handling many things, including security and compliance and working with multiple payment providers. One of the things that were being asked from one of the payment providers was to be PCI DSS compliant. Aside from that, it was essential for Scentbird to ensure that its audience could trust Scentbird with its data. Andrei Rebrov, CTO & Co-Founder at Scentbird, shares, “The customers should safely leave their credit card information on our website. If people think something is wrong, they will feel unsafe, and there will be no conversion. And if there’s no conversion, there is no revenue.” The Scentbird team realized that with the upcoming change in PCI DSS, they needed a proper way to comply with the specific requirements 6.4.3 and 11.6.1.

The team’s most important question was what was going on with the customer data. Traditional cookie consent management platforms didn’t track who interacted with which form, the changes inside the scripts, or what kind of data was being transmitted outside.

Scentbird mission is to give users fragrance recommendations and personalizations. So, Scentbird has to collect information about the customer and share this information with marketing platforms to fuel personalization. So, it was essential to achieve a balance between the information they gathered, how they treated it, and how they controlled the third-party scripts on their website. They needed a solution to help them control third-party scripts without spending too much time tending to minor changes.

Solution

The Scentbird team first examined several cookie consent management tools that offered PCI DSS compliance. However, they didn’t provide a proper solution and couldn’t answer any specific PCI DSS questions. Another category of solutions they looked at were big enterprise platforms (CDNs, WAFs) that would cost a lot of money and would have you undergo a rigorous integration process. Moreover, Andrei, Scentbird’s Co-Founder, noted that while the major platforms often release features aligned with their general protection offerings, they do not delve deeply into specific matters like PCI DSS v4 compliance.

It was clear to the Scentbird team what they needed to do. Andrei notes, “The Jscrambler team explained how the integration would work, how to prepare for the audit, how to view the rest of the inventory, how notifications about specific changes would be received, how those changes would be reflected, and how we should respond. I appreciate this in a partner—they provided a clear protocol and outlined exactly what I needed to do. I had no additional questions and felt confident about using the product properly.” Andrei shares that it was quite easy to implement the solution, and there were no major obstacles.

“So what starts as a list of around 60 different scripts and pixels and sort of interactions with a third party, might be the list of 100 more with the dependencies. And then when you start looking at the scripts for the past 30 days, you will see a huge list with one script that has changed the version every other day. It’s a minor change, but it’s very annoying.”
Andrei Rebrov

CTO & Co-Founder at Scentbird

“I didn’t want to spend a lot of time having someone on my team manage this. So, I was looking for something I could implement once to ensure we are protected. If something new comes up, the team will reach out to notify me about changes and any actions I need to take, allowing us to focus on what we do best: selling fragrances.”
Andrei Rebrov

CTO & Co-Founder at Scentbird

Top Jscrambler Features and Capabilities

  • PCI DSS v4 compliance status with the Jscrambler Agent
  • Convenient alert mechanisms for PCI DSS compliance
  • Ease of use and quick implementation

Results

Scentbird became PCI DSS-compliant in early 2024, well ahead of the 2025 deadline and earlier than many e-commerce companies. When asked why Scentbird chose Jscrambler, Andrei mentioned the delivery of what they needed to be PCI DSS-compliant, quick implementation, and the quality of the Jscrambler team’s support.

Jscrambler WPI 101 – AI Assistant

For many, client-side security under PCI DSS v4 has evolved into a massive operational burden. With requirements 6.4.3 and 11.6.1 mandating the authorization and integrity of every script on payment pages, security analysts are drowning in a sea of script approvals.

Jscrambler’s AI Assistant is designed to cut through this noise. Integrated directly into the Webpage Integrity (WPI) PCI DSS dashboard, it serves as an expert analyst, helping you validate the legitimacy of scripts running in payment pages, detect Magecart skimmers, and maintain PCI DSS v4 compliance with minimal effort and maximum confidence.

This guide outlines the general workflow for using the AI Assistant: Reviewing Insights, Deep-Dive Investigation, and Taking Action.

Step 1: Access AI Insights

To get started, in your dashboard, navigate to Vendor Services in the PCI DSS dropdown. Here, you will see a list of all scripts running on your payment pages. Select the “needs review” filter to see every new script, or existing script that has changed its behavior, awaiting your review.

Access AI Insights

To open up the AI insights panel, click on the vendor you would like to review, and the panel will open on the right-hand side.

Step 2: Initial Review with AI Insights & Recommendations

The Jscrambler AI Assistant performs a real-time analysis by cross-referencing detected behaviors, automated security evaluations, and known vendor purposes. The AI then determines if the script’s activity aligns with its stated function to provide tailored risk insights and recommendations.

The AI flags any newly detected behaviors, such as accessing form data ( like payment information), connecting to external domains, or creating cross-origin iframes. It then performs security checks to determine whether this is legitimate script behavior or indicative of a threat, such as a web skimmer.

  • For Safe Behaviors: If the detected activity, such as network connections or iframe control, matches the known purpose of a vendor, the AI Assistant will recommend that you authorize and provide the specific permissions and actions that it should be allowed to perform.

Initial Review with AI Insights & Recommendations

  • For Abnormal Behaviors: If the script exhibits behaviors outside its expected purpose, such as an analytics tool suddenly accessing sensitive form data or transferring information to an unauthorized domain, it is flagged as a potential skimmer, and the AI will recommend blocking these specific behaviors immediately to mitigate the threat.

Step 3: Investigate Further with the AI Chat Assistant

If the initial insights are enough for you, you can finish the review and apply the recommended permissions to the vendor. But if you need more context before making a decision, click the Analyze with AI button.

This opens a chat interface where you can query the AI assistant directly (using pre-built suggestions or your own unique query) to validate your assumptions or scope a threat.

Investigate Further with the AI Chat Assistant

Validating Assumptions

For new vendors, you can ask general questions to confirm legitimacy:

  • “Tell me more about Stripe.”
  • “What additional risks are there with this script?”

Validating Assumptions

Investigating Impact

For suspicious scripts, you can use the AI to understand the scope of an attack:

  • “How many customers might have been impacted by this malicious script?” (The AI can query session data to provide exact numbers, e.g., 10,000 sessions).
  • “What is the reputation of the target domains?” (The AI can identify unauthorized domains, confirming if data is being exfiltrated to a malicious URL).

Step 4: Remediation and Justification

The final stage of the workflow is taking action. The AI Assistant streamlines the compliance paperwork and technical configuration required for PCI DSS v4.

Automating Justification

When authorizing a vendor, the AI Assistant pre-populates the Justification field required for audits. It uses the insights gathered to write the note for you, ensuring consistent and accurate record-keeping. You remain in full control to edit this text or switch it off.

Applying Restrictions

When handling a threat, the Jscrambler AI Assistant can help you decide the correct granular permissions to set.

Unlike other solutions that apply an all-or-nothing approach to blocking scripts (potentially breaking page functionality), you can follow the AI’s recommendation to block specific behaviors (such as network transfers or form data access) while leaving non-malicious script behaviors active that may be necessary for the page’s operation.

Simply click Save to apply your decisions and complete the review.

Applying Restrictions

Comply with Confidence

By following this workflow, you can use the Jscrambler AI to transform client-side security from a manual, error-prone task into a streamlined, data-driven process. The Jscrambler AI Assistant ensures that whether you are approving a new payment provider or mitigating an active skimmer, every decision is backed by expert intelligence.

Jscrambler WPI 101 — Skimming Detection

Welcome back to the WPI blog series! Jscrambler WPI 101 is a series of articles about Jscrambler’s product Webpage Integrity (WPI), its main use cases, innovative features, and tips on maximizing the product’s benefits.
This article focuses on the WPI use case for Skimming Detection and explains how Webpage Integrity enables you to protect your business against web skimming and data leakage.

The Dangers of Web Skimming

As web skimming attacks become more sophisticated, businesses face increasing pressure to secure their client-side environments, especially on sensitive pages like payment pages and login portals. Skimmers often operate silently, injecting malicious scripts into third-party code or exploiting weak points in the browser to siphon off personal and financial data without ever being detected.


To combat this, Jscrambler’s WPI Skimming Detection provides a proactive line of defense. Leveraging advanced static code analysis, it inspects every script running on your website, evaluating not just the code itself but how and where it executes. The system is designed to identify behaviors commonly associated with skimming, such as obfuscation, data encryption, unauthorized form injections, and access to sensitive information.


When a potential skimmer is detected, the Jscrambler platform offers detailed visibility into the threat, including which third-party vendors are involved and where the skimmer was found. This visibility empowers security teams to act quickly and precisely, removing the threat before any damage is done.


Preventing Digital Skimming with Jscrambler

The Jscrambler Skimming Detection engine aims to classify every individual third-party script present on a website and determine whether a potential skimmer is behind it.


The skimming detection capabilities within the Jscrambler dashboard are slightly different depending on whether you’re using the full Webpage Integrity (WPI) product or a PCI DSS Module of the WPI. However, they pursue the same goal—helping you eliminate skimming risks to zero.


Inventory

A good way to get an instant overview of skimming threats is to check the Inventory in the WPI dashboard. The Inventory feature provides comprehensive visibility into all vendors and their scripts on the website, offering a better understanding of the various scripts in use. It allows users to identify the scripts’ purpose, location, and impact on sessions and assess the associated level of risk based on verified actions and the potential types of threats they pose.
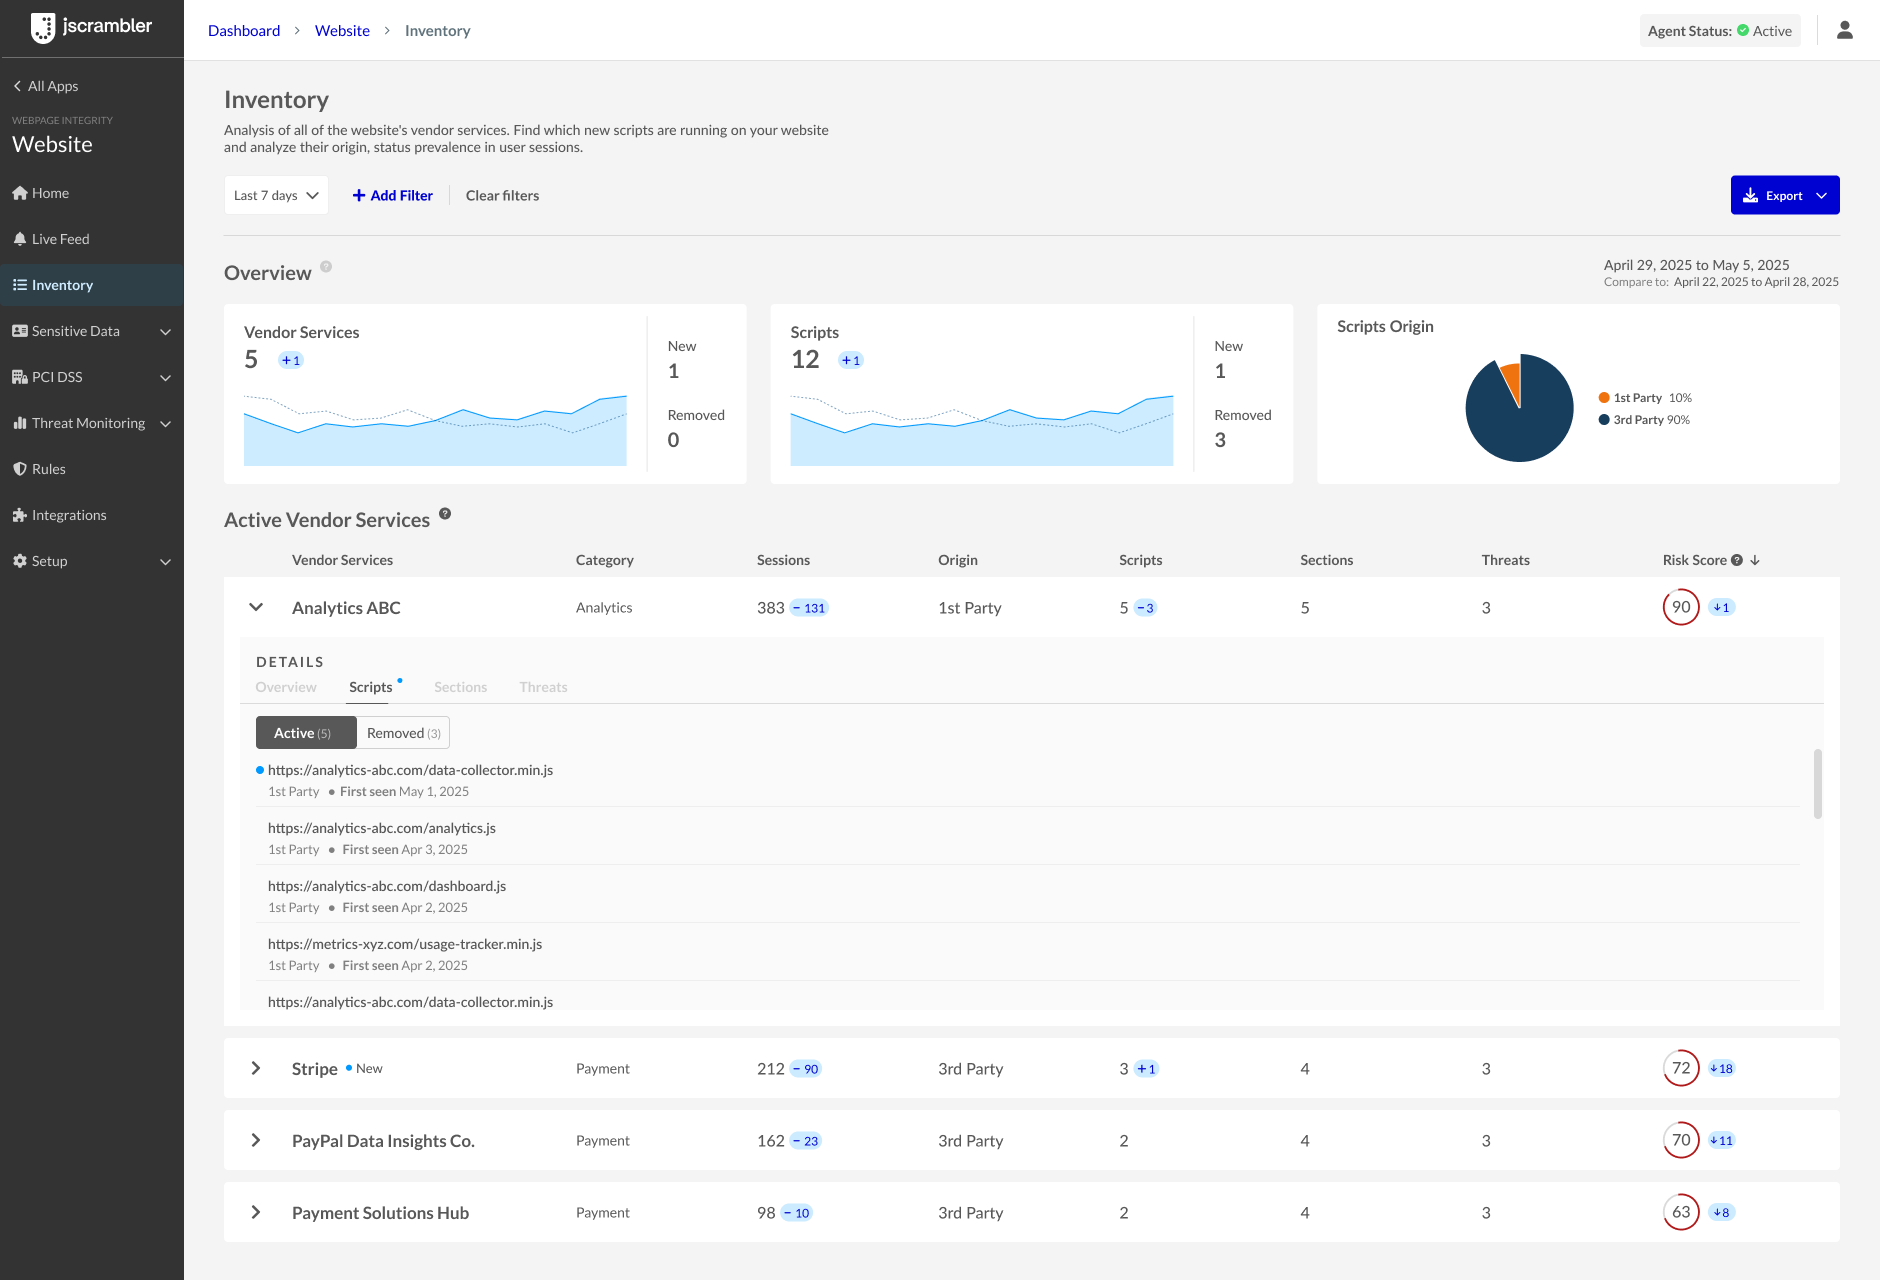
 

example-of-inventory-view-with-no-skimming-issuesAn example of an Inventory view with no skimming issues identified.

This goes beyond simply raising awareness of threats. The Inventory dashboard presents a qualitative measure that helps prioritize security actions and implement mitigation measures to address the impact of vendors present and active on the website.
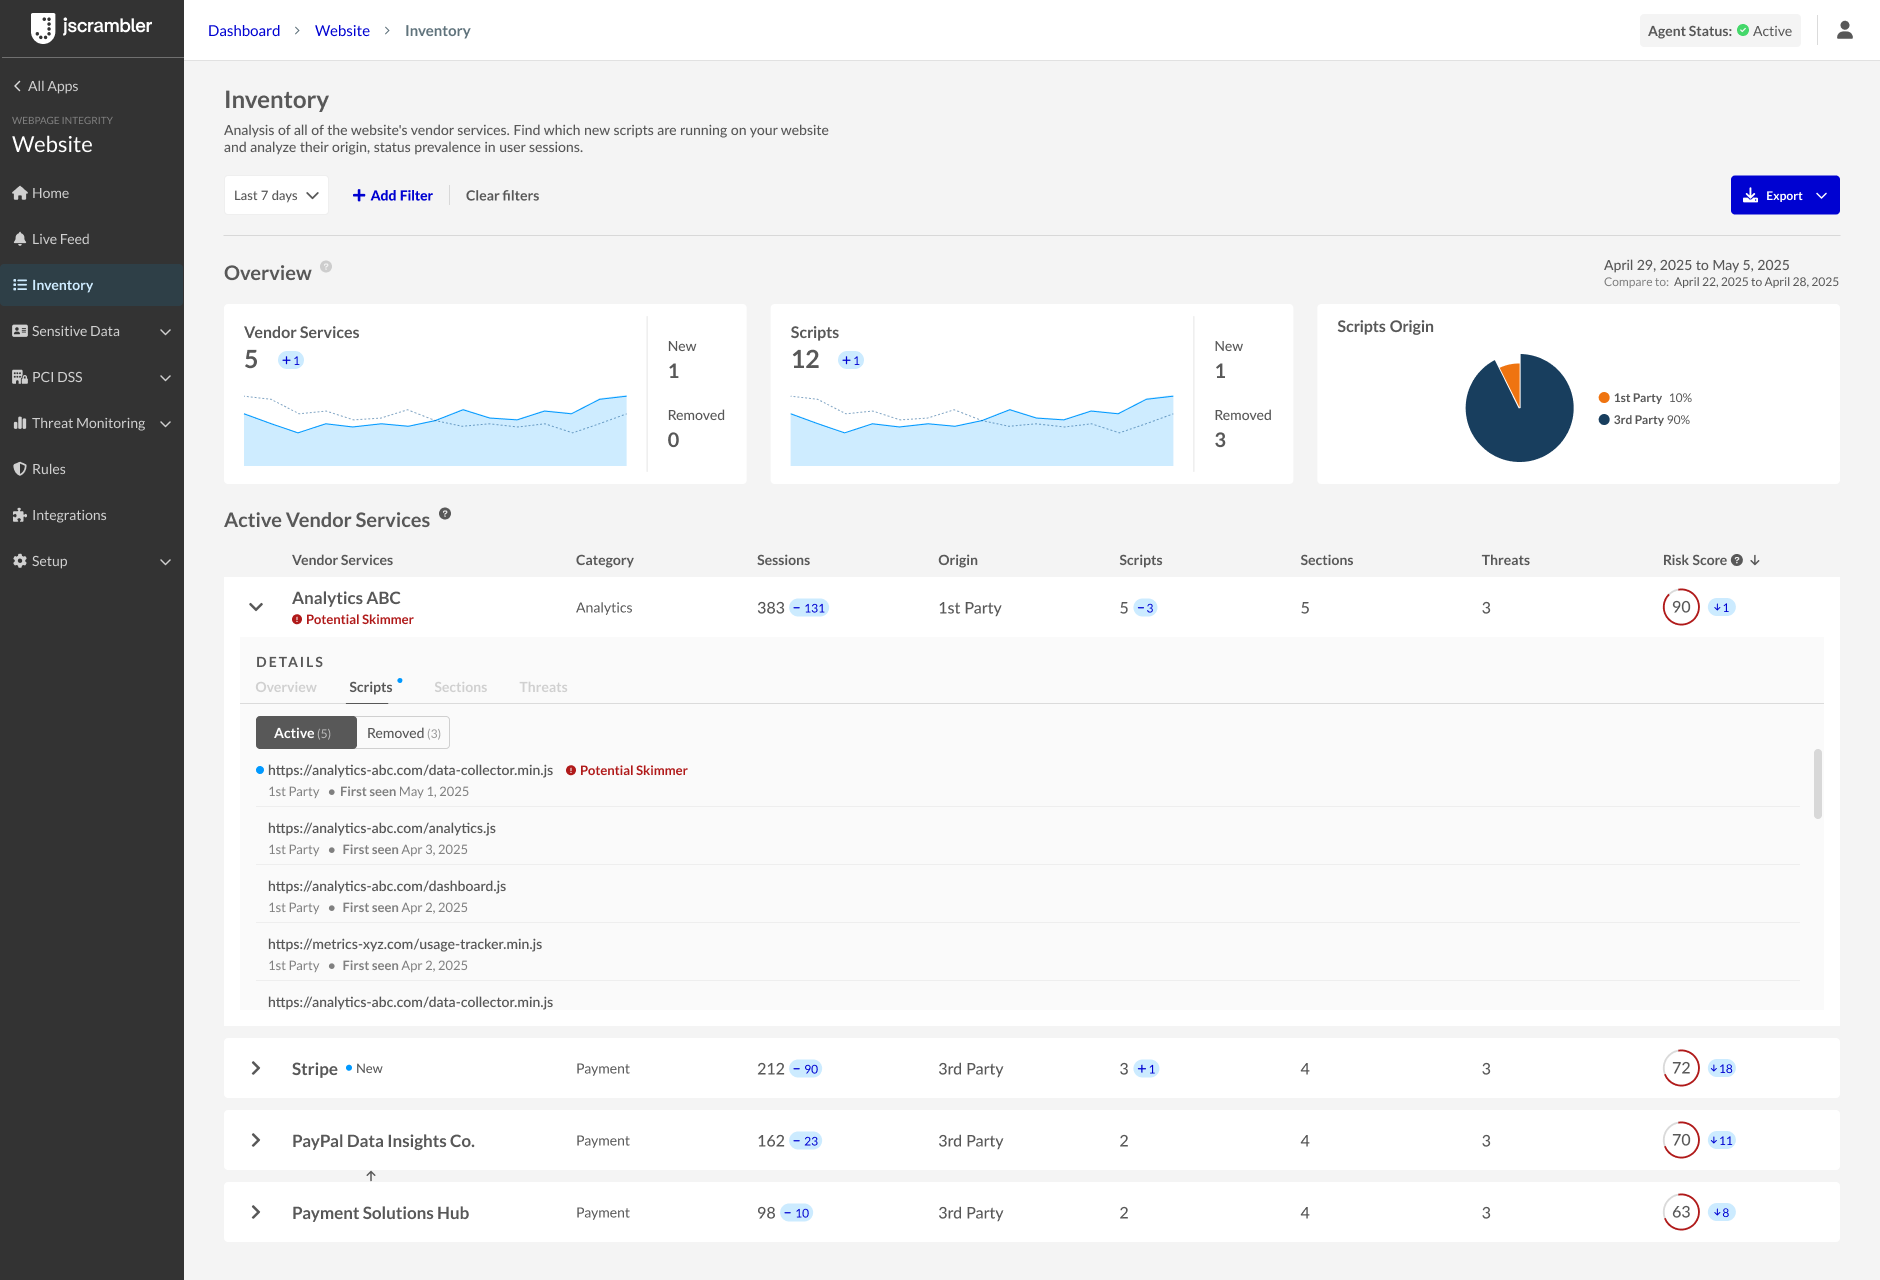
 

example-of-an-inventory-view-with-potential-skimmer-identifiedAn example of an Inventory view with a potential skimmer identified.


In addition, the Inventory feature provides visibility into threats related to sensitive data present or entered on the website. It enables verification of which scripts have access to specific data and ensures compliance with the appropriate data access permissions.


Skimming Detection

Now that you’ve spotted a skimmer in your Inventory view, what is behind it? You can go deeper to discover what happened and get more insight into the skimming risks. This is possible thanks to the Skimming Detection feature that is responsible for identifying and classifying scripts based on their potential security threats, including those associated with Magecart and skimming attacks. Skimming attacks are notorious for extracting sensitive information from websites, posing significant risks to both website owners and their users.


At its core, Skimming Detection is all about analyzing the scripts running on your website and flagging those that could be dangerous. Every script is scanned and categorized based on its behavior and the aspects detected in its code. If it looks clean, it’s marked as safe. But if it shows signs of malicious intent—especially those linked to Magecart-style skimming—it’s flagged as a threat.


This classification helps you stay ahead of attacks by giving you visibility into which scripts (and which vendors) could be putting your customers at risk.


Giving You Control: Manual Reclassification

Sometimes, a script might get flagged even when you know it’s safe. That’s why we have built-in flexibility. If your technical team reviews a script and determines it’s not a threat, you can manually mark it as safe right from your dashboard. That change is reflected within minutes, ensuring your data stays current and actionable.


Vendors and Risk Scores

The Skimming Detection system doesn’t stop at individual scripts—it also looks at vendors. If a vendor has even one script flagged as Skimmer, the vendor itself gets tagged accordingly, and its risk score spikes to reflect that elevated threat level. Clean up the scripts, and the vendor’s risk profile improves. It’s that simple.


This system makes it easier to prioritize threats, monitor your third-party ecosystem, and protect your site from one of the web’s most dangerous types of attacks.


Skimming Detection for PCI DSS Compliance

The Skimming Detection section of the dashboard alerts merchants when skimming activity is detected in their vendor services. If no skimming is found, you’ll see a reassuring message. If any skimming is detected, you’ll be able to access a link that shows you which specific vendors are compromised.

By analyzing the behavior of web scripts and the context in which they execute, the system detects various indicators commonly associated with skimming activity, such as:


  • Obfuscation
  • Stealth techniques
  • Data encryption
  • Injection of forms, iframes, and other elements
  • Access to sensitive data
  • Suspicious networking behavior

By evaluating these and other factors within the script and page context, the result provides a comprehensive assessment of whether potential skimming activity is present on the website.


If our system detects a potential skimmer—a malicious script designed to steal sensitive data, especially payment information—you’ll see it in the dashboard right away. You’ll see which vendors are involved and where exactly the threat was found, whether on a specific website or payment page. This visibility empowers your team to act quickly and precisely, minimizing risk and exposure.
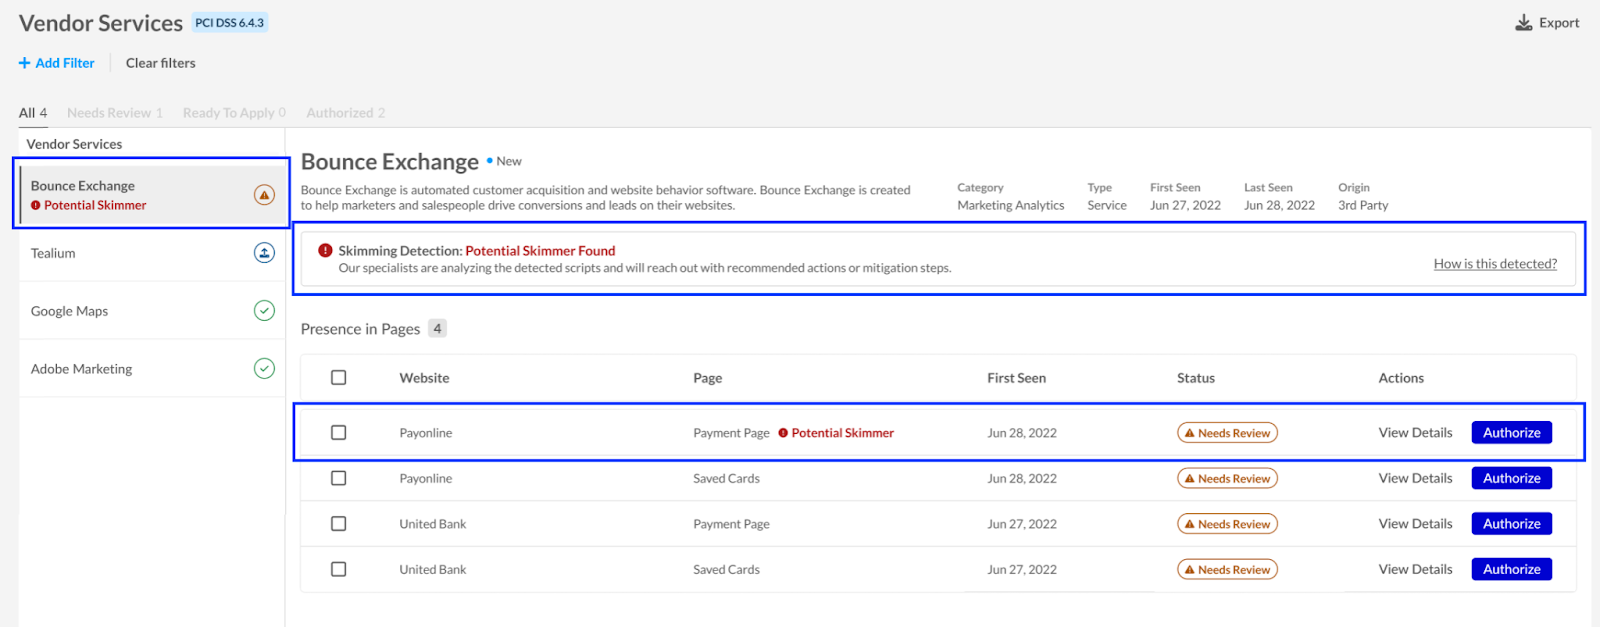
 

PCI-DSS-module-view

PCI DSS Module view with a “Potential skimmer found” notice.

No skimmers? No problem. When our system gives the all-clear, you’ll see a reassuring “No skimmer found” message. It’s peace of mind that your site is clean and your customers’ data is safe, for now.
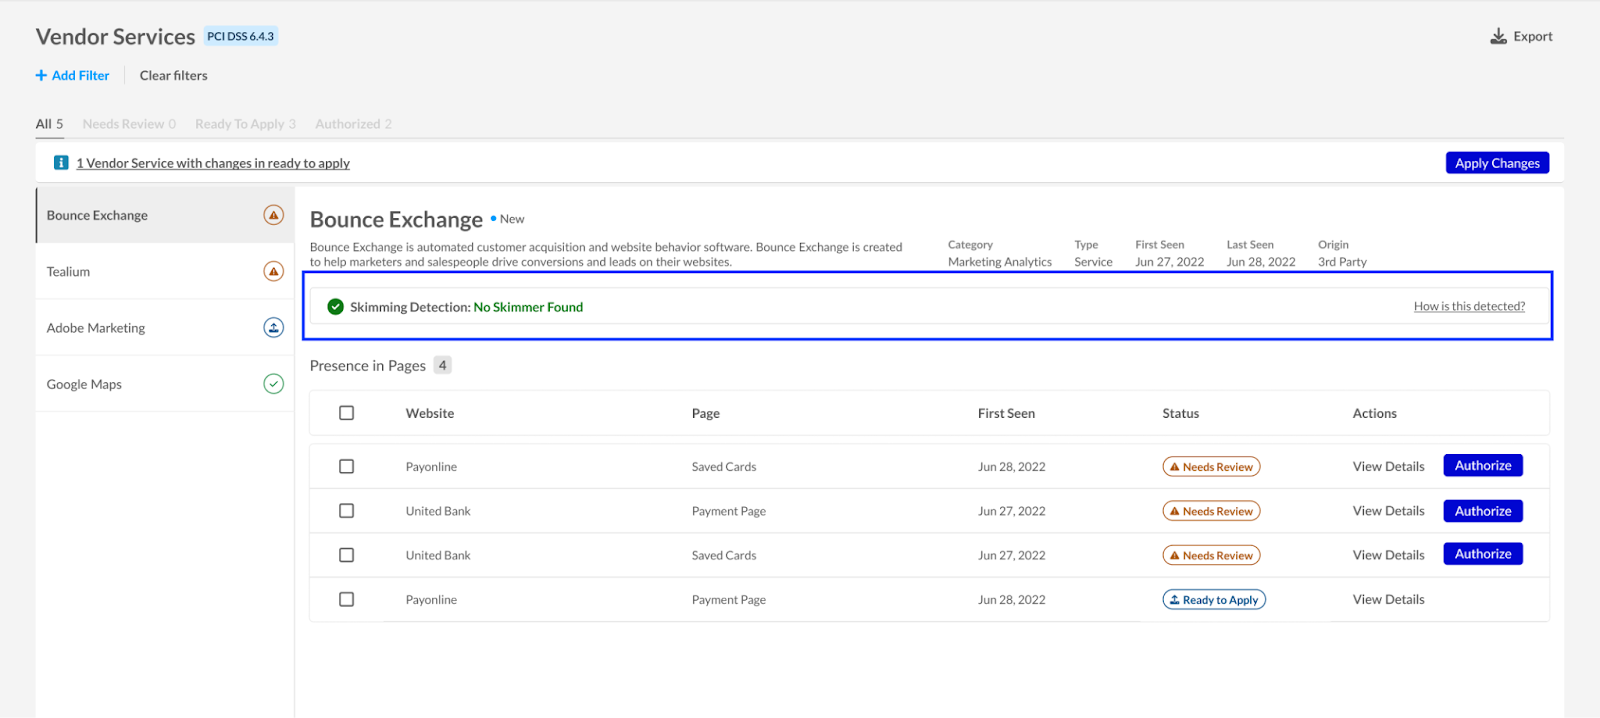
 

PCI-DSS-module-ni-skimmer-foundPCI DSS Module with a “No skimmer found” notice.

Next Steps After Skimming Detection

Jscrambler Webpage Integrity allows you to react to skimming alerts, review the malicious script or scripts in question, limit their access to data, and block them from performing malicious actions or data transfers.


In summary, the WPI product can block all unauthorized behaviors from third-party vendor scripts without preventing the script from loading on the page or performing authorized behaviors. This prevents actions such as skimming of payment, login, or other PII (Personally Identifiable Information) data, even if a vendor script contains both malicious code and useful code that is critical to the end-user experience.


As long as the script remains on the page, even if WPI is preventing all behaviors, it will still be included in the vendor inventory. The website administrator should remove a certain third-party vendor script to prevent its continued presence.


To learn more about the blocking capabilities of the Jscrambler WPI, check out the Form Fencing feature that specifically restricts third-party scripts from accessing form data. And stay tuned for the next WPI 101 series article that will cover PCI DSS compliance and how it helps meet the requirements 6.4.3 and 11.6.1, and goes beyond them with the blocking capability.
 

Jscrambler WPI 101 – Form Fencing

Welcome to our new blog series! Jscrambler WPI 101 is a series of articles about Jscrambler’s product Webpage Integrity (WPI), its main use cases, innovative features, and tips on how to maximize the benefits of using the product.
The focus of this article is the WPI use case for Form Fencing. Forms are integral to many online businesses that sell goods and services online. Forms gather important customer data and allow you to easily collect payment. Before we cover how WPI’s Form Fencing works, let’s see what kind of forms Webpage Integrity protects and the ways in which they are deployed on websites. In the section below, we’ll primarily review the payment forms as they collect the most sensitive data that criminals target – cardholder data.

Form Fencing: The Dangers of Form Data Leakage

Safeguarding user data is critical. Websites rely on third-party analytics libraries to track user behavior, but these integrations can sometimes become a security liability. Let’s imagine that there is a website that uses a third-party analytics library to store user session data. While this functionality is essential for business insights, it also opens the door for potential exploitation.

Imagine a scenario where the third-party library is compromised by malware. Let’s suppose the attackers manipulate a function to access all form inputs and exfiltrate sensitive information. Initially, the function only stores basic user details like email, user ID, first name, and last name.

However, with the malware in place, additional sensitive data—such as addresses and credit card details—could be stealthily collected and sent to an unauthorized external server, all without detection. This kind of data breach can be catastrophic, leading to identity theft, financial loss, and reputational damage.

Preventing Unauthorized Data Collection with Fencing Rules

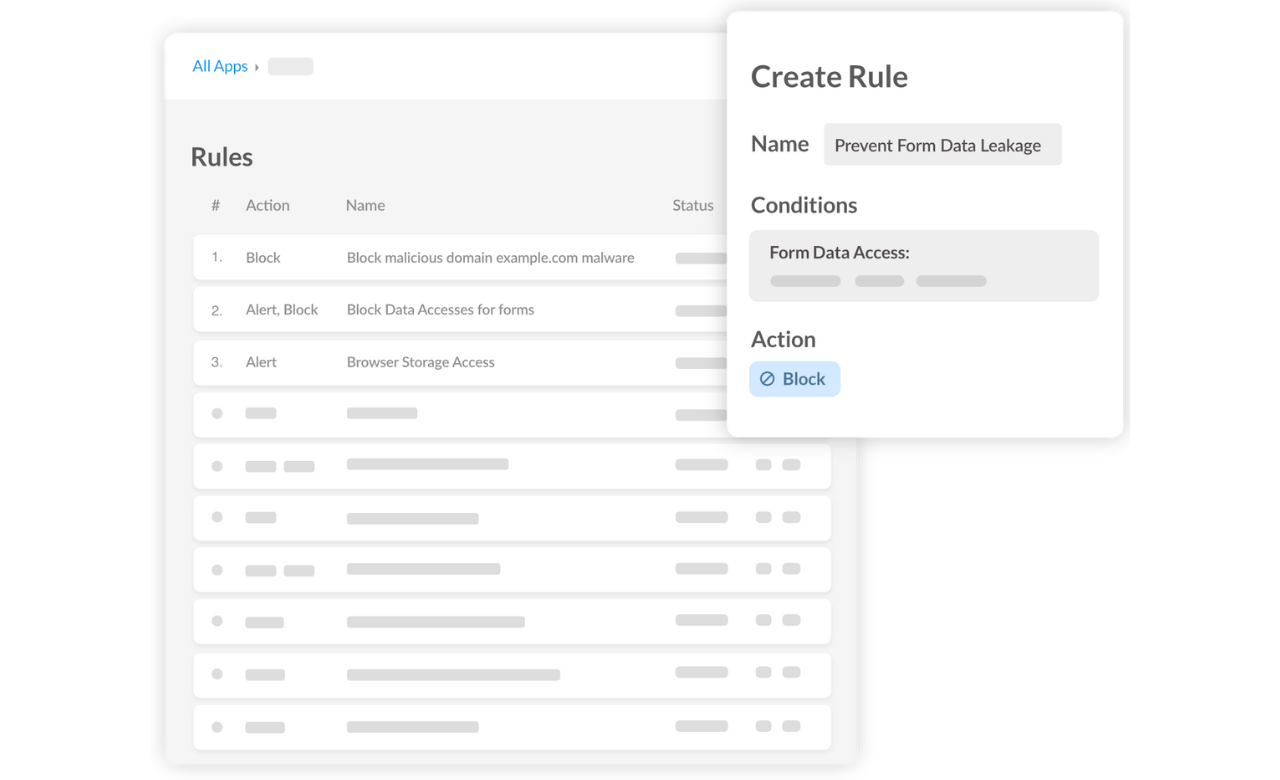
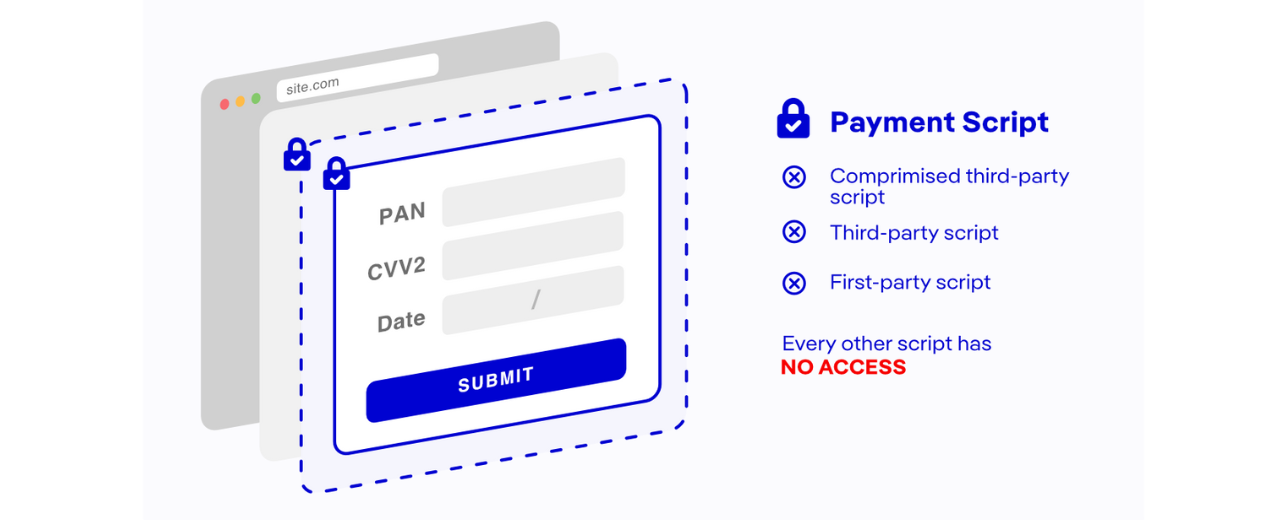
To counteract such threats, businesses can leverage WPI’s Form Fencing, a proactive security measure that ensures that only authorized first-party scripts and third-party vendors collect and transmit data. With Form Fencing, organizations can create specific rules to monitor and prevent third-party scripts from accessing form fields.

Preventing-Unauthorized-Data-Collection-with-Fencing-Rules

Setting up a Fencing rule is straightforward:

  • Navigate to the Rules page and create a new rule.
  • Define a clear name and description for easy identification.
  • Specify which website pages should be monitored.
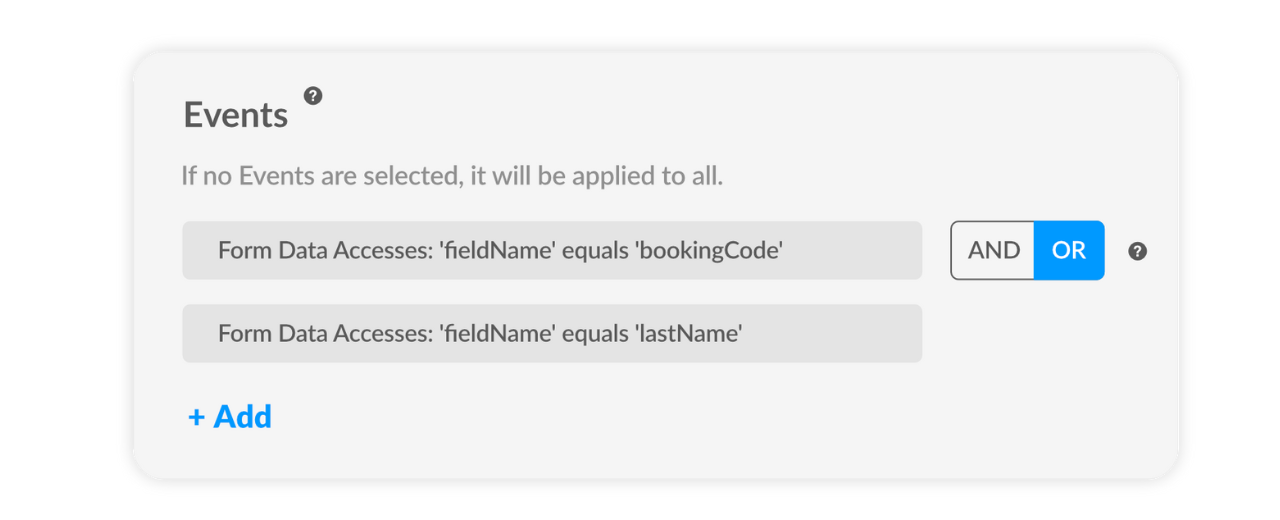
  • Identify the values to configure the rule with the form ID/name or the input ID/name (for example, bookingCode for input booking code and lastName for the input last name).
  • Configure the targets.

    Setting-up-Fencing-rule-is-straightforward

  • Configure the action to prevent form data from being accessed by unauthorized scripts.
  • Deploy the rule and activate the WPI protection agent.

Once in place, this rule ensures that any attempt to extract unauthorized information is immediately blocked and flagged in the dashboard.

Payment Form Deployment Types WPI Addresses

There are different ways in which you can deploy a form to be displayed on a website and collect payment data. The most vulnerable forms are usually forms that collect card payment data; they are the most common target of digital skimming attacks. Below are the most common types of payment forms.

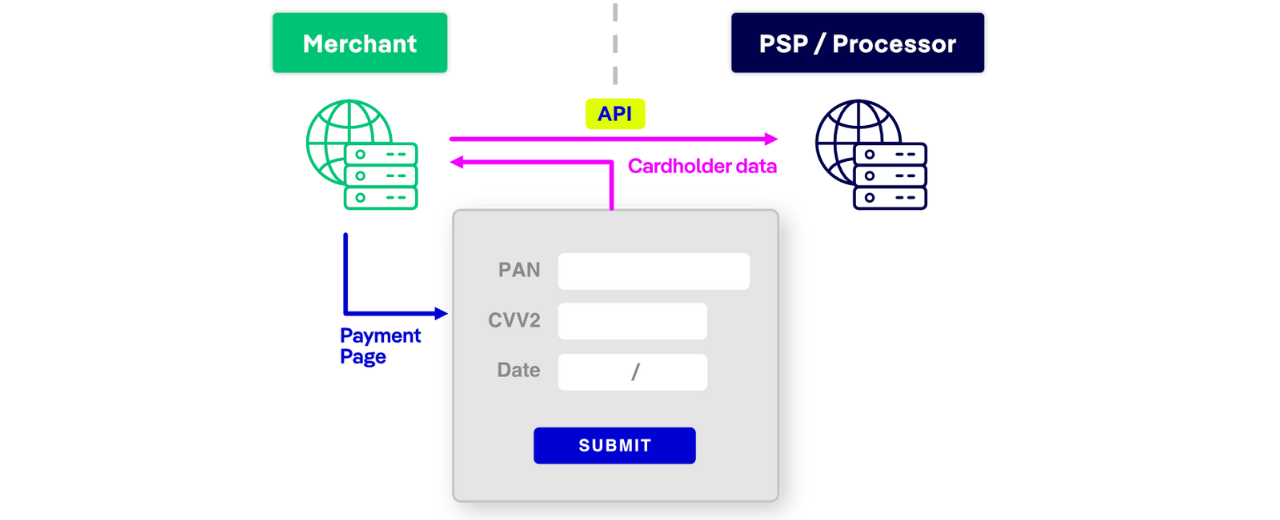
Direct API Integration Forms

Deployment: The merchant collects payment details and sends them securely via an API to the payment processor. In this case, the WPI agent should be injected by the merchant who is responsible for rendering the payment form.

Direct-API-Integration-Forms

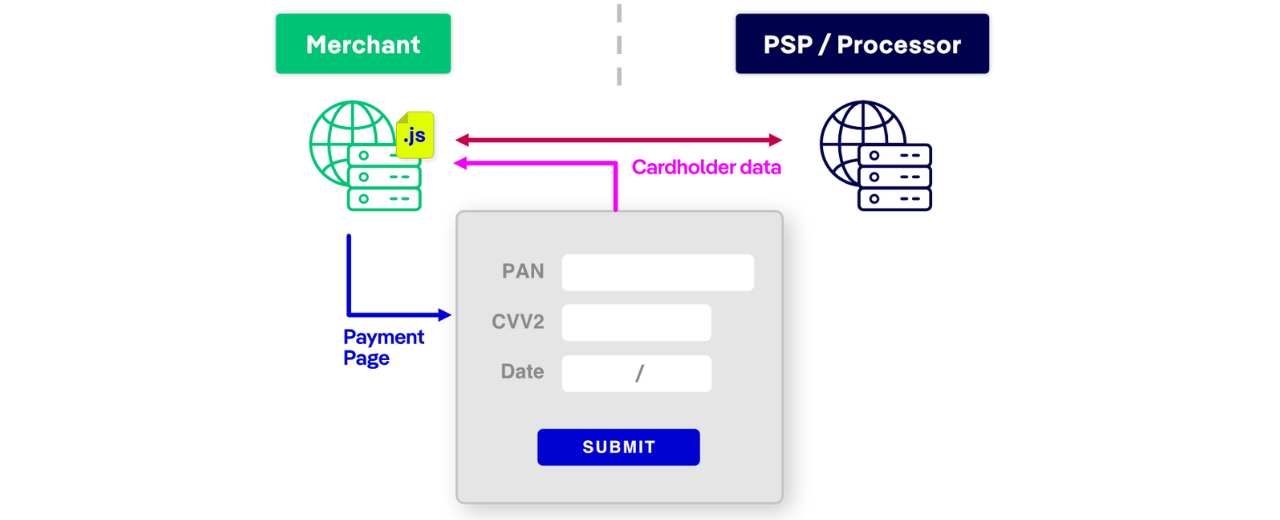
JavaScript-Based Payment Forms

Deployment: A secure JavaScript library (e.g., Stripe.js) collects payment data directly and sends it to the processor. In this case, the WPI agent should be injected by the merchant who is responsible for rendering the payment form.

 JavaScript-Based-Payment-Forms

Stripe.js-Braintree-Hosted-Fields

Example: Stripe.js, Braintree Hosted Fields


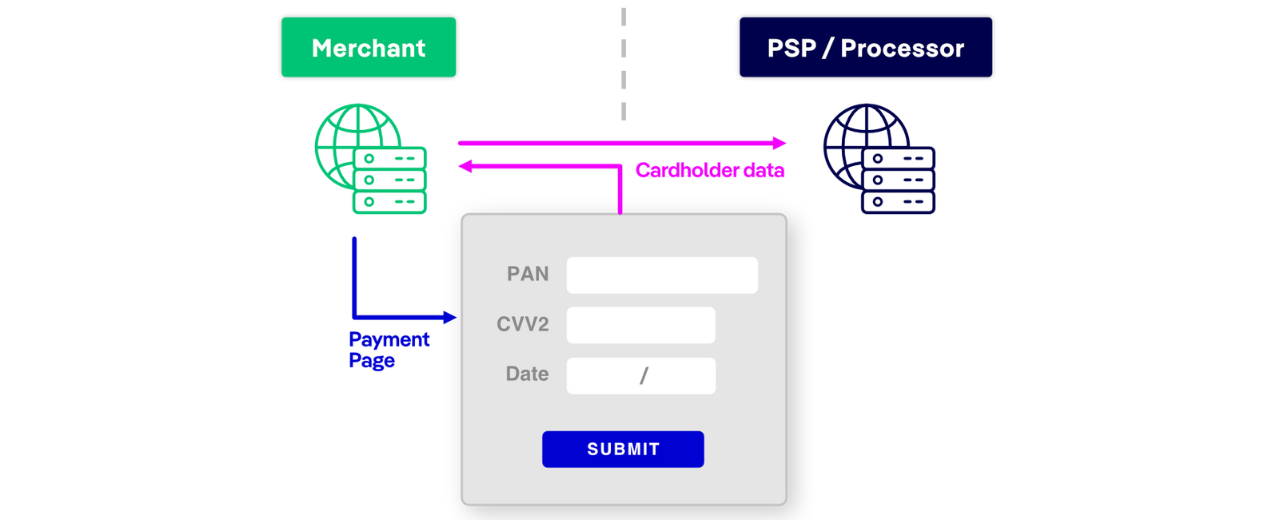
Hosted Payment Forms

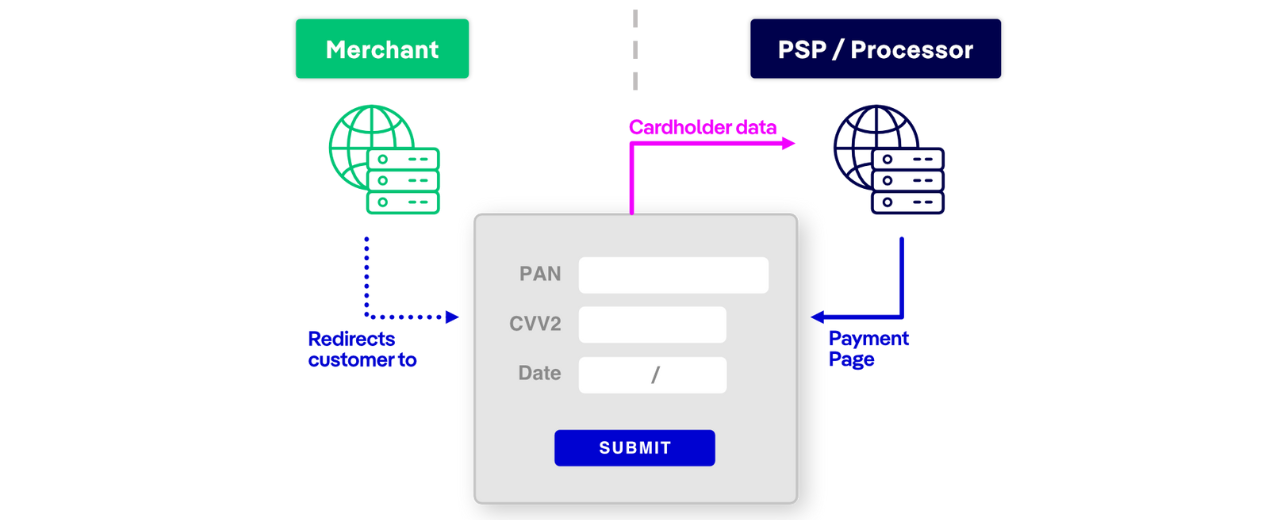
Deployment: A third-party payment processor hosts the form, so WPI should be deployed and provided by the Payment Service Provider (PSP).

Hosted-Payment-Forms

Form Fencing for PCI DSS v4 compliance

PCI DSS requirements 6.4.3 and 11.6.1 will become effective on March 31st, 2025. Both requirements were developed to ensure that online merchants’ payment pages are sufficiently protected to detect and prevent skimming attacks.

If you are a Merchant who hosts a payment form yourself, then you can use a Form Fencing feature as a Compensating Control or follow a Customized Approach to become PCI DSS v4 compliant. Therefore, you don’t need to worry about authorizing scripts.

Form-Fencing-PCI-DSS-v4-compliance 

Additionally, Form Fencing works as an extra layer of defense that can shield your forms from skimmers even before you authorize scripts.

As cyber threats continue to evolve, proactive security solutions like Form Fencing are essential in protecting sensitive information. By implementing Form Fencing, businesses can safeguard user data, maintain compliance with data protection regulations, and enhance trust with their customers. Don’t wait for a breach to occur—instead, take control of your data security today.