News Type: Press

Jscrambler Empowers Payment Service Providers in Enabling Merchants to Achieve PCI DSS V4 Compliance, According to Online Business Systems Report

PORTO, Portugal, July 15, 2025 – Jscrambler, the pioneering platform for client-side protection, today announced new independent research from Online Business Systems (OBS) titled “Jscrambler’s Iframe Integrity And The New PCI DSS Requirements.” A leading provider of innovative digital solutions and cybersecurity, the OBS report details Iframe Integrity’s success in helping payment service providers/payment gateways (PSPs) offer PCI DSS compliance (for requirements 6.4.3 and 11.6.1) and simplifying SAQ A eligibility for merchants by shielding payment pages from sophisticated e-skimming attacks while ensuring transaction security.

The number of payment card numbers stolen through e-commerce “skimming” attacks is surging. In these incidents, the e-commerce skimmer watches the transaction between the merchant and the consumer, stealing a copy of the customer’s payment card data, as it’s being entered. With an increasing number of attackers targeting scripts running in a consumer’s browser, the PCI Security Standards Council (PCI SSC) has introduced two new requirements in PCI DSS v4.0.1 specifically designed to reduce the risk of client-side e-skimming attacks — requirements 6.4.3 and 11.6.1.

PCI SSC also updated the Self-Assessment Questionnaire (SAQ A), designed for merchants who accept payments but who fully outsource payment processing, for example, by embedding a PSP’s payment pages in the merchant’s website. In this scenario, all payment processing is managed by the external, PCI DSS-compliant PSP. However, to be eligible to use the updated SAQ A, merchants now must confirm that their e-commerce site is not susceptible to script attacks.

In its new independent research assessment, OBS’s PCI SSC accredited Qualified Security Assessors (QSAs) and Offensive Security Services (OSS) experts evaluated Iframe Integrity’s effectiveness in meeting the latest anti-skimming requirements, particularly its ability to harden payment pages against a range of threats, including iframe hijacking, iframe overlays, fake iframes, and function hijacking. “Iframe Integrity safeguards payment pages against script attacks by isolating the PSP script and all elements related to the payment form from unauthorized interference by other scripts running on the parent page. Additionally, it mitigates risks where a malicious script on the merchant’s parent page could manipulate users into unintentionally exposing their payment data.”

Following a series of simulated attacks, where code snippets were executed in the browser’s console to simulate an attack executed by a malicious script running on the page, the OBS team reported that “Based on the observations of OBS’s QSAs and OSS experts, Iframe Integrity was successful in preventing all the tested attacks. Deploying the solution to a merchant’s parent page, as part of a PSP’s payment page script, appears to be a successful way of ensuring that the merchant’s payment page is not susceptible to script attacks.”

The paper goes on to report that “For e-commerce merchants who completely outsource payment processing to a PCI DSS compliant PSP that is using Jscrambler’s Iframe Integrity to harden their payment iframes, there is little additional work required to confirm the merchant meets the eligibility requirements in SAQ A.”

“Recent updates to PCI DSS—and specifically to SAQ A—have significantly expanded merchant responsibility for ensuring their e-commerce sites are not susceptible to client-side attacks. That shift has placed a heavy burden on many merchants lacking the technical and financial resources to validate and secure their environments,” said Pedro Fortuna, CTO at Jscrambler. “Iframe Integrity was designed to fill that gap by giving PSPs a solution that eases the compliance burden on merchants while securing payment pages against client-side threats. OBS’s new report offers strong third-party validation that we are delivering on that promise.”

“Many merchants today lack the technical and financial resources and are looking to their PSPs to ensure that their iframes and payment pages are secure,” said Jordan Wiseman, Fellow Consultant at OBS and author of the report. “Our review found that Jscrambler’s Iframe Integrity can secure payment pages against script-based attacks and can help PSPs support their merchant-customers’ compliance efforts.”

Learn more about Jscrambler’s Iframe Integrity. You can also read the complete “Jscrambler’s Iframe Integrity And The New PCI DSS Requirements” report.

About Online Business Systems

Online Business Systems is a leading provider of innovative digital solutions, cybersecurity services, and digital transformation, offering expertise in customer experience (CX), artificial intelligence, and strategic advising. Its team of cybersecurity experts develops robust security programs tailored to each client’s risk appetite, enabling organizations to focus on business growth. As members of GEAR, Online Business Systems’ team of over 40 Qualified Security Assessors (QSAs) delivers PCI guidance and assessment services to clients worldwide. The company’s Financial Services practice specializes in digital banking solutions, Fintech integration, and managed services, along with Digital Advisory offerings such as strategy, mergers and acquisitions, system selection, and brand experience.

About Jscrambler

Jscrambler is the leader in Client-Side Protection and Compliance. Jscrambler is the first to merge advanced polymorphic JavaScript obfuscation with fine-grained third-party tag protection in a unified Client-Side Protection and Compliance Platform. Jscrambler’s integrated solution ensures a robust defense against current and emerging client-side cyber threats, data leaks, misconfigurations, and IP theft, empowering software development and digital teams to innovate securely online with JavaScript.

Jscrambler’s Code Integrity product safeguards first-party JavaScript through state-of-the-art obfuscation and exclusive runtime protection. Jscrambler’s Webpage Integrity product mitigates threats and risks posed by third-party tags, all while ensuring compliance with the new version 4 of PCI DSS. Jscrambler’s Iframe Integrity empowers PSPs to deliver seamless protection, PCI DSS compliance, and SAQ A eligibility to merchants.

With Jscrambler, businesses adopt a unified, future-proof client-side security policy, all while achieving compliance with emerging security standards. Jscrambler serves a diverse range of customers, including top Fortune 500 companies, online retailers, airlines, media outlets, and financial services firms whose success depends on safely engaging with their customers online.

Jscrambler Re-Elected to the PCI SSC 2025-2027 Board of Advisors

Porto, Portugal

Jscrambler, a pioneer in client-side protection and compliance, today announced it has been re-elected to the PCI Security Standards Council (SSC) Board of Advisors for 2025-2027. The PCI SSC Board of Advisors is a group of industry experts who provide technical insights to help shape payment security standards. Jscrambler Chief Technology Officer and Co-Founder, Pedro Fortuna, and Security Advisor, John Elliott, have been Board of Advisors members since 2023.


Since its launch in 2004, the PCI SSC Board of Advisors has represented PCI SSC participating organizations worldwide, ensuring global industry involvement in the development of PCI security standards and programs. With today’s announcement, Jscrambler will continue to serve on the board, bringing its industry and technical insights to PCI SSC plans and projects while actively contributing to the creation of new standards and major revisions aimed at securing payment data. 


“The Board of Advisors provides industry expertise and perspectives that influence and shape the development of PCI security standards and programs. We look forward to continuing to work with Jscrambler in our efforts to help organizations secure payment data globally,” said PCI SSC Executive Director Gina Gobeyn.


“Cyber threats targeting payment environments are escalating, with e-skimming attacks becoming more common and damaging. Over the last year, we’ve worked closely with PCI SSC to help businesses strengthen their defenses against these threats,” said Rui Ribeiro, CEO and Co-founder of Jscrambler. “We’re proud that Pedro and John will continue serving on the Board of Advisors, not only sharing their expert insights but helping organizations around the globe protect their customers’ payment data.”


In addition to its work with the Council, Jscrambler continues to expand its comprehensive client-side protection and compliance platform, as well as PCI DSS solutions, designed to simplify ongoing script management, protection, and compliance. In December, Jscrambler announced that it had been assessed as compliant with PCI DSS v4 following an external assessment by Integrity360, a leading Qualified Security Assessor (QSA). This achievement reinforces Jscrambler’s ability to protect its customers’ sensitive data and ensure the security of their financial transactions. 


In addition to today’s news, Jscrambler will also be participating in upcoming PCI Community events in North America, Europe, and the Asia Pacific. For additional details on these events, visit our events page. For more information about Jscrambler and its solutions, visit https://jscrambler.com/.


About the PCI Security Standards Council

The PCI Security Standards Council (PCI SSC) leads a global, cross-industry effort to increase payment security by providing industry-driven, flexible and effective data security standards and programs that help businesses detect, mitigate and prevent cyberattacks and breaches. Connect with PCI SSC on LinkedIn. Join the conversation on X (formerly Twitter) @PCISSC. Subscribe to the PCI Perspectives Blog. Listen to the Coffee with the Council podcast.


About Jscrambler

Jscrambler is the leader in Client-Side Protection and Compliance. Jscrambler is the first to merge advanced polymorphic JavaScript obfuscation with fine-grained third-party tag protection in a unified Client-Side Protection and Compliance Platform.

Jscrambler’s integrated solution ensures a robust defense against current and emerging client-side cyber threats, data leaks, misconfigurations, and IP theft, empowering software development and digital teams to innovate securely online with JavaScript. Jscrambler’s Code Integrity product safeguards first-party JavaScript through state-of-the-art obfuscation and exclusive runtime protection. Jscrambler’s Webpage Integrity product mitigates threats and risks posed by third-party tags, all while ensuring compliance with the new version 4 of PCI DSS.

Jscrambler’s Iframe Integrity empowers PSPs to deliver seamless protection, PCI DSS compliance, and SAQ A eligibility to merchants. With Jscrambler, businesses adopt a unified, future-proof client-side security policy, all while achieving compliance with emerging security standards. Jscrambler serves a diverse range of customers, including top Fortune 500 companies, online retailers, airlines, media outlets, and financial services firms whose success depends on safely engaging with their customers online.


Jscrambler Wins Gold for Client-Side Security and PCI Compliance in 2025 Globee® Awards for Cybersecurity

PORTO, Portugal

Jscrambler, the pioneering platform for client-side protection, has been named a winner in the 21st Annual 2025 Globee® Awards for Cybersecurity, a globally recognized program celebrating excellence in all areas of cybersecurity. Jscrambler received gold in both the Client-Side Security and PCI (Payment Card Industry) Compliance categories, highlighting the company’s groundbreaking contributions to digital security.

While JavaScript frameworks and third-party JavaScript-based add-ons enable mainstream businesses to rapidly create powerful online experiences, they also introduce four distinct risks, including new skimming threats, risks of IP theft, risks of data leakage, and compliance challenges. As an innovative client-side protection provider, Jscrambler offers the only comprehensive client-side protection platform that secures both first- and third-party JavaScript.

In addition, the combination of the company’s client-side protection with its PCI DSS Quick Start Program and QSA Alliance Program, Jscrambler allows organizations to achieve PCI Data Security Standard (DSS) v4 compliance within one business day without compromising the security of cardholder data.

“This recognition by the Globee Awards is a testament to the strength of Jscrambler’s solution, technical expertise, and the community that our PCI Quick Start Program and QSA Alliance have fostered,” said Rui Ribeiro, CEO and Co-founder of Jscrambler. “Jscrambler enables secure innovation, upholds robust security, and provides merchants, PSPs, and assessors with the resources, tools, and guidance to achieve compliance in a frictionless, scalable, verifiable, and more efficient way.”

San Madan, President of the Globee Awards, commended this year’s winners: “Congratulations to the 2025 winners for their exceptional contributions to strengthening our digital world. Your dedication, innovation, and leadership are not only driving cybersecurity forward but also inspiring the industry to reach new heights. We are proud to recognize and celebrate your success.”

The Globee® Awards for Cybersecurity spotlight the achievements of companies and individuals excelling in risk management, threat detection, cloud security, AI-driven defense, data privacy, zero-trust architecture, compliance, and other cutting-edge cybersecurity innovations that safeguard digital ecosystems worldwide. To be recognized as a Gold Globee® Winner, an entrant needs to attain an average score of 9.0 or above, or have the highest score in their category, according to the judgment of the evaluators.

The Gold Globee® Winner accolade marks the recipient’s superior performance, innovation, and leadership in their field, distinguishing them as leaders of excellence and encouraging the broader industry community to aim for and achieve high standards of excellence.

About Jscrambler

Jscrambler is the leader in Client-Side Protection and Compliance. Jscrambler is the first to merge advanced polymorphic JavaScript obfuscation with fine-grained third-party tag protection in a unified Client-Side Protection and Compliance Platform. Jscrambler’s integrated solution ensures a robust defense against current and emerging client-side cyber threats, data leaks, misconfigurations, and IP theft, empowering software development and digital teams to innovate securely online with JavaScript.

Jscrambler’s Code Integrity product safeguards first-party JavaScript through state-of-the-art obfuscation and exclusive runtime protection. Jscrambler’s Webpage Integrity product mitigates threats and risks posed by third-party tags, all while ensuring compliance with the new version 4 of PCI DSS. With Jscrambler, businesses adopt a unified, future-proof client-side security policy, all while achieving compliance with emerging security standards.

Jscrambler serves a diverse range of customers, including top Fortune 500 companies, online retailers, airlines, media outlets, and financial services firms whose success depends on safely engaging with their customers online.

About the Globee® Awards

The Globee® Awards present recognition in ten programs and competitions, including the Globee® Awards for Achievement (American Business), Globee® Awards for Artificial Intelligence, Globee® Awards for Business (International), Globee® Awards for Customer Excellence, Globee® Awards for Cybersecurity, Globee® Awards for Disruptors, Globee® Awards for Impact (Women in Business). Globee® Awards for Innovation (also known as Golden Bridge Awards®), Globee® Awards for Leadership, and the Globee® Awards for Technology. Visit the official.

Jscrambler Unveils Iframe Integrity to Help PSPs Protect Merchants from Costly Payment Card Skimming Attacks

PORTO, Portugal

Jscrambler, a pioneer in client-side protection, today announced the launch of Iframe Integrity, a new innovative solution that helps payment service providers (PSPs) deliver instant PCI DSS v4-compliant payment iframes to merchants. With Iframe Integrity, PSPs protect merchants from costly script-based attacks while ensuring eligibility with the new Self-Assessment Questionnaire A (SAQ A) and FAQ 1588 updates.

PSPs offer easy-to-integrate, cost-effective payment solutions that allow merchants to securely process transactions without the need for merchants to invest in complex infrastructure. Often operating with limited technical and financial resources, many merchants rely on PSPs to handle everything from payment gateway integration to fraud prevention, as well as compliance with PCI DSS v4 and payment page requirements 6.4.3 and 11.6.1.

Powered by Jscrambler’s market-leading technology, including Code Integrity and Webpage Integrity, this new offering allows PSPs to deliver PCI DSS v4-compliant payment iframes to merchants and meet the new eligibility criterion included in the recent SAQ A and FAQ 1588 updates. These updates require merchants to confirm that their third-party service provider/payment processor’s solution includes techniques that protect the merchant’s payment page from script-based attacks such as digital skimming.

Despite the rise in script-based attacks, many businesses remain exposed. According to the 2024 Jscrambler research, only 36% of businesses have policies and tools in place to prevent digital skimming. By working with PSPs that are using Iframe Integrity and are aligned with SAQ A, merchants can demonstrate their commitment to securing their customers’ data.

“Online merchants rely on PSPs to deliver the latest payment capabilities that secure transactions while helping to enhance the overall customer experience,” said Rui Ribeiro, CEO and Co-founder of Jscrambler. “With Iframe Integrity, we eliminate complex configurations, maintenance, and operational burdens, making it fast and easy for payment processors and PSPs to deliver PCI DSS compliance and security at scale. As a result, they can reduce risk, open new revenue streams, and maintain a seamless, optimized experience that their merchants can trust by providing instant, robust protection for every transaction without disruption.”

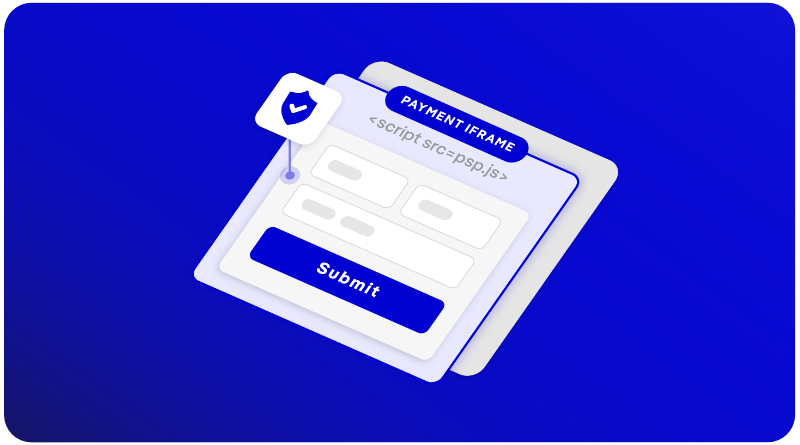
Interested PSPs simply integrate Iframe Integrity into their existing script build process, instantaneously creating a controlled and secure iframe environment for loading payment pages and ensuring transactions remain protected from threats. Hardened with Jscrambler’s integrity technology, the iframe is continuously monitored and safeguarded against overlay, hijacking, and formjacking attacks targeting payment pages. Unlike traditional security solutions, Iframe Integrity is fully automated and completely transparent, requiring minimum maintenance from PSPs and zero management from merchants.

Main Iframe Integrity features include:

  • PSP Script Hardening: Protects against reverse engineering and automated threats with PSP script tamper-resistance.
  • Function Hijacking Protection: Applies monkey-patching protection in privileged functions (on the parent page).
  • Iframe Hijacking Protection: Prevents iframe hijacking attacks by isolating Document Object Model (DOM) methods used to tamper with iframe creation processes (on the parent page).
  • Iframe Overlay Protection: Prevents iframe hijacking attacks by isolating DOM methods used to create new iframes or tampering with existing (on the parent page).
  • Form Overlay Protection: Prevents iframe hijacking attacks by isolating DOM methods used to create new forms or tampering with existing (on the parent page).
  • Iframe & Form Control: Provides fine-grained control over how iframes and forms can be used by scripts (on the parent page).

Jscrambler Iframe Integrity is available now. Learn more about how Jscrambler can help PSPs ensure merchant compliance with PCI DSS v4 and ultimately protect their businesses from growing script-based attacks. In addition, read the latest blog from Chief Technology Officer Pedro Fortuna, Introducing Iframe Integrity: Redefining Payment Page Security for PSPs.


About Jscrambler

Jscrambler is the leader in Client-Side Protection and Compliance. Jscrambler is the first to merge advanced polymorphic JavaScript obfuscation with fine-grained third-party tag protection in a unified Client-Side Protection and Compliance Platform.

Jscrambler’s integrated solution ensures a robust defense against current and emerging client-side cyber threats, data leaks, misconfigurations, and IP theft, empowering software development and digital teams to innovate securely online with JavaScript.

Jscrambler’s Code Integrity product safeguards first-party JavaScript through state-of-the-art obfuscation and exclusive runtime protection. Jscrambler’s Webpage Integrity product mitigates threats and risks posed by third-party tags, all while ensuring compliance with the new version 4 of PCI DSS. Jscrambler’s Iframe Integrity empowers PSPs to deliver seamless protection and PCI DSS compliance and SAQ A eligibility to merchants.

With Jscrambler, businesses adopt a unified, future-proof client-side security policy, all while achieving compliance with emerging security standards.  Jscrambler serves a diverse range of customers, including top Fortune 500 companies, online retailers, airlines, healthcare, media outlets, and financial services firms whose success depends on safely engaging with their customers online.

Jscrambler Client-Side Protection and Compliance Capabilities Recognized in 2025 Cybersecurity Excellence Awards

PORTO, Portugal


Jscrambler, the pioneering platform for client-side protection, today announced that it has won in the categories of Best Cybersecurity Compliance Company, Best Client-Side Security Product, and Best Magecart Protection Product in the 2025 Cybersecurity Excellence Awards


The Cybersecurity Excellence Awards is an annual competition honoring individuals and companies that demonstrate excellence, innovation and leadership in information security. Nominated companies are evaluated based on the strength of their submission, which includes an overview of the company or product, a list of key capabilities and features, and a description of how the nominee differs from other providers or solutions available in the space. A popular vote and comments received from the cybersecurity community are considered in the event of a tie. Awards are then segmented by company size and region to ensure fairness and recognition of diverse achievements.  


“While client-side threats continue to grow, client-side environments often receive insufficient attention and many companies still lack the necessary tools to protect user data and ensure compliance. We’re delighted that this honor emphasizes the criticality of client-side security and Jscrambler’s impact on the cybersecurity industry,” said Jscrambler CEO, Rui Ribeiro. 


Jscrambler is the only comprehensive client-side protection platform that covers both first- and third-party JavaScript. The Jscrambler Client-Side Protection Platform provides a holistic security and compliance policy, protecting against current and emerging client-side cyber threats, Magecart attacks, digital skimming, data leaks, misconfigurations, and IP theft, while enabling businesses to craft advanced online experiences. 


“We congratulate Jscrambler on these outstanding achievements,” said Holger Schulze, founder of Cybersecurity Insiders and organizer of the Cybersecurity Excellence Awards. “As we celebrate 10 years of recognizing excellence in cybersecurity, Jscrambler’s innovation, commitment, and leadership set a powerful example for the entire industry.”


Learn more about Jscrambler’s client-side protection and compliance platform.  


About Jscrambler

Jscrambler is the leader in Client-Side Protection and Compliance. Jscrambler is the first to merge advanced polymorphic JavaScript obfuscation with fine-grained third-party tag protection in a unified Client-Side Protection and Compliance Platform. Jscrambler’s integrated solution ensures a robust defense against current and emerging client-side cyber threats, data leaks, misconfigurations, and IP theft, empowering software development and digital teams to securely innovate online with JavaScript.

Jscrambler’s Code Integrity product safeguards first-party JavaScript through state-of-the-art obfuscation and exclusive runtime protection.

Jscrambler’s Webpage Integrity product mitigates threats and risks posed by third-party tags, all while ensuring compliance with the new anti-skimming requirements in version 4 of PCI DSS. With Jscrambler, businesses adopt a unified, future-proof client-side security policy, all while achieving compliance with emerging security standards.  Jscrambler serves a diverse range of customers, including top Fortune 500 companies, online retailers, airlines, media outlets, and financial services firms whose success depends on safely engaging with their customers online.


Jscrambler Secures $5.2M Investment from Iberis Capital to Strengthen its Position as a Leader in Client-Side Protection

PORTO, Portugal


Jscrambler, a pioneer in client-side protection, today announced the completion of a $5.2M investment round subscribed to exclusively by Iberis Capital. This latest investment builds upon a previous $15 million Series A funding round led by Ace Capital Partners with participation from Sonae IM and Portugal Ventures, which also led the company’s initial Seed round.


Despite the continued growth in client-side threats, many businesses continue to lack the tools needed to keep user data safe. According to the 2024 Jscrambler report, only 36% of respondents’ companies have policies and tools to prevent data skimming. Now, with this latest investment, Jscrambler will further accelerate its efforts to help companies securely and cost-effectively achieve PCI DSS v4 compliance ahead of the  March 31, 2025 deadline. PCI DSS v4 requirements 6.4.3 and 11.6.1 are designed to prevent digital skimming attacks on websites that capture payment card data. In addition to PCI compliance, this round of funding will also support Jscrambler’s commitment to ongoing research and solution innovation.


“Merchants accepting payments face escalating threats like digital skimming, yet many lack the client-side protection tools that are vital to securing customer cardholder data,” said Rui Ribeiro, CEO and co-founder of Jscrambler. “With the PCI compliance deadline rapidly approaching, the urgency for effective client-side protection solutions has never been greater. This funding round from Iberis Capital will enable us to address this immediate pressing need while accelerating our investments in innovation and research to ensure our clients are always prepared for the challenges of tomorrow.”


João Henriques, Partner at Iberis Capital, stated: “Jscrambler delivers a world-leading technological solution that empowers businesses to protect their websites, meeting the increasing demand for robust digital security. Supported by a leadership team with extensive industry knowledge, Jscrambler is uniquely positioned to lead in client-side security. Iberis is proud to be part of Jscrambler’s journey toward success.”


Jscrambler is transforming application security, becoming an essential solution for businesses seeking to protect their applications and web pages while ensuring user trust. By enabling organizations to monitor and safeguard their front-end JavaScript code in real-time, Jscrambler is designed to make client-side security easier to implement, scalable, and focused on threat prevention.


About Jscrambler

Jscrambler is the leader in Client-Side Protection and Compliance. Jscrambler is the first to merge advanced polymorphic JavaScript obfuscation with fine-grained third-party tag protection in a unified Client-Side Protection and Compliance Platform. Jscrambler’s integrated solution ensures a robust defense against current and emerging client-side cyber threats, data leaks, misconfigurations, and IP theft, empowering software development and digital teams to innovate securely online with JavaScript.

Jscrambler’s Code Integrity product safeguards first-party JavaScript through state-of-the-art obfuscation and exclusive runtime protection. Jscrambler’s Webpage Integrity product mitigates threats and risks posed by third-party tags, all while ensuring compliance with the new version 4 of PCI DSS. With Jscrambler, businesses adopt a unified, future-proof client-side security policy, all while achieving compliance with emerging security standards.  Jscrambler serves a diverse range of customers, including top Fortune 500 companies, online retailers, airlines, media outlets, and financial services firms whose success depends on safely engaging with their customers online.

About Iberis Capital 

Founded in 2017, Iberis Capital is a venture capital and private equity fund manager based in Lisbon. Iberis Capital invests in Venture Capital, Mid-Market growth and buyout, Yielding Investments, and Sustainable Investments with flexible investment structures adapted to the needs of companies. With close to 600 million euros in assets under management and a base of more than 1,200 investors, Iberis Capital establishes partnership relationships and has contributed to the development of some of Portugal’s most promising technology companies, being able to support them at different stages of their growth. Find out more about Iberis Capital.


Jscrambler Upgrades QSA Alliance Program to Accelerate PCI DSS Education Ahead of Impending Deadline

PORTO, Portugal


Jscrambler, the pioneering platform for client-side protection, today announced enhancements to its existing QSA Alliance program designed to strengthen PCI DSS expertise for Qualified Security Assessors (QSA) and Internal Security Assessors (ISA) ahead of the impending March 31, 2025 deadline. The expanded program will be led by PCI Technical Advisor, former PCI SSC employee, and QSA enablement leader Gareth Bowker.

As the author of many of the first PCI SSC QSA training programs, Bowker brings significant experience to Jscrambler, including over a decade at the PCI Security Standards Council, where he most recently served as the Director of Technology, Infrastructure, and Privacy. Through his experience, he has devised an effective formula for ensuring both new and experienced QSAs receive the training necessary to attain the knowledge, understanding, and assessment experience to effectively navigate PCI DSS’s new 6.4.3 and 11.6.1 requirements for their clients.


Under Bowker’s guidance, the expanded QSA Alliance program will feature advanced enablement strategies, including new live training sessions, self-service videos, newsletter content, and assessor hotline access. The program will also feature a monthly PCI DSS Assessor Forum, a series of virtual community events where QSAs and ISAs can learn and discuss new PCI DSS topics supporting their educational journey. The forum will be moderated by PCI DSS expert John Elliott, who will be joined by other PCI DSS experts who cover new topics, exchange ideas, and foster QSA collaboration.


“As the March 31 PCI DSS deadline approaches, it’s imperative for both QSAs and ISAs to fully understand the updated requirements so they can guide merchants toward compliance,” said Pedro Fortuna, Chief Technology Officer and co-founder of Jscrambler and member of the Board of Advisors for PCI SSC. “With the addition of Gareth to our team of PCI experts along with these new program enhancements, we’re providing the assessors with the proven tools, guidance, and resources they need to accelerate their understanding and help merchants address potential threats effectively and avoid costly penalties.”


All attendees who join and participate in the PCI DSS Assessor Forum live will be eligible for continuing professional education (CPE) credits and provided with a proof of attendance certificate that may be used to maintain their relevant security and assessor certifications. The 2025 PCI DSS Assessor Forum will kick off on January 28, 2025, with John Elliott and Gareth Bowker discussing challenges in implementing and assessing all the new requirements relating to system and application accounts.


Partner Perspectives on the Jscrambler QSA Alliance Program

“Online works with our clients through their digital journey while protecting them from the new threats that come with it, including those targeting account data,” said Jeff Man, PCI QSA and Information Security Evangelist at Online Business Systems. “As a member of Jscrambler’s QSA Alliance program, we have access to key content and services, including its QSA Payment Page Inventory tool that makes it easy to verify e-commerce scripts as part of a PCI DSS assessment. As a result, we can help facilitate the PCI DSS compliance process while mitigating costly web skimming attacks.”


“Our team is laser-focused on the fast-approaching PCI DSS March 31 deadline and helping our clients protect payment data as well as the sensitive information of their customers, said Adam Bush, Director PCI Services at Schellman. “Jscrambler is a key partner in these efforts. Through their QSA Alliance program, we gain access to valuable complementary resources that are helping us educate customers on the specific challenges they will face in the months ahead and provide a path they can follow to achieve compliance.”


About Jscrambler

Jscrambler is the leader in Client-Side Protection and Compliance. Jscrambler is the first to merge advanced polymorphic JavaScript obfuscation with fine-grained third-party tag protection in a unified Client-Side Protection and Compliance Platform. Jscrambler’s integrated solution ensures a robust defense against current and emerging client-side cyber threats, data leaks, misconfigurations, and IP theft, empowering software development and digital teams to securely innovate online with JavaScript.

Jscrambler’s Code Integrity product safeguards first-party JavaScript through state-of-the-art obfuscation and exclusive runtime protection.

Jscrambler’s Webpage Integrity product mitigates threats and risks posed by third-party tags, all while ensuring compliance with the new anti-skimming requirements in version 4 of PCI DSS. With Jscrambler, businesses adopt a unified, future-proof client-side security policy, all while achieving compliance with emerging security standards.  Jscrambler serves a diverse range of customers, including top Fortune 500 companies, online retailers, airlines, media outlets, and financial services firms whose success depends on safely engaging with their customers online.


Jscrambler Introduces Solution Enhancements that Pave the Way to 1-Day PCI DSS Compliance

PORTO, Portugal


Jscrambler, the pioneering client-side protection platform, announced enhancements to its PCI DSS Solution today. By adding advanced payment page script controls and ease of management to its existing market-leading capabilities, Jscrambler makes it fast and easy for merchants to securely and cost-effectively achieve PCI DSS compliance with requirements 6.4.3 and 11.6.1 before the March 31, 2025 deadline. 


1-Day PCI DSS Compliance


Jscrambler’s new and existing PCI DSS capabilities remove obstacles to complying with PCI DSS requirements 6.4.3 and 11.6.1. These requirements are designed to protect against and detect web skimming attacks on payment pages which are critical for merchants to generate revenue and who may be struggling to mitigate these types of threats. 


According to Jscrambler’s report, The Perils of Third-Party Tags: Examining the Client-Side Security Risks and Compliance Challenges of JavaScript, only 36% of respondents’ companies have policies and tools to prevent data skimming. With the launch of these new operationally focused and easy-to-manage payment page script controls, Jscrambler becomes the go-to vendor for merchants looking to achieve compliance and ultimately gain protection from skimming threats. 


Interested businesses need only to provide a payment page URL. Jscrambler will then assess the page, deploy continuous monitoring, deliver a detailed vendor and header inventory, and provide a compliance report within hours. Specific new features that enable this accelerated assessment include:


  • Bulk Script Approvals: Scale a large volume of script approvals, which reduces the time required to approve scripts across multiple payment pages.

  • Automated Workflow Integrations: Seamless Security Information and Event Management (SIEM), email, Slack, and Jira integrations, which deliver real-time alerting, streamlined workflows, and an optimal team experience.

  • Updated Compliance-Ready Reporting: Detailed minute-ready assessment reports that track all vendors, scripts, and authorizations to simplify the assessment process for Qualified Security Assessors (QSA).


“For businesses accepting, storing, transmitting, or processing payment card data, the clock is ticking on a critical compliance deadline they cannot afford to miss. Achieving compliance is vital to their long-term success, and businesses must act now by securing every payment page, detecting unauthorized modifications, and protecting sensitive customer data,” said Rui Ribeiro, CEO and co-founder of Jscrambler.


“With our enhanced PCI DSS solution, merchants gain the levels of compliance needed to eliminate potential penalties, combat digital skimming threats, create a safer environment for handling payment transactions, and ultimately gain the trust and resilience needed in today’s increasingly complex digital landscape, all in a single day.”


These latest capabilities add to Jscrambler’s existing market-leading solution, which includes:


  • Flexible Hybrid Architecture: This architecture enables agentless or agent-based deployment across each payment page. All data is unified within a centralized data ontology that can be accessed through a single dashboard. There’s no lock-in, as businesses accelerate deployment and can flex methods per page as risk changes.

  • Advanced Skimming Detection & Analysis: Advanced static code analysis can identify threats from skimming attacks. By examining web scripts for signs like obfuscation, stealth tactics, and sensitive data access, Jscramblder delivers a thorough assessment to detect and prevent skimming activity on a merchant’s website.

  • Skimming Prevention & Behavior Blocking: Granular script control prevents unauthorized script behaviors from accessing sensitive information while maintaining full functionality.

  • Delegated Compliance: Jscrambler experts manage the script authorization workflows on behalf of clients to reduce the need for additional in-house resources. The service is comprised of three main parts: script management and justification, policy and procedures management, and annual assessment/SAQ guidance. Jscrambler offers unparalleled flexibility, allowing merchants to customize and select only the Delegated Compliance components needed to meet their goals.


In addition to the solution, Jscrambler offers customers an experienced team of PCI DSS experts, including CTO Pedro Fortuna, Security Advisor John Elliott, and Security Solutions Advisor Gareth Bowker. These experts not only work in close collaboration with the Payment Card Industry Security Standards Council (PCI SSC), they also possess a deep understanding of the requirements and experience in helping businesses achieve compliance.


About Jscrambler


Jscrambler is the leader in Client-Side Protection and Compliance. Jscrambler is the first to merge advanced polymorphic JavaScript obfuscation with fine-grained third-party tag protection in a unified Client-Side Protection and Compliance Platform.

Jscrambler’s integrated solution ensures a robust defense against current and emerging client-side cyber threats, data leaks, misconfigurations, and IP theft, empowering software development and digital teams to securely innovate online with JavaScript. Jscrambler’s Code Integrity product safeguards first-party JavaScript through state-of-the-art obfuscation and exclusive runtime protection. Jscrambler’s Webpage Integrity product mitigates threats and risks posed by third-party tags, all while ensuring compliance with the new version 4 of PCI DSS.

With Jscrambler, businesses adopt a unified, future-proof client-side security policy, all while achieving compliance with emerging security standards.  Jscrambler serves a diverse range of customers, including top Fortune 500 companies, online retailers, airlines, media outlets, and financial services firms whose success depends on safely engaging with their customers online.


Jscrambler Wins 2024 CyberSecurity Breakthrough Award

PORTO, Portugal – November 5, 2024

Jscrambler, the pioneering platform for client-side protection, today announced that it has been named Data Leak Detection Solution of the Year in the 2024 CyberSecurity Breakthrough Awards.  Jscrambler detects and defends against data leaks, intellectual property theft, current and emerging client-side cyber threats, and misconfigurations, upholding robust security while enabling businesses to craft advanced online experiences.


CyberSecurity Breakthrough is a leading independent market intelligence organization that recognizes the top companies, technologies, and products in the global information security market. Its mission is to honor excellence and recognize innovation, hard work, and success in a range of cybersecurity projects. Now in its 8th year, The CyberSecurity Breakthrough Awards saw thousands of nominations from all over the world.


“The significant proprietary data leakage risks from third-party website tags have only been exacerbated by AI and algorithm-powered third-party website add-ons that require ever more data to do their job,” said Rui Ribeiro, CEO and co-founder, of Jscrambler. “We’re thrilled that this win acknowledges that a dedicated, purpose-built client-side protection solution is necessary as alternate approaches to client-side protection–such as in-house script-protection solutions, WAF, and Web Application and API Protection security suites–have proven ineffective.”


The only comprehensive client-side protection platform that covers both first- and third-party JavaScript, Jscrambler provides a blanket security and compliance policy encompassing all client-side related risks and regulatory compliance requirements and offers its technology as a managed security service along with expert advisory services.


The platform combines dynamic and behavior-based risk assessment and inventory, fine-grained fencing capabilities, custom data categories and filters, and real-time detection and response capabilities and alerts. Jscrambler also tracks and manages pixel behavior across sections of user websites, and enables users to vet and authorize third-party scripts before they are implemented. Jscrambler’s Sensitive Data Dashboard shows interactions between scripts and sensitive data and uniquely focuses on data, rather than vendor scripts. This shifts the perspective from what vendors are doing with data to which data vendors are accessing, allowing easier and more efficient management of data access rules and ensuring that only authorized vendors or scripts have access to critical data.


About Jscrambler

Jscrambler is the leader in Client-Side Protection and Compliance. Jscrambler is the first to merge advanced polymorphic JavaScript obfuscation with fine-grained third-party tag protection in a unified Client-Side Protection and Compliance Platform.

Jscrambler’s integrated solution ensures a robust defense against current and emerging client-side cyber threats, data leaks, misconfigurations, and IP theft, empowering software development and digital teams to innovate securely online with JavaScript. Jscrambler’s Code Integrity product safeguards first-party JavaScript through state-of-the-art obfuscation and exclusive runtime protection. Jscrambler’s Webpage Integrity product mitigates threats and risks posed by third-party tags, all while ensuring compliance with the new version 4 of PCI DSS.

With Jscrambler, businesses adopt a unified, future-proof client-side security policy, all while achieving compliance with emerging security standards.  Jscrambler serves a diverse range of customers, including top Fortune 500 companies, online retailers, airlines, media outlets, and financial services firms whose success depends on safely engaging with their customers online.


Jscrambler Named Winner of the Coveted Top InfoSec Innovator Awards for 2024

ORLANDO, Fla. – October 31, 2024   Jscrambler, the pioneering platform for client-side protection, is proud to announce it has been named the winner in the Best Solution: Client-Side Protection category in the 2024 Top Infosec Innovator Awards from Cyber Defense Magazine (CDM), the industry’s leading electronic information security magazine.

“We’re thrilled to be a member of this coveted group of winners in the 12th year of Cyber Defense Awards, said Rui Ribeiro, CEO of Jscrambler. “As the provider of the only comprehensive client-side protection platform covering both first- and third-party JavaScript, we couldn’t be more pleased for this further validation of Jscrambler’s innovation and leadership in the Client-Side Protection category.”

“Jscrambler embodies three major features we judges look for with the potential to become winners: understanding tomorrow’s threats, today, providing a cost-effective solution, and innovating in unexpected ways that can help mitigate cyber risk and get one step ahead of the next breach,” said Gary S. Miliefsky, Publisher of Cyber Defense Magazine.

About Jscrambler

Jscrambler is the leader in Client-Side Protection and Compliance. Jscrambler is the first to merge advanced polymorphic JavaScript obfuscation with fine-grained third-party tag protection in a unified Client-Side Protection and Compliance Platform. Jscrambler’s integrated solution ensures a robust defense against current and emerging client-side cyber threats, data leaks, misconfigurations, and IP theft, empowering software development and digital teams to securely innovate online with JavaScript.

Jscrambler’s Code Integrity product safeguards first-party JavaScript through state-of-the-art obfuscation and exclusive runtime protection.

Jscrambler’s Webpage Integrity product mitigates threats and risks by third-party tags while ensuring compliance with the new anti-skimming requirements in version 4 of PCI DSS. With Jscrambler, businesses adopt a unified, future-proof client-side security policy, while achieving compliance with emerging security standards.

Jscrambler serves a diverse range of customers, including top Fortune 500 companies, online retailers, airlines, media outlets, and financial services firms whose success depends on safely engaging with their customers online.

About Cyber Defense Awards

This is Cyber Defense Magazine’s 12th year of honoring cybersecurity innovators, in this case, the Top Global CISOs for 2024, on our Cyber Defense Awards platform. In this competition, judges for these and other prestigious awards include cybersecurity industry veterans, trailblazers, and market makers Gary Miliefsky of CDMG, Dr. Lindsey Polley de Lopez of VentureScope, Katie Gray of In-Q-Tel, Robert R. Ackerman Jr. of Allegis Cyber, Dino Boukouris of AltitudeCyber and with much appreciation to emeritus judges Robert Herjavec of Cyderes, Dr. Peter Stephenson of CDMG and David DeWalt of NightDragon.

About Cyber Defense Magazine 

Cyber Defense Magazine was founded in 2012 by Gary S. Miliefsky, a globally recognized cyber security thought leader, inventor, and entrepreneur, and continues to be the premier source of IT Security information. They are managed and published by and for ethical, honest, passionate information security professionals.

Their mission is to share cutting-edge knowledge, real-world stories, and awards for the best ideas, products, and services in the information technology industry. They deliver electronic magazines every month online for free, and limited special editions exclusively for the RSA, BlackHat, and Cyber Defense Conferences. Cyber Defense Magazine is a proud member of the Cyber Defense Media Group.