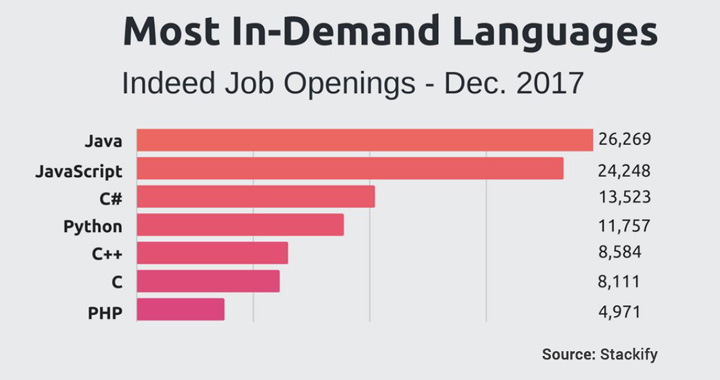
JavaScript’s days as an infant front-end development language are long gone.
During the last few years, it has exploded in popularity. An overwhelming 95% of websites run JavaScript on the front end. JavaScript enables complex processes to run on the client-side, providing much faster access to services such as streaming and transactions.
This popularity created exciting new opportunities for developers and companies, but it also drew hackers’ full attention. Because JavaScript runs on the client-side, the user’s browser becomes an easy point of unauthorized access.
It comes as no surprise that attacks featuring JavaScript code are not rare.
This led us to this initiative—to look back at the most significant attacks, their impact, and how we can learn from them. Because there are so many interesting case studies, we will break this down into a series on App Security Disasters.
Today, we begin with attacks in the eCommerce space.
Ticketmaster’s Payment Data Breach
This incident became public in late June 2018. Ticketmaster issued an alarming statement: a third party breached the platform and accessed the data of around 40,000 UK customers.
Shortly after the breaking news, security analyst RiskIQ identified the perpetrators as the hacker group Magecart. A deeper analysis showed that the leak didn’t affect only 40,000 Ticketmaster customers, but potentially millions.
Magecart had been running a massive credit card fraud operation that affected more than 800 e-commerce websites—potentially the largest credit card skimming operation ever. Some recent attacks, such as the one on British Airways, are being linked to Ticketmaster’s.
RiskIQ’s report found that the breach stemmed from malicious JavaScript injected into a module custom-built by Inbenta for Ticketmaster.
Because the code was unprotected, attackers could retrieve credit card information. Inbenta released a statement saying its module shouldn’t run on payment pages because it poses a major security threat.
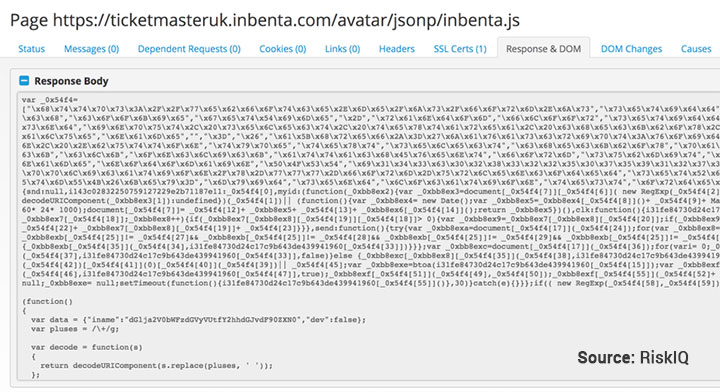
Because Ticketmaster had no web page monitoring system, the company took a long time — reportedly, two months — to identify and address the attack.
Outcomes
At the time of writing, this incident is still fresh. As the dust starts to settle, some consequences become notorious:
- Payment data of potentially millions of users was stolen, including Personally Identifiable Information (PII);
- Numerous Ticketmaster customers reported fraudulent transactions;
- Ticketmaster may face some heavy fines, given the EU’s strict GDPR policies;
- Both Ticketmaster and Inbenta faced severe PR backlash.
Identity theft is no simple matter—nor is it a small PR nightmare. All guilt games aside, both companies still face a long road of damage control.
Klook’s Data Breach
While talk of the Ticketmaster incident was still abuzz, another data breach came to light, again driven by a JavaScript attack.
Hong Kong-based Klook, a leading travel services booking platform, released a public statement regarding a customer data leak on its website.
The data breach was attributed to malicious JavaScript code injected into a third-party tool—SOCIAPlus—which was being used on Klook’s website.
Although Klook acted quickly after uncovering the issue, attackers accessed the personal data and credit card information of about 8% of Klook’s users from December 2017 to June 2018—a total of six months.
Outcomes
Given the known details and outcomes of similar past breaches, we can expect to see:
- A rise in phishing attempts targeting affected Klook customers;
- Reports of credit card fraud;
- Potential legal action against Klook and the company responsible for the third-party tool.
OnePlus’ Clients Credit Card Leak
“We cannot apologize enough for letting something like this happen”.
OnePlus is a rising smartphone brand that surpassed US$1 billion in revenue just 3 years after its inception. Most of its sales come from its own eCommerce website, which debuted in 2014.
Early in 2018, OnePlus customers began reporting credit card fraud after purchasing through the eCommerce platform, and the news quickly became public.
The company’s website used Magento—an open-source platform commonly used for eCommerce sites.
During checkout, customers entered credit card details on a page hosted on-site. Because the code was unprotected, hackers could inject malicious JavaScript that captured the credit card data.
Outcomes
OnePlus suspended credit card payments, warned its customers, and offered free credit monitoring. However, significant damage was done:
- Approximately 40,000 affected customers, many of whom were victims of fraudulent transactions;
- Severe criticism for not following PCI guidelines — a set of security standards for credit card payment handling;
- A considerable dent in the company’s reputation, directly impacting its customers’ trust.
Final Thoughts and Lessons Learned
Attacks on eCommerce websites are extremely frequent. In the U.S., 6% of all websites use Magento, and many others rely on platforms with known vulnerabilities, including WooCommerce and Squarespace.
Running unprotected JavaScript code is a recipe for disaster.
Server-side security systems can’t protect against these attacks. Companies are only now realizing the danger of client-side threats—and mostly because of the recurrently reported attacks.
Ticketmaster and Klook’s cases show that protecting their own code is often not enough. Both couldn’t monitor the web pages where third-party modules ran, so they had zero visibility into these threats.
Jscrambler ensures the most advanced JavaScript code protection and real-time page monitoring. With Jscrambler’s leading solutions, JavaScript code becomes self-defensive, and companies gain full visibility into every threat to their eCommerce site’s integrity.
With so much breaking news this week about Magecart infecting potentially thousands of eCommerce websites, we’re providing a Webpage Threat Analysis at no cost. Don’t wait any longer to see if your website is being infected.
Security is not a blame game. Growing businesses face fiercer attacks every day, and decision-makers must evolve their security with state-of-the-art solutions.
Hackers’ ability to compromise websites has evolved. Our knowledge and readiness must be several steps ahead. Is your business prepared?