Password managers are valuable tools that help individuals and organizations strengthen their digital security.
By securely storing and auto-filling login credentials, password managers offer convenience and the ability to generate strong, unique passwords. However, password managers are not infallible.
This blog post explores a potential security concern with auto-filling inputs and how users can mitigate the risks.
The Danger of Automatic Auto-Filling
While password managers are designed to enhance security, their automatic auto-fill functionality can inadvertently introduce risks.
The primary danger is that a password manager may automatically fill in credentials for untrusted or malicious websites. This can happen when attackers manipulate website elements or create convincing phishing sites that deceive password managers.
If users rely on auto-fill without verifying the page’s legitimacy, adversaries could expose login credentials and compromise accounts.
Auto-Filling Sandboxed Iframes
In January, Google published an advisory informing users that “multiple password managers can be tricked into auto-filling credentials into untrusted pages“. Hence, it could “lead to account compromise for any users using these password managers“.
We found this happening in Safari and in Bitwarden and Dashlane extensions, where they would automatically auto-fill credentials in forms embedded in sandboxed iframes. By the time we published this advisory, these vulnerabilities had already been fixed.
What about Unsandboxed Iframes?
Our security research team tested common browsers and password managers to determine how they behave with same-origin and cross-origin iframes that are not sandboxed.
We created a test page that included four different scenarios when using iframes:
- Same-Origin iframe without sandboxing;
- Same-Origin iframe with sandboxing;
- Cross-Origin iframe without sandboxing;
- Cross-Origin iframe with sandboxing;
With these tests, we expect only same-origin, unsandboxed iframes to be filled.
1. Firefox
We observed that Firefox behaves as expected. The autofill feature only fills the same-origin unsandboxed iframe and ignores all other cross-origin or sandboxed iframes.
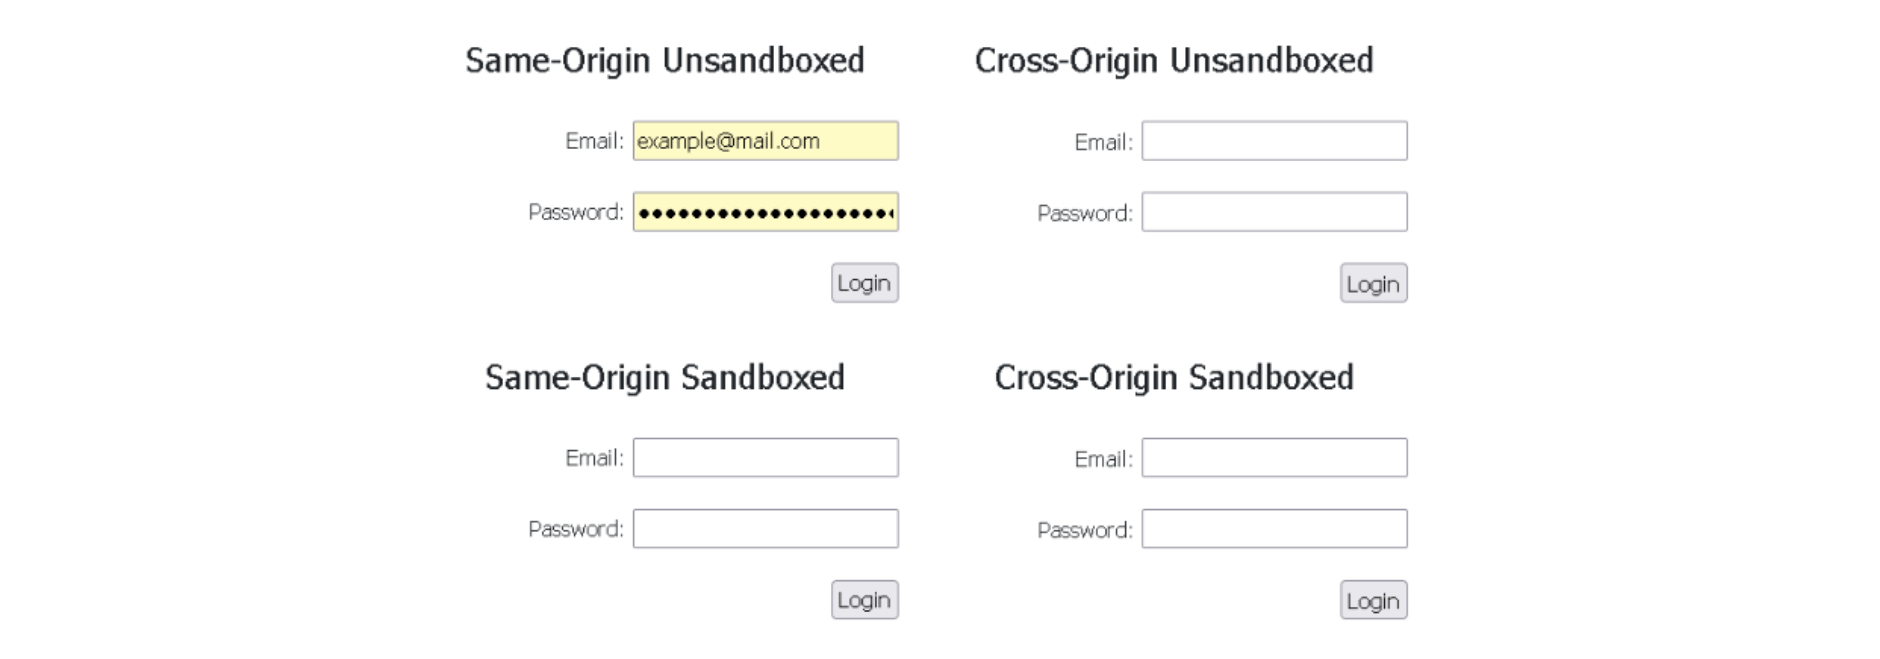 Image 1: Firefox browser only auto-fills the same-origin unsandboxed iframe
2. Chrome
Like Firefox, Chrome also displays the correct behavior. The autofill feature will only fill the same-origin unsandboxed iframe, ignoring all other cross-origin or sandboxed iframes.
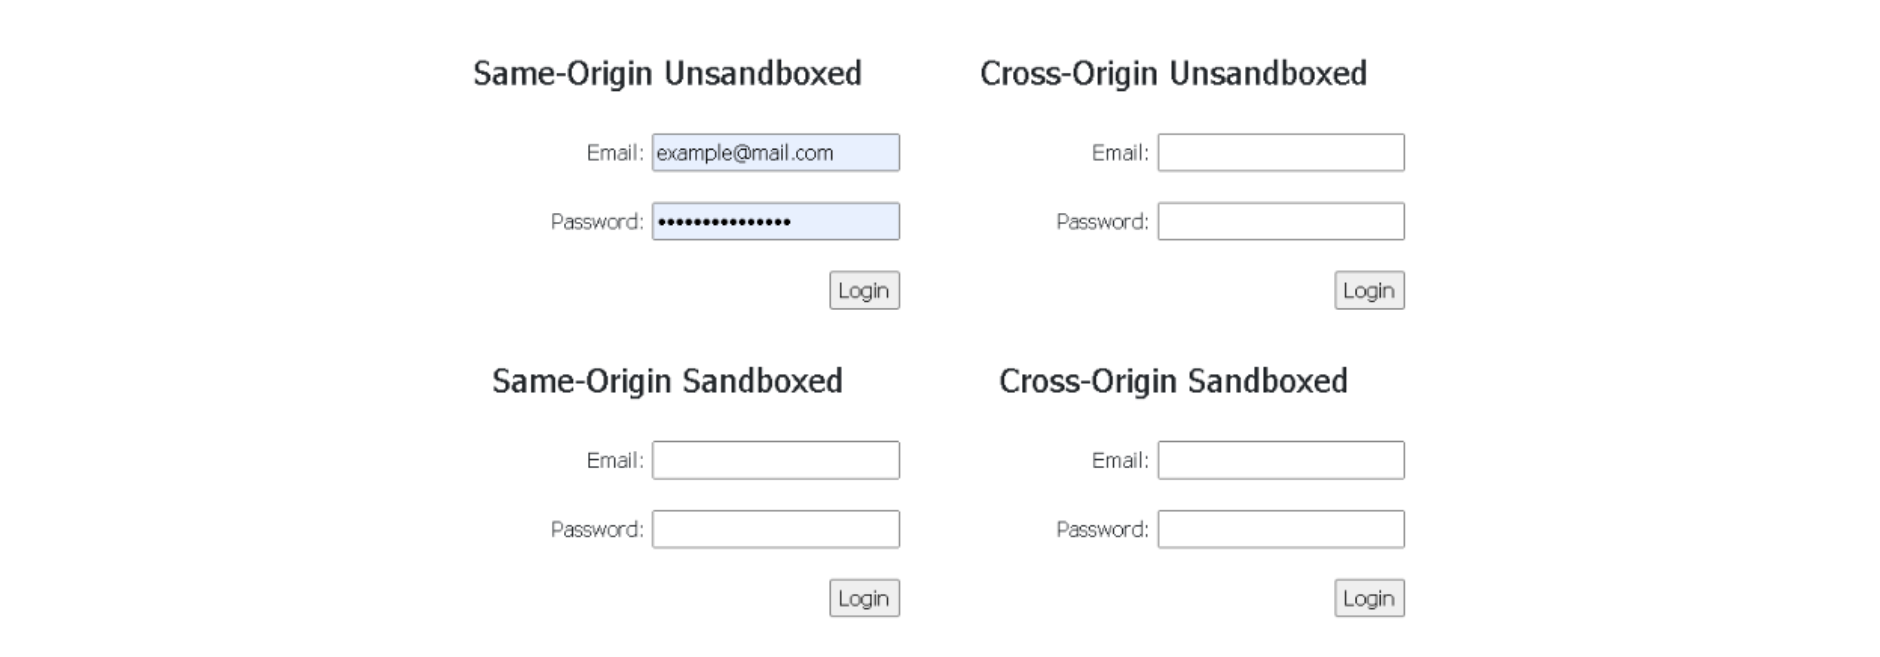 Image 2: Chrome browser only auto-fills the same-origin unsandboxed iframe
3. Edge
The Edge browser showed slightly different behavior.
Even though it will still only autofill the password field on the same-origin unsandboxed iframe, as we expected, it will also autofill the username or email field in cross–origin or sandboxed iframes without warning the user that information will be sent to an external domain, which can be considered a security issue.
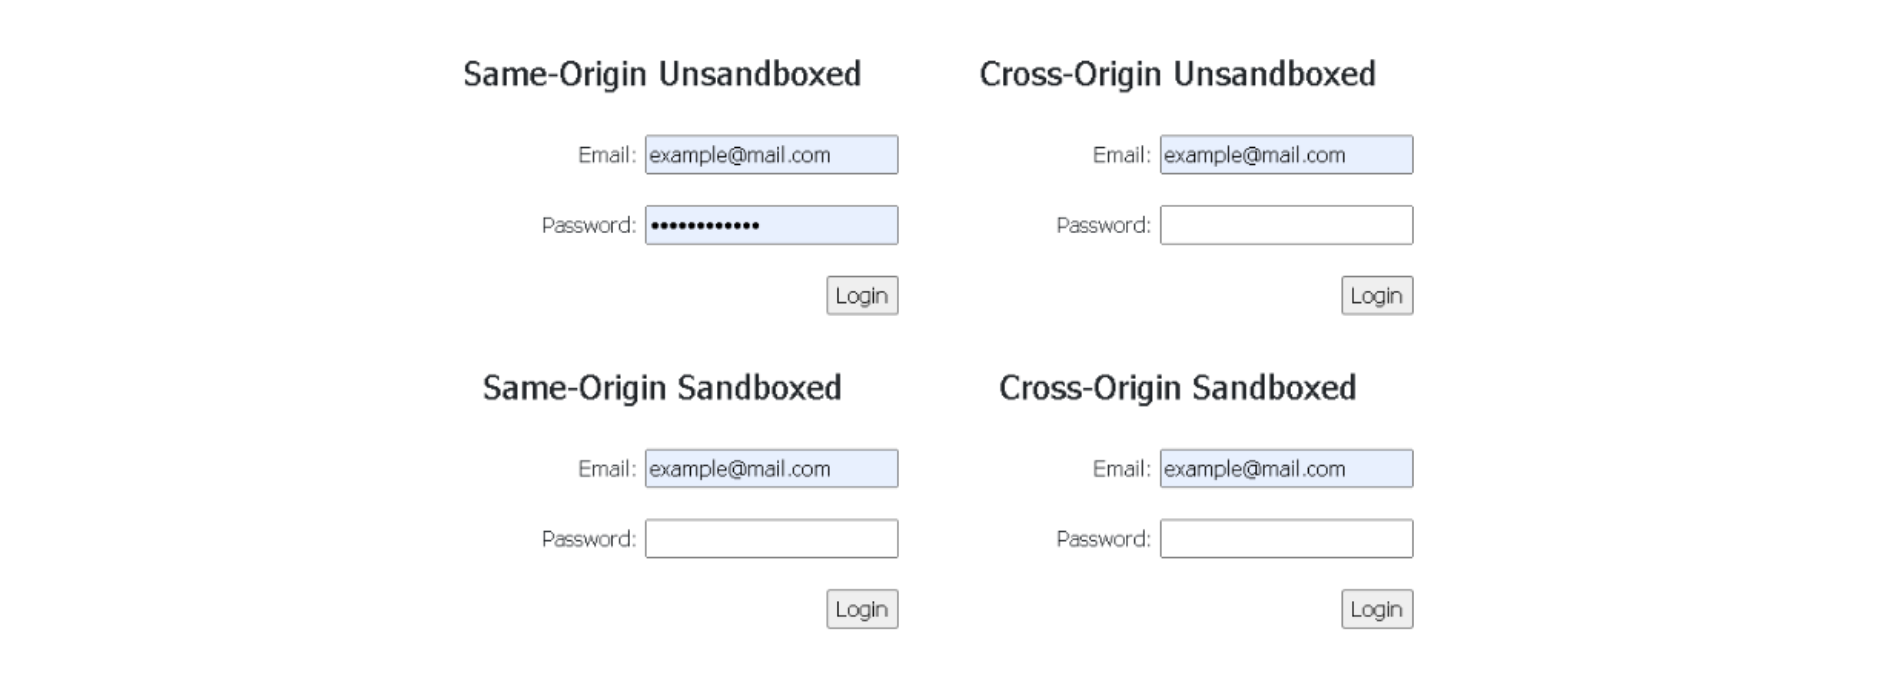 Image 3: Edge browser auto-fills username/email fields in all iframes
4. Bitwarden
Bitwarden shows a warning prompt, informing the user that the credentials are about to be sent to a domain different from the current one.
This prompt lets the user decide whether he actually wants that form auto-filled or not, and if he accepts, the extension will auto-fill unsandboxed cross-origin iframes.
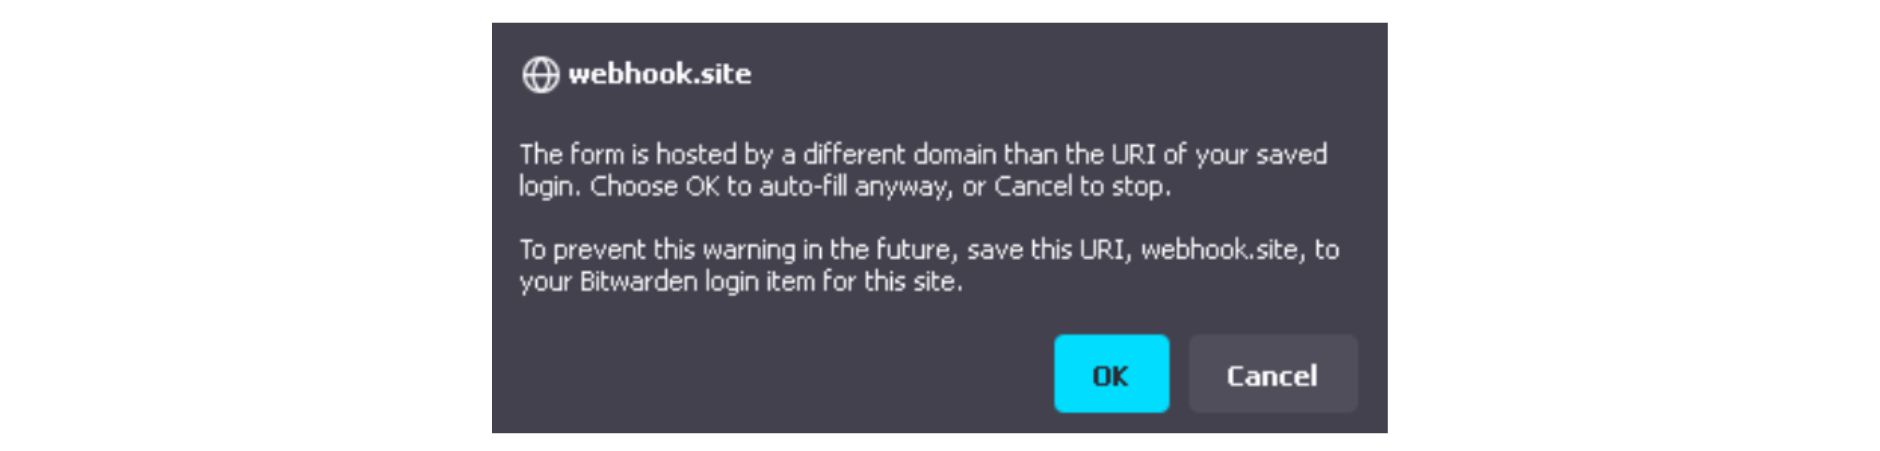 Image 4: Bitwarden extension warning the user about auto-filling cross-origin iframes
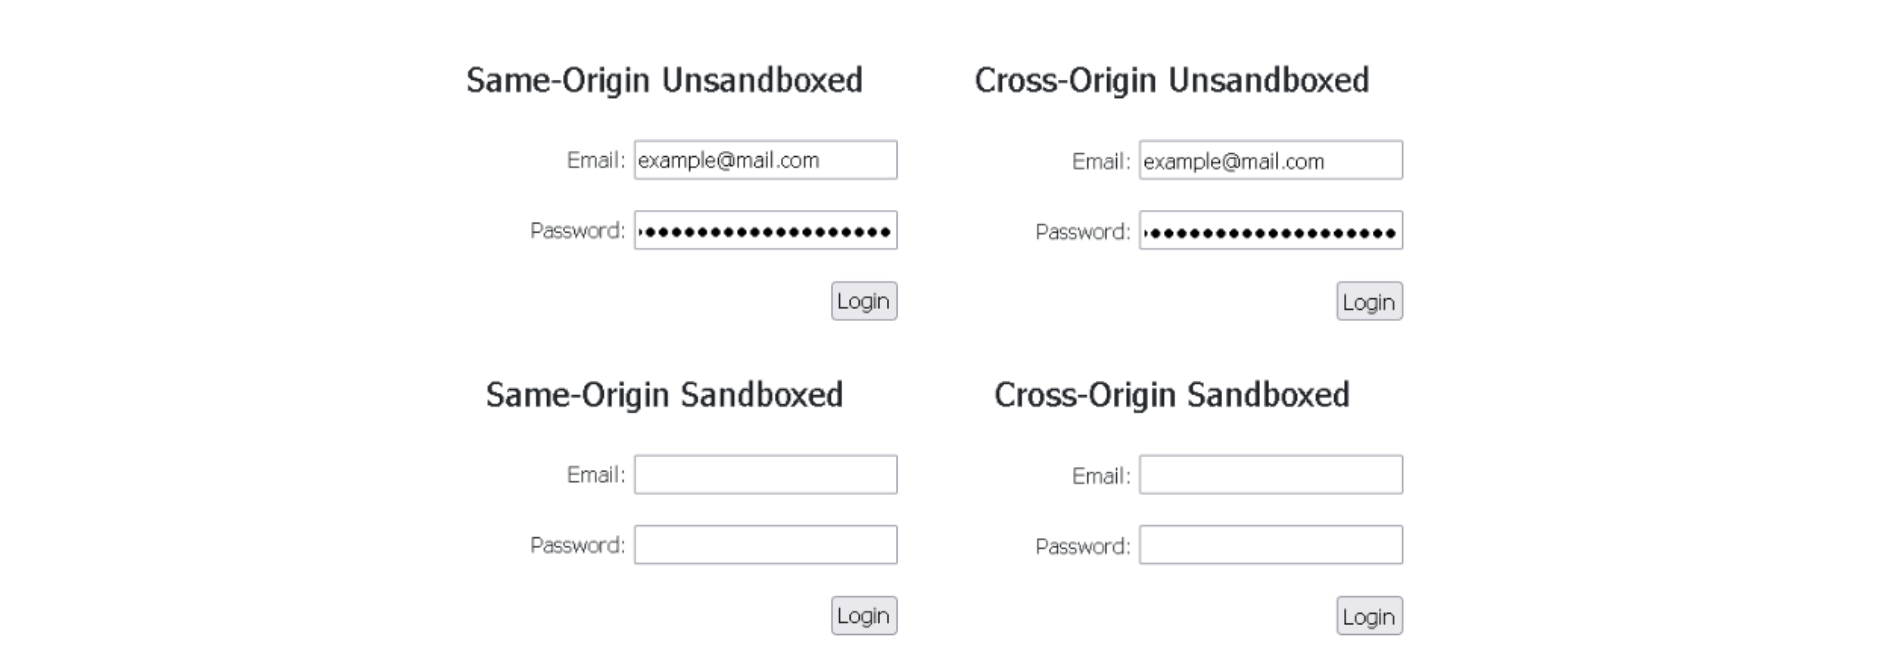 Image 5: Bitwarden extension filling same-origin and cross-origin iframes, if the user consents
5. LastPass
Like Bitwarden, LastPass will also show a warning prompt to the user, informing them that the credentials are about to be sent to a domain that is different from the current one. If he accepts, the extension will also auto-fill unsandboxed cross-origin iframes.
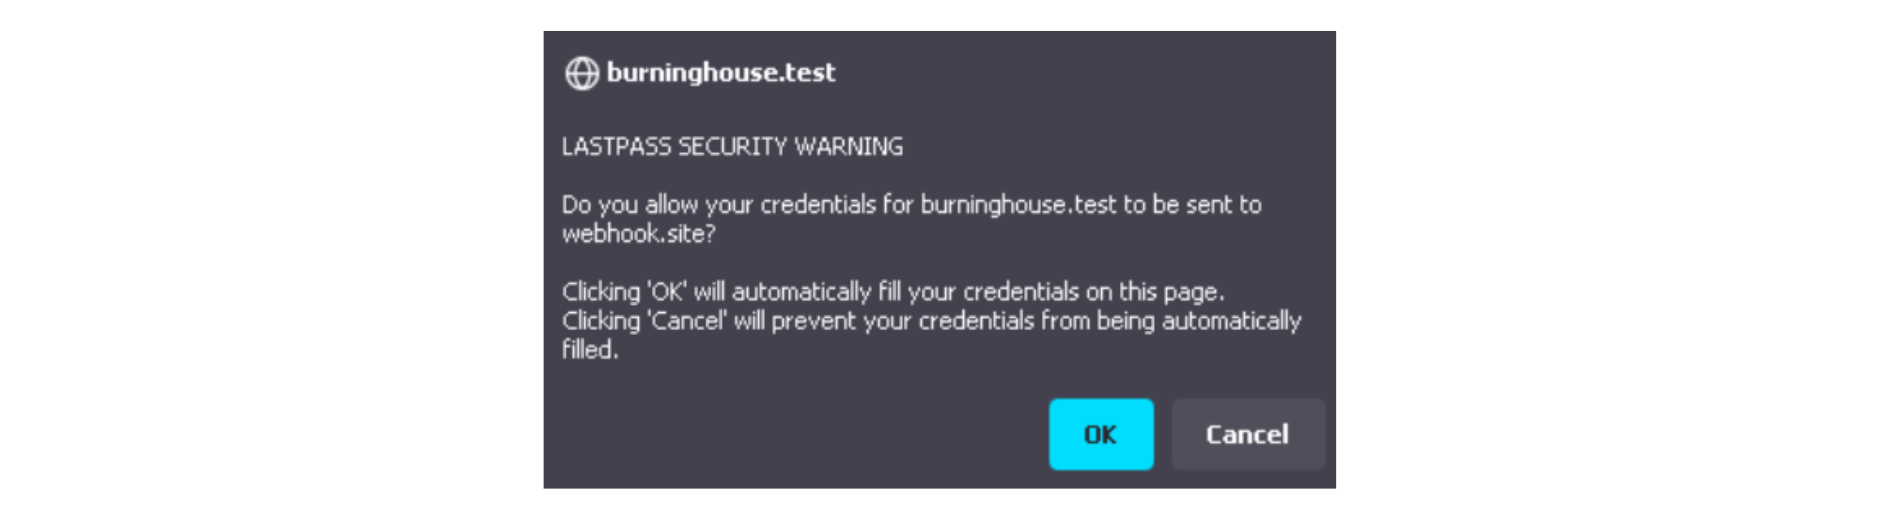 Image 6: LastPass extension warning the user about auto-filling cross-origin iframes
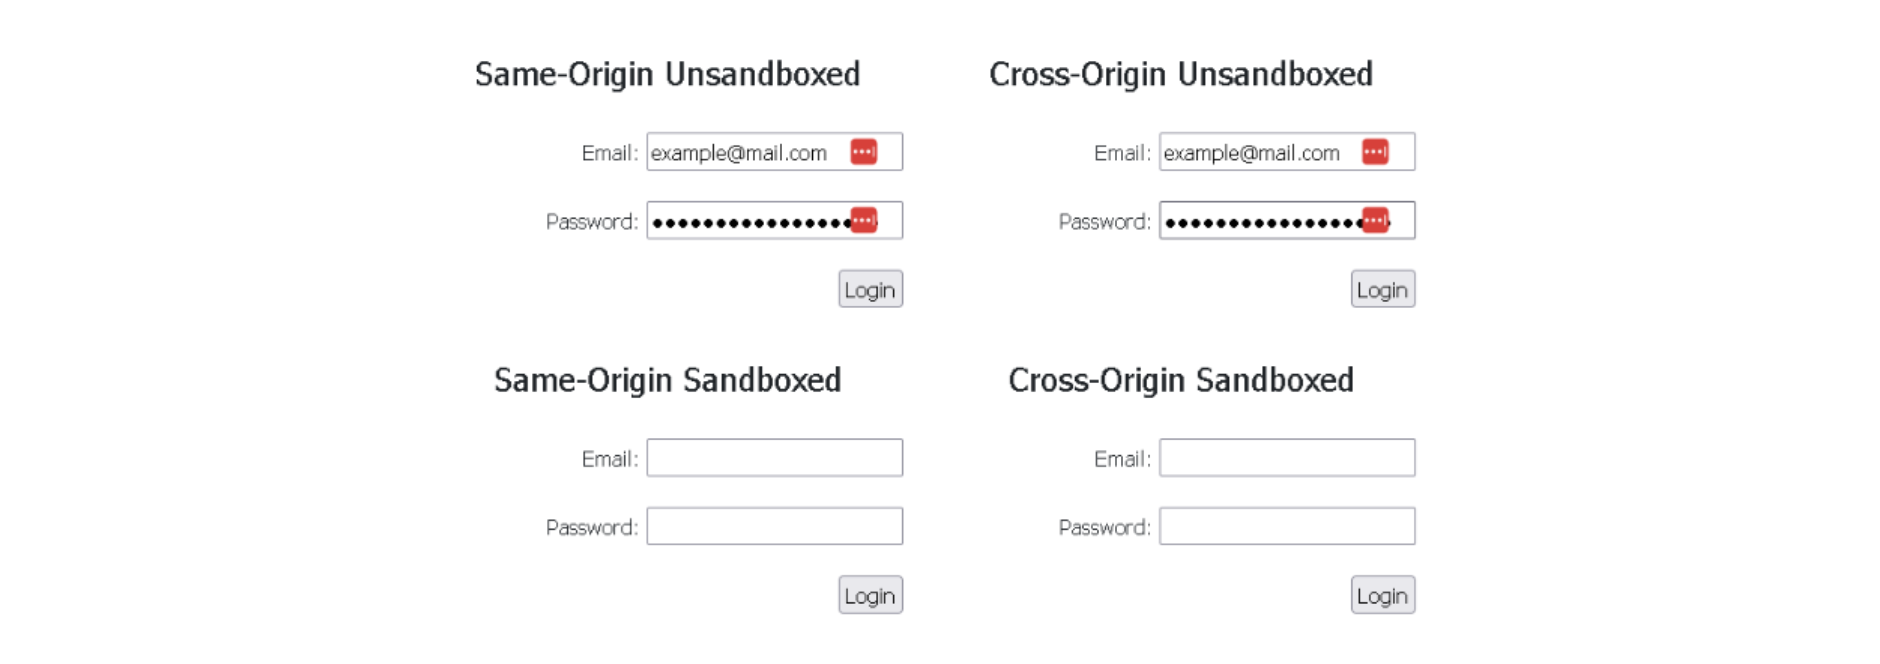 Image 7: LastPass extension filling same-origin and cross-origin iframes, if the user consents
6. Passbolt
From the password managers that were tested, Passbolt was found to be one of the most secure, as it does not auto-fill or even present the auto-fill option to the user in cross-origin or sandboxed iframes.
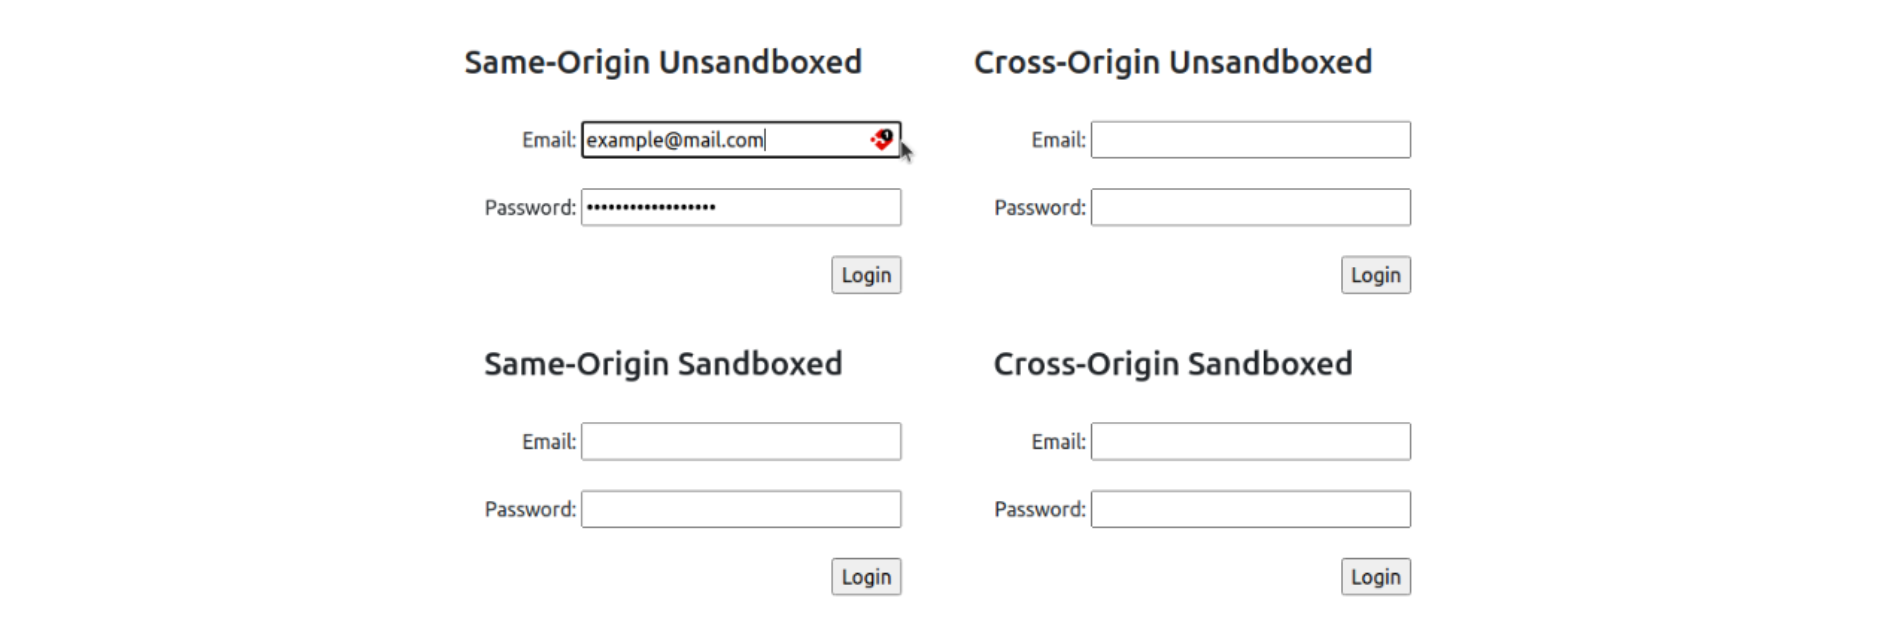 Image 8: Passbolt extension only auto-fills the same-origin unsandboxed iframe
7. 1Password
1Password also displayed the behavior we were expecting. It does not auto-fill or even present the auto-fill option to the user in cross-origin or sandboxed iframes, just like Passbolt.
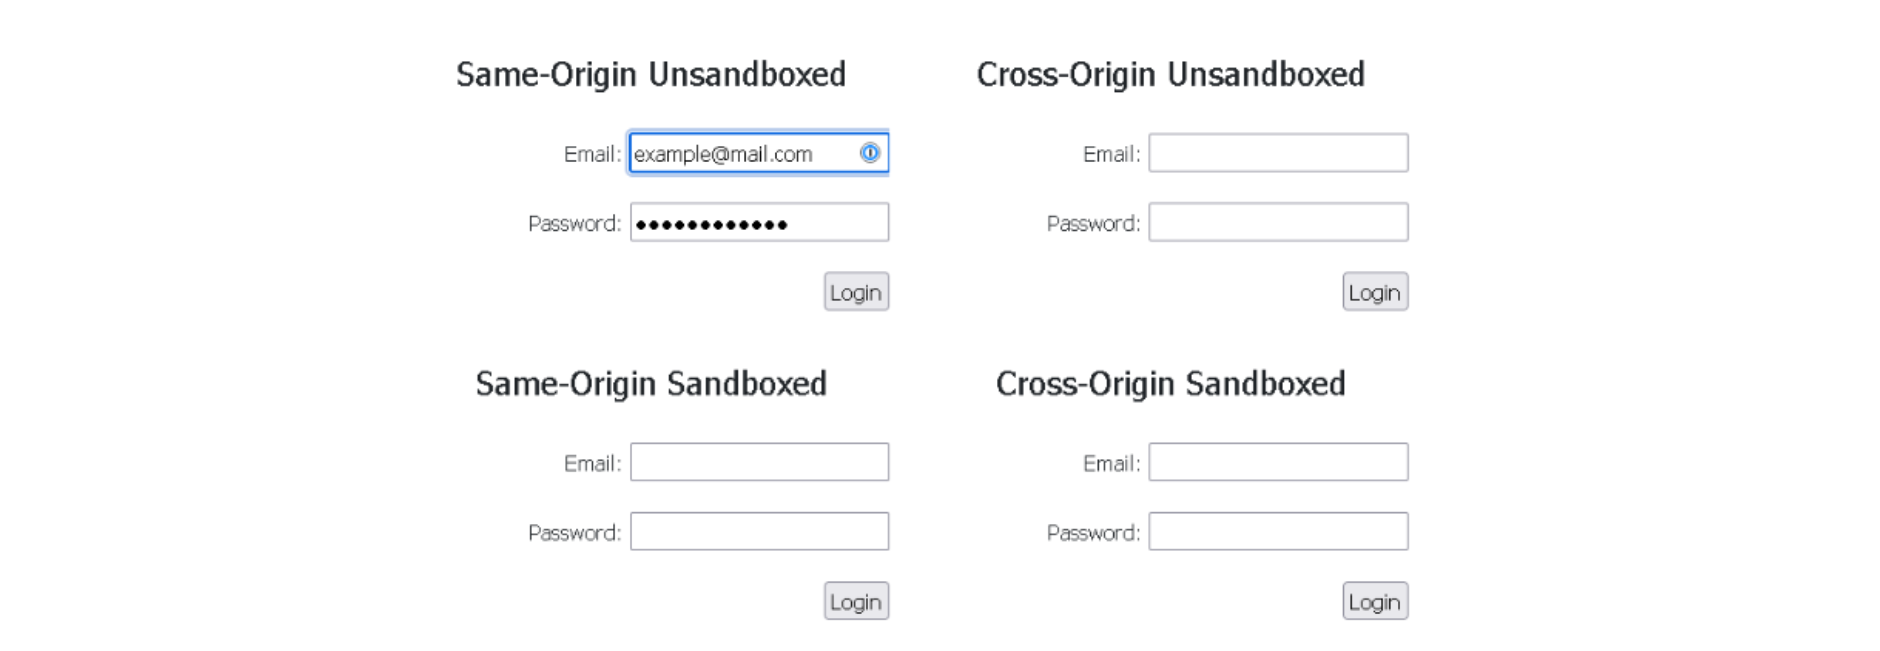 Image 9: 1Password extension only auto-fills the same-origin unsandboxed iframe
Conclusion
While password managers are powerful tools for enhancing online security, users must remain vigilant and understand the potential risks of auto-fill.
We suggest that users disable the automatic auto-fill feature in their password managers and instead trigger auto-fill manually only when they are confident the form is legitimate and should be filled.
Remember, secure password management depends not only on the technology but also on the user’s responsible, proactive approach to online security.