Healthcare organizations ushered in the new year with the stark realization that healthcare data breaches were rampant in 2024. New Year’s resolution or not, it’s time to strengthen client-side protection against data loss, security vulnerabilities, and malicious threats.
The data doesn’t lie; 2024 marked a record-breaking year for healthcare-related data breaches in the U.S. and globally. According to the U.S. Department of Health and Human Services’ Office for Civil Rights, by December 20, 2024, 677 major healthcare data breaches had affected more than 182.4 million people that year alone. Hacking and IT incidents were the most significant attack type, and client-side threats can let attackers steal sensitive medical data, leading to larger attacks, privacy violations, and financial losses.
Recent data shows that third-party tracking technology is present on nearly 99% of “hospital websites, which includes transfers to large tech companies, social media companies, advertising firms, and data brokers.”
The omnipresence of these technologies demands that the healthcare industry proactively protect patient data, mitigate data leakage, and prevent bad actors from executing malicious code by injecting scripts or manipulating client-side application functionality.
Identifying Client-Side Vulnerabilities for Healthcare Data
When discussing threats to data integrity, people often assume a bad actor is actively working to compromise systems to access valuable data. It is a fair assumption. However, because of how third-party vendor services operate, sensitive user data can be unwittingly exposed to unauthorized access when third-party tags (or scripts) appear on pages where they should be restricted. And in many scenarios, that is the case. However, some third-party tagging technologies can unwittingly expose sensitive user data to unauthorized third parties.
Take data leakage, for instance. Data leakage via third-party tags happens when an organization inadvertently exposes sensitive user information by allowing third-party tags to “roam” the website freely, including login and payment data forms. Vulnerabilities in third-party vendor software or misconfigurations can lead to unauthorized access to customer, patient, or user data.
When a website integrates code from a third-party ad network, analytics platform, or other service, the code may unintentionally collect and transmit user data, such as browsing history, demographics, or personal details like date of birth or Social Security numbers, to unauthorized third parties. Even small leaks can lead to significant consequences, including legal issues, identity theft, financial loss, and operational disruption. With multiple tags from various sources running on websites, the risk of data leakage grows exponentially.
Another more intentional threat is digital skimming. Digital skimming is a fraudulent process that captures and transfers payment card data. It involves bad actors injecting malicious code into third-party scripts on a website. The code then skims credit card data when users enter it into payment forms.
Because hackers continuously look for vulnerabilities to exploit, client-side vulnerabilities can be especially appealing. By exploiting weaknesses in the applications the end user is actively using, attackers can not only steal data from a client device but also install malware and gain unauthorized access to systems.
Hackers target client-side vulnerabilities because they are less secure and give them direct access to user data such as login credentials or credit card details. The client side also presents a much wider attack surface because of the number of applications and browser extensions running on an end-user device. Hackers also rely on users not keeping software up to date, leaving known vulnerabilities open to attack.
For healthcare organizations, this can negatively impact patient care and create a range of other risks. The adverse outcomes of client-side data breaches run the gamut of:
- Disruption of patient care: When healthcare data are compromised, it can delay treatment, make records hard to access, and disrupt essential medical procedures.
- Data breaches: Hackers exploit vulnerabilities in web applications to steal sensitive data such as diagnoses, prescriptions, and insurance details—which can lead to privacy violations, identity theft, and potential lawsuits and settlements.
- Digital skimming attacks: Bad actors use the lack of visibility into third-party scripts on websites to introduce malicious code into the patient’s browser, primarily to steal cardholder data.
- Phishing attacks: Attackers create a fake or mirrored website hosted on a fraudulent URL to trick end users into divulging personal and sensitive information.
- Reputation damage: A data breach can significantly damage a healthcare organization’s reputation, ultimately eroding patient trust and business.
Tracking Codes and Compliance
While common across websites, third-party tracking codes must follow different rules on healthcare provider sites.
Healthcare websites use third-party trackers to improve provider services, but the same technology becomes a risk vector when it shares unauthorized data with technology providers. Examples of third-party tags include the Meta Pixel, Google Analytics, LinkedIn Insights, Snapchat Pixel, TikTok Pixel, Twitter conversion tracking, and other custom tracking pixel tags implemented by a third-party ad network or marketing platform.
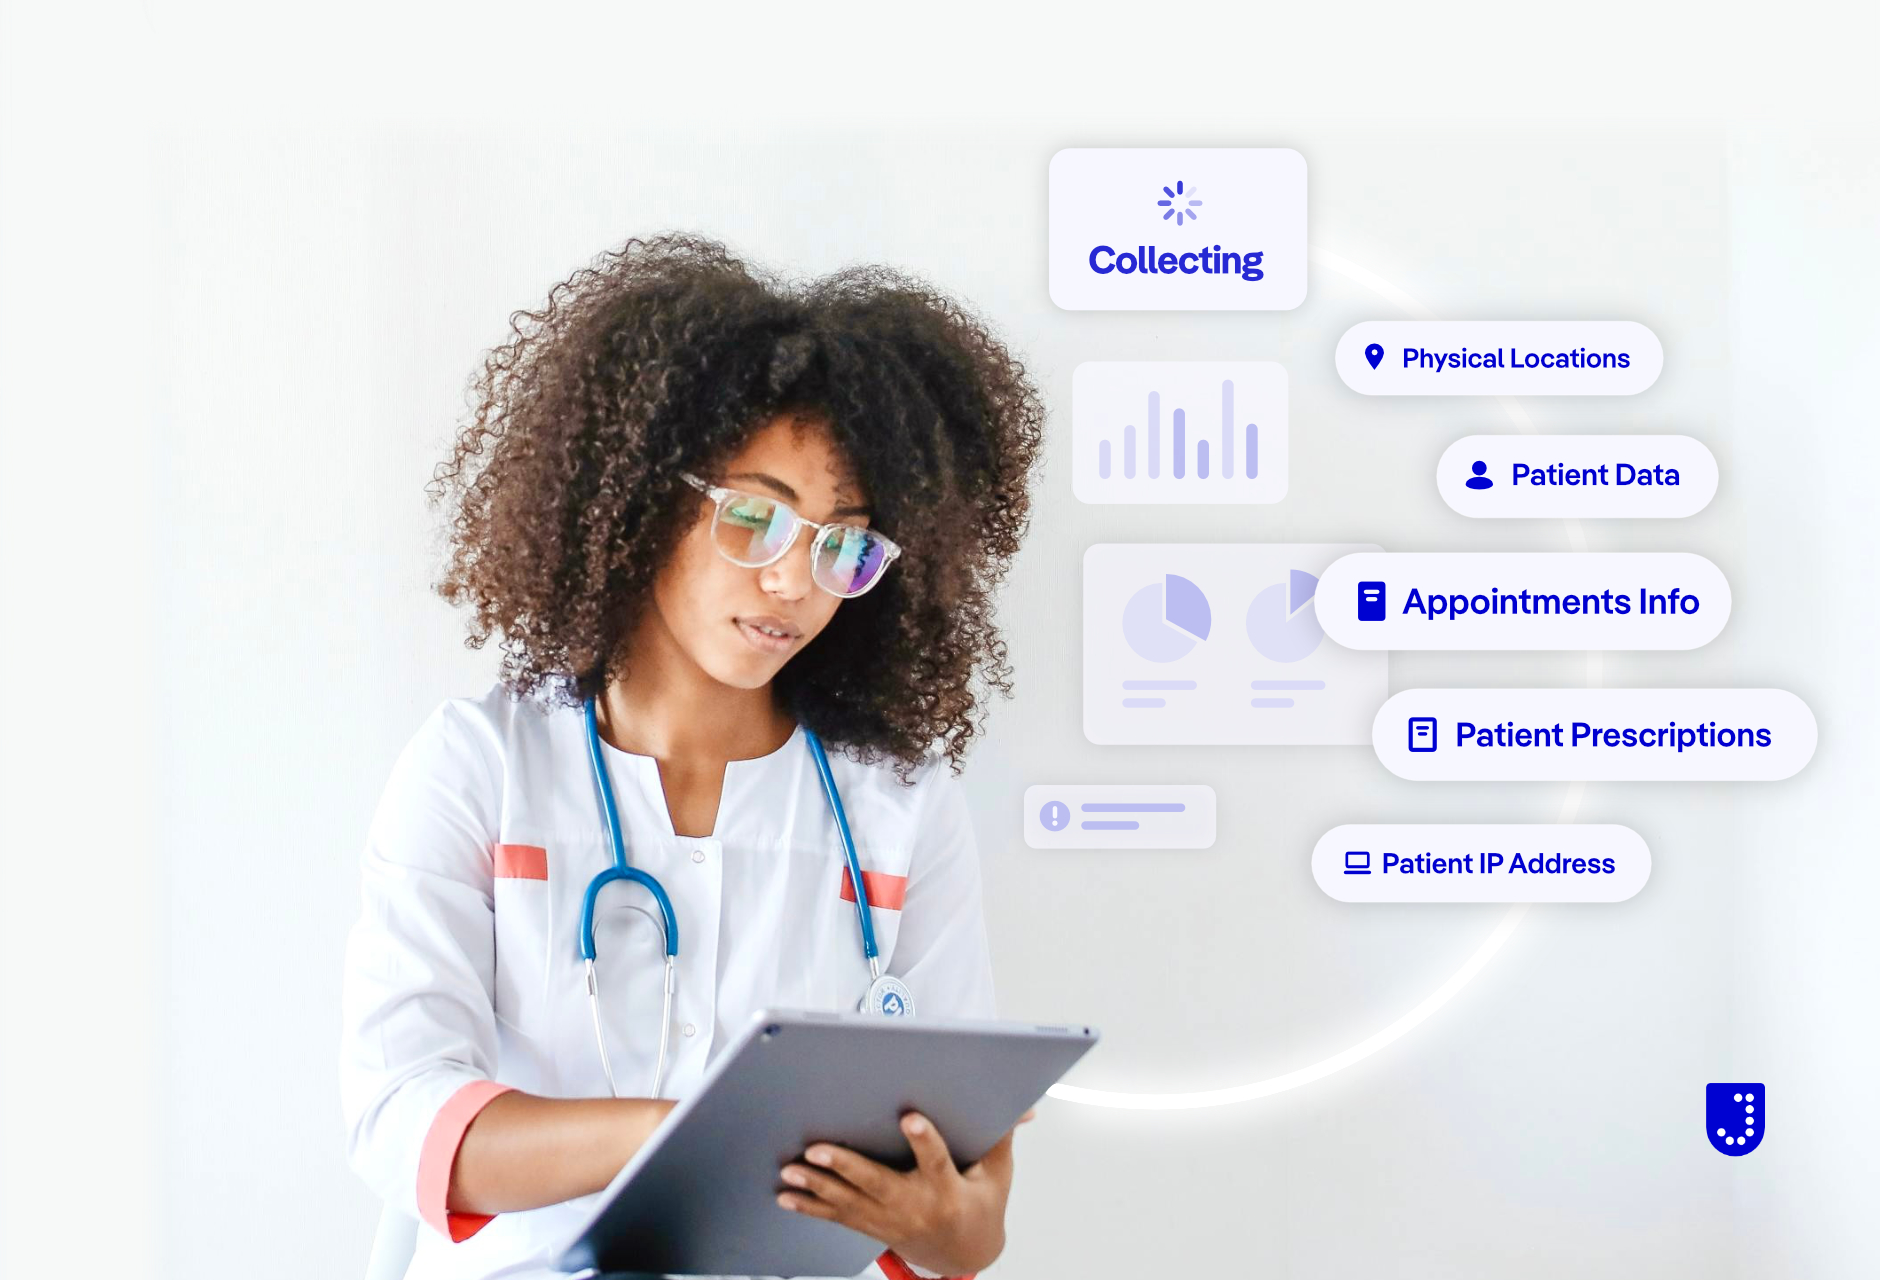
These code snippets utilize cookies, web beacons, pixel tags, and other tracking technologies to identify users across different websites. The data collected can help healthcare providers understand patient behavior, identify trends in health needs, improve website usability, and deliver more personalized, proactive care. Problems arise when third-party tracking technologies put patient privacy at risk and when data collectors potentially misuse sensitive health information. A lack of transparency about how data is collected and used can also put healthcare providers in a precarious compliance position.
Guidance from the U.S. HHS Office for Civil Rights explains that HIPAA-regulated organizations must have a business associate agreement (BAA) in place with the code provider or obtain patient authorization—or face violations of the Health Insurance Portability and Accountability Act. And while the guidance is clear, a recent analysis of healthcare websites found that one-third of those websites analyzed still use Meta Pixel tracking code—even with the risk of repercussions such as “lawsuits, data breaches, and fines for non-compliance with the HIPAA Rules.”
For instance, Novant Health settled a $6.6 million pixel privacy breach lawsuit in January 2024. The Lawsuit involved pixel code that collected personally identifiable information on their patient portal, intending to improve care with virtual visits. In this case, the tracking pixels also transferred data from more than 1.3 million individuals to third-party technology companies not authorized to receive it.
Closing the Loop on Client-side Threats
Fortunately, healthcare organizations can follow key security steps to keep this year’s resolution and protect their end users on the client side.
To safeguard against client-side attacks, healthcare organizations can implement strict access controls, deploy robust endpoint protections, conduct regular security audits, protect mobile devices, limit network access, educate employees on cybersecurity best practices, and more. Client-side protection platforms provide an additional layer of security against hackers and data leakage by protecting end users as they interact with websites and applications in a few critical ways.
Managing Script Inventory
By automatically identifying all third-party vendors and scripts present on each web page, script inventory management allows users to maintain a real-time list of all scripts running on their website—including third-party tags. This provides visibility into potential security risks and helps ensure organizations stay compliant with regulations such as PCI DSS. Client-side protection platforms provide comprehensive script tracking by identifying and managing potentially unauthorized scripts on payment pages.
Blocking Access to Data
By identifying and limiting third-party vendors’ access to forms and the data entered into them, client-side protections such as form fencing let clients control which scripts can read and access form data. These platforms offer powerful and granular rule engines that give healthcare organizations full control of each script running on their website.
Controlling Data Exfiltration
By setting specific rules for how third-party tags interact with data, protection platforms can restrict access to sensitive information and prevent unauthorized data transfer.
Stopping Formjacking and Magecart Attacks
By monitoring and securing forms on healthcare websites, client-side protection can stop attackers from capturing sensitive data, such as patients’ searched healthcare interests. Client-side protection can also prevent Magecart attacks, which target e-commerce sites by injecting malicious code into checkout pages and allowing threat actors to skim user card details in the HTML form.
Detecting Threats and Data Leakage in Real Time
By continuously monitoring end-user sessions, client-side platforms can spot suspicious activity, intervene quickly, and mitigate threats. For instance, client-side protection platforms can identify potential data leaks by analyzing how third-party tags interact with sensitive data on a website.
Complying with Standards & Regulations
By adding client-side protections, healthcare organizations can meet data privacy regulations like HIPAA and PCI DSS v4 when accepting payments on their websites.
Jscrambler provides even more protection against client-side data leakage and attacks, benefiting healthcare providers.
- Comprehensive: Jscrambler is the only client-side security and compliance platform to natively combine first-party JavaScript obfuscation with third-party tag protection. Jscrambler’s Code Integrity obscures JavaScript used in healthcare, making it harder for hackers to understand the code and exploit vulnerabilities to steal patient data. Jcrambler’s Webpage Integrity blocks unauthorized behavior and offers protection against data breaches, form jacking, web skimming attacks, and data exfiltration.
- Fine-Grained Control: Employ fine-grained rules for managing forms and sensitive data. Our solution provides real-time detection and response, issuing alerts for suspected fraudulent or risky activity.
- Top-Notch Performance: Jscrambler is designed to scale effortlessly to the largest and most demanding websites without slowing down or disrupting the online user experience.
- Sweeping Client-Side Security & Compliance Policy: Jscrambler is unique in its ability to support all involved teams (product management, software development, security, digital, marketing, and governance, risk, and compliance) in formulating a centralized security policy that encompasses all client-side risks and regulatory compliance requirements. The policy is sweeping, comprehensive, fine-grained, company-wide, and future-proof. Out of the box, businesses can comply with one or several security standards, including HIPAA, PCI DSS v4, PSD3, and others.
- Trusted Expertise: Jscrambler helps clients succeed with its industry-leading platform at every step. For third-party tags, skilled consultants can guide clients in setting up the best risk-mitigation strategies, including appropriate data-fencing tactics. Jscrambler also offers Managed Services for PCI DSS v4 Compliance (requirements 6.4.3 and 11.6.1), so security teams don’t have to manage script authorizations or worry about compliance.
Learn more about how Jscrambler can help healthcare organizations mitigate the risk of client-side attacks.