Enterprise JavaScript apps face opportunities, threats, and solutions, just like web, mobile, and desktop apps with cross-platform development.
If you’re working with JavaScript, it’s entirely likely that you’re familiar with its history. The 24-year-old programming language has evolved drastically in recent years, especially with the advent of Node.js and JS frameworks.
If JavaScript was once a gimmick that made websites dynamic and more enjoyable, the landscape is quite different today. JavaScript is the powerhouse of the web.
A staggering 97% of modern web apps use JavaScript, and every single Fortune 500 company relies on Node.js and JavaScript to create highly competitive web and mobile applications.
As Progressive Web Apps gain traction as a viable alternative to native apps, this growth will likely accelerate. JavaScript isn’t only for the web; it also powers desktop and mobile apps through cross-platform development.
With all its numerous advantages and business value, we must still consider the other side of the coin: the considerable security threats linked to using JavaScript.
JavaScript: Threats
JavaScript needs to be rendered by a browser in order to work. This means that it can’t be encrypted in a feasible way. Then, JavaScript code is completely exposed and anyone can access, read, and modify it.
At first glance, we could argue this won’t be a problem as long as companies don’t store important business logic on the client side. But server calls take time, and in performance-critical services such as streaming, e-commerce, or gaming, that is not an option. So, companies put proprietary algorithms on the client side for performance.
When we combine these two ingredients — proprietary algorithms and an exposed environment — we get a recipe for disaster. For a long time, malicious actors have exploited exposed JavaScript, stealing this code and redistributing copycat apps. But that’s just the tip of the iceberg.
Exposed JavaScript opens the door to automated abuse. For instance, a cloud provider may offer 1 month free for new accounts, and this can be abused by malicious actors through automated account creation. This is especially relevant in use cases where relying on CAPTCHAs is not feasible.
To prevent account takeover and combat fraud, several companies deploy JavaScript agents to block bots or provide device fingerprinting. However, because these agents’ code is exposed, attackers can reverse-engineer it and bypass them.
Then there’s cheating and piracy. Attackers can exploit exposed JavaScript to bypass app restrictions, unlock features without paying, or violate licensing agreements—all of which threaten a company’s business model.
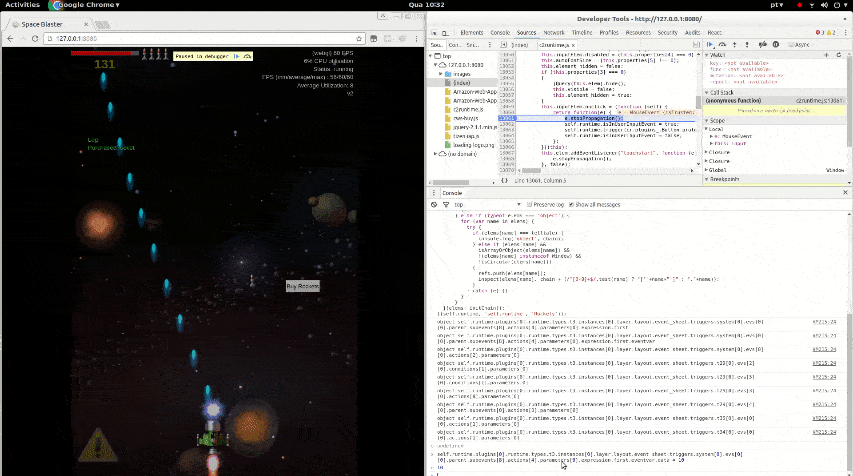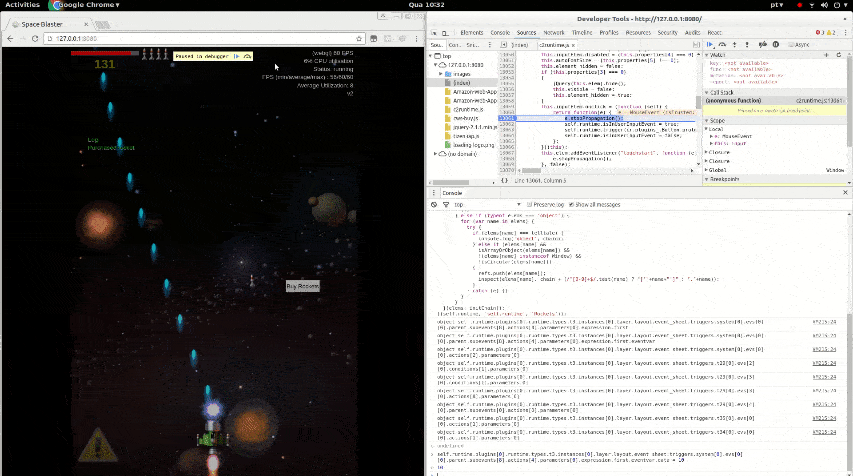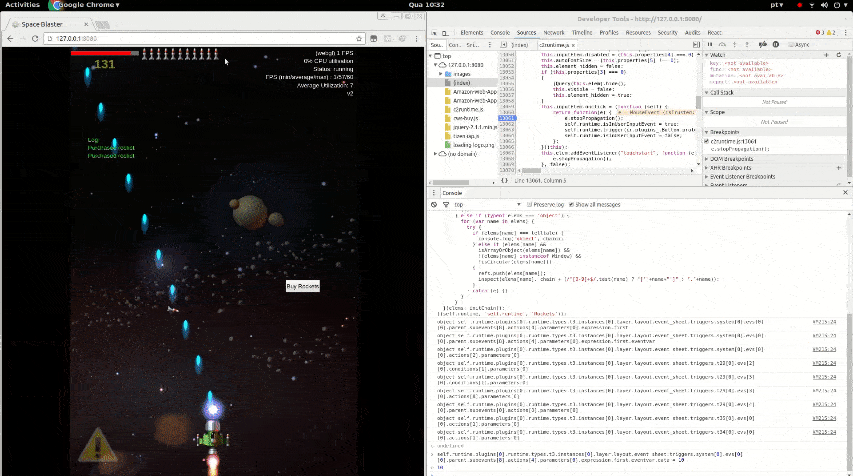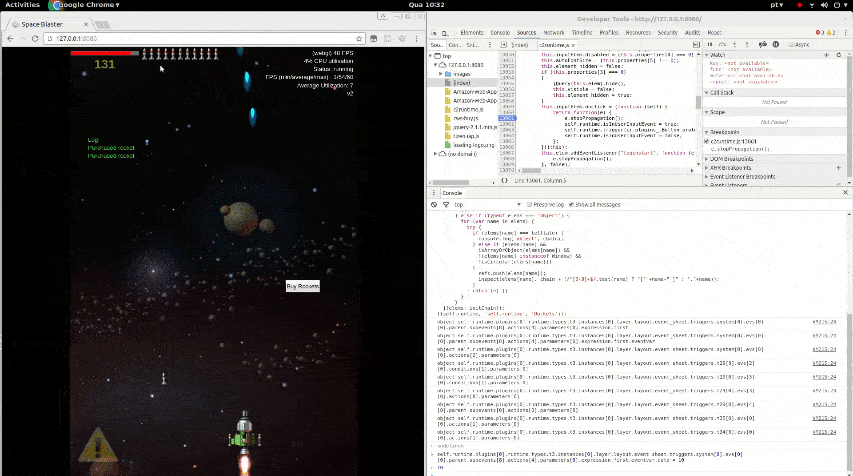
Reverse-engineering a game’s source code to bypass a paywall.
Licensing agreements and copyrights are especially important for digital content such as video or audio streams. By accessing the underlying JavaScript of HTML5 web players, attackers can capture and redistribute streams, causing massive business losses for streaming providers.
So, enterprises rely on JavaScript to build apps that are core to their business, but it exposes their core logic and proprietary algorithms to attack. Again, they have no way of encrypting this code. What they can do, though, is protect JavaScript with layers that prevent these attacks.
JavaScript: Solutions
When addressing the threats of code theft and reverse engineering, the only feasible way to protect JavaScript is to conceal its logic. This is a recommendation by OWASP in their Mobile Top 10 Security Risks, M9-Reverse Engineering:
In order to prevent effective reverse engineering, you must use an obfuscation tool.
JavaScript obfuscation is a core step in protecting JavaScript source code. Obfuscated JavaScript is extremely complex to read, understand, and reverse engineer. But different JavaScript obfuscators offer widely varying levels of protection, and development teams often struggle to choose the right tool. Free obfuscators offer basic transformations that can easily be reversed using automated tools.
When deciding which obfuscation tool to use, besides considering the cost of the tool, you should ask yourself:
What would it cost my business if an attacker redistributed my code, tampered with it, or bypassed our licensing agreements?
Then, we must still consider the more advanced and dangerous threats of application abuse, cheating, and piracy. Free obfuscators offer no real protection against these. Again, enterprise-grade problems require enterprise-grade solutions.
Jscrambler is a market-leading JavaScript protection solution for the enterprise. Not only does it provide the most advanced set of obfuscation techniques, but it also adds three additional protective layers to mitigate debugging and tampering attempts:
- Code Locks — Varying application locks that restrict when, where, and by whom your JavaScript application can be executed.
- Self-Defending — When your protected code faces a debugging or tampering attempt, Jscrambler’s integrity checks break the application or trigger a countermeasure specified by you.
- Self-Healing — Runtime integrity checks that automatically revert tampered code back to original, clean code, without breaking the app or interfering with the user experience.
Together, these technologies effectively mitigate abuse, cheating, piracy, code theft, and reverse-engineering attempts that operate through the client side. This technology has earned the trust of Fortune 500 companies, along with over 43,000 other companies and individuals, who trust Jscrambler to protect their applications.
Looking Ahead
The future looks promising for JS. The enterprise keeps raising the bar by delivering highly advanced web and mobile user experiences, leveraging JavaScript’s ubiquity, flexibility, and extremely active community.
While malicious actors will target these apps for their own gain, companies can (and should) take action to conceal their code logic and actively thwart debugging and tampering attempts. And, unlike some argue, it’s not about security through obscurity—it’s about adding a new security layer to further protect critical business assets.
If you’re interested in how Jscrambler fits your specific use case, book a demo with our application security experts to see our solutions in action.