Thank you to everyone who connected with us in Seattle.
Throughout the event, our conversations with privacy and data governance leaders consistently centered on one critical compliance challenge: The CMP Gap.

Consent Management Platforms (CMPs) successfully capture privacy choices, but they cannot enforce them at runtime. This browser blind spot leaves organizations highly vulnerable to unauthorized third-party tracking, silent data exfiltration, and significant liability under laws and regulations like CCPA, HIPAA, and CIPA.
It was inspiring to see so many privacy professionals actively looking to move beyond simply capturing consent, seeking ways to turn documented privacy policies into strict, automated runtime enforcement.
Spotlight Session: What the Pixel Saw, and What It Sent
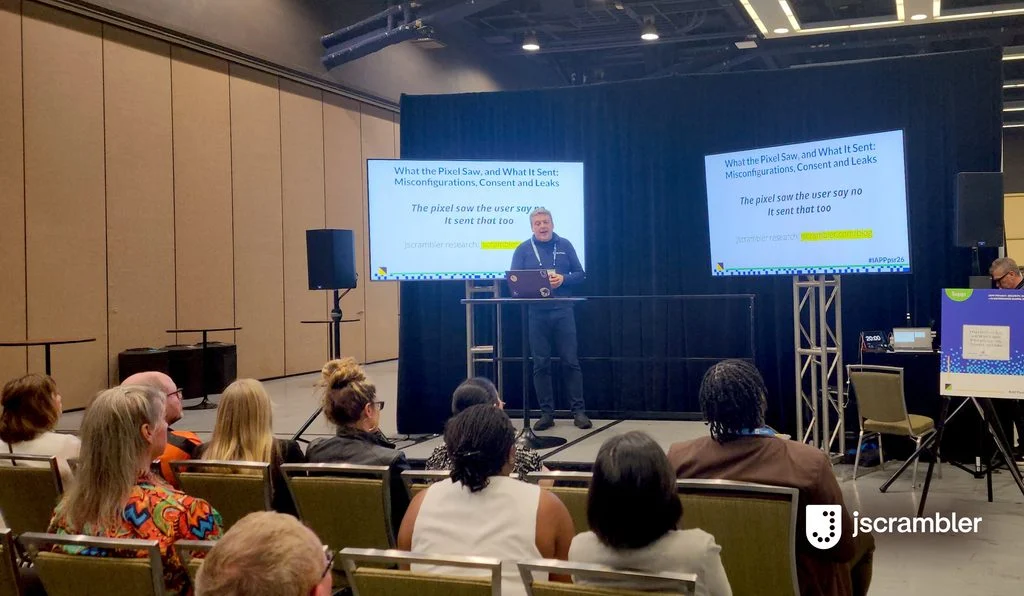
A major highlight of the week was the Spotlight Session led by Gareth Bowker, Jscrambler’s Head of Information Security. Sharing runtime analysis of real customer journeys across live banking and retail sites, Gareth revealed exactly how third-party pixels bypass consent:
- Pixels often fire before the consent banner is even engaged.
- User data continues to flow to third-party platforms even after explicitly rejecting cookies.
- Sensitive details regularly leak into URLs and persist in logs and browser history.
- Privacy laws still classify hashed identifiers as personal data.
If you missed the session, you can download Gareth’s slides below
Executive Dinner: Beyond Consent
The discussions continued at our invitation-only dinner for privacy and governance executives. Over an open dialogue about the reality of third-party tracking and embedded AI agents, industry leaders shared how they are tackling the challenge of enforcing consent. The consensus was clear: the industry is pivoting from capturing consent to actively enforcing it.
Join us in Seattle during IAPP 2026! Our team will be available throughout the event for one-on-one conversations about today’s security, compliance, and data protection challenges. Whether you’re evaluating new initiatives or looking to strengthen your existing strategy, we’d love to connect.
Close the Enforcement Gap
Because CMPs cannot govern the browser’s execution environment, organizations need active controls to ensure third-party code actually respects user choices. Jscrambler works alongside your existing CMP to monitor runtime behavior, block unauthorized data exfiltration, and generate definitive audit trails for GDPR, CCPA, HIPAA, and PCI DSS compliance.
Keep the conversation going:
Join our next webinar
From Consent to Enforcement: The Privacy Gap CMPs Leave and How to Address Them.
🗓️ Nov 10, 2026 • 12pm ET | 5pm UK
Schedule a 1-on-1 Meeting: See exactly how Jscrambler actively enforces your privacy policies at runtime.
Meet the speakers


Beyond Analytics: The Silent Collection of Commercial Intelligence by TikTok and Meta Ad Pixels
Read Now
5 Steps to Minimize California Invasion of Privacy Act (CIPA) Litigation Risk
Read Now
Jscrambler vs Consent Management Platforms (CMPs)
Compare Jscrambler and CMPs