

With so much third-party code being run on the client-side of web applications, companies have no clue what they’re running there. Third-party scripts have the same power as internally developed scripts. They can harvest any user input (including PII and credit card data), add extra code, and fully modify the page’s behavior.
Attackers are taking advantage of this, blindsiding companies with complex web supply chain attacks, namely with web skimming attacks (Magecart). How can companies gain visibility and control of client-side code? Is CSP the answer?
In this webinar, we:
– Explain the client-side blind spot
– Explore how a Content Security Policy handles third-party code and its pitfalls
– Explain how to gain full visibility of client-side scripts and get granular control of their behavior
– Go over key insights from Jscrambler customers
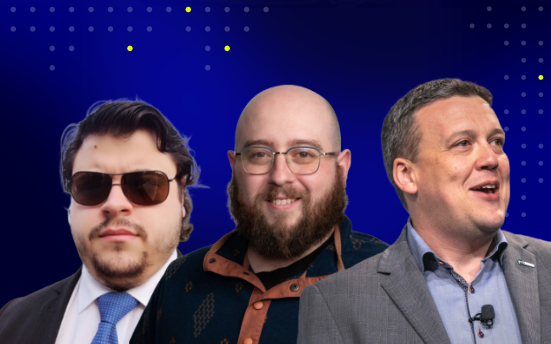
Meet the Speakers
Pedro Fortuna
Jscrambler CTO & Co-Founder
Filipe Pereira
VP of Engineering at Jscrambler