
Jscrambler Vintes
Explore articles by Jscrambler
AI Security
LLMs Just Made Your IP Easier to Steal: Here’s the Fix
JavaScript is, by design, delivered in the open. Every line of client-side code an organization ships reaches the user’s device in a form that can be read, inspected, copied, and…
Client-Side Security
Privilege Without Control: Rethinking the Architectural Edge for CISOs
Ask a room full of CISOs where their architectural edge begins, and you’ll likely get a dozen different answers. Some will point to the network boundary. Others will say identity…

Code Protection
Jscrambler Enhances Code Integrity Product to Be LLM-Resilient
The latest Code Integrity release builds on Jscrambler’s LLM-resilient foundation with code-hardening improvements that broaden protection coverage, ensuring stronger defense against AI-driven reverse engineering. As AI threats become more prominent,…
Client-Side Security
Agentic SOC: Completing the Context Layer with the Browser
The security operations center is undergoing its biggest structural shift in two decades. The recent launch of the Agentic SOC Alliance signals a major milestone: enterprise defense is officially standardizing…

Products & Platform
Jscrambler Launches Unified Client-Side Security Platform to Secure Software and Data in the Age of AI
AI is fundamentally changing how software is attacked, and customer data is exposed inside the browser. As organizations rapidly adopt AI-powered applications, agents, and third-party services, existing security architectures built…

Code Protection
Hashing Algorithms
Hashing is the process of taking any piece of data- a password, a file, a message- and converting it into a short, fixed-length string of characters called a hash, digest,…

Products & Platform
Security Advisory: Unauthorized Publication of a Malicious npm Package Affecting CI
At a Glance Affected package: jscrambler Affected products: Code Integrity Affected versions: 8.14/8.16/8.17/8.18/8.20 Safe version: 8.22 Other affected packages and versions: jscrambler-webpack-plugin 8.6.2 gulp-jscrambler 8.6.2 grunt-jscrambler 8.5.2 jscrambler-metro-plugin 9.0.2 Safe…
Data Governance & Privacy
5 Key Takeaways from IAPP Global Summit 2026
Jscrambler recently joined thousands of privacy and legal professionals at the IAPP Global Summit 2026 in Washington, D.C. It was an invaluable opportunity to connect with experts and leaders dedicated…

Client-Side Security
Client-Side Protection: Effectiveness vs Consolidation
Security leaders today face a familiar mandate: consolidate tools, reduce operational complexity, and improve efficiency. Web Application Protection Platforms (WAPPs) have emerged as a compelling answer, promising unified protection across…
Code Protection
JavaScript Obfuscation: The Definitive Guide
The JavaScript Obfuscation Practical Guide 2026 provides a step-by-step approach to exploring key questions, namely: What is an obfuscation code? Why obfuscate JavaScript code? What is JavaScript obfuscation, and how…
Security Research
Silent Skimming vs Double-Entry Attacks
by Pedro Marrucho and David Alves, with contributions by Tom Vicary Client-side attacks against e-commerce aren’t going away and are evolving. Threat actors are constantly changing their methods, shifting from…

Products & Platform
Jscrambler Wins Innovator Award for Client-Side Protection at 2025 Global InfoSec Awards
Porto, Portugal Jscrambler, the pioneering platform for client-side protection, today announced that it has been named an Innovator for Client-Side Protection by Cyber Defense Magazine (CDM), the industry’s leading electronic…
Compliance Enforcement
Q&A with Elavon’s Andrew McCarroll: Mastering PCI DSS 6.4.3 and 11.6.1 to Combat Web Skimming
1. Andrew, how does your role at Elavon EU shape payment security strategies to help merchants meet PCI DSS requirements 6.4.3 and 11.6.1? My role at Elavon involves designing security…
Client-Side Security
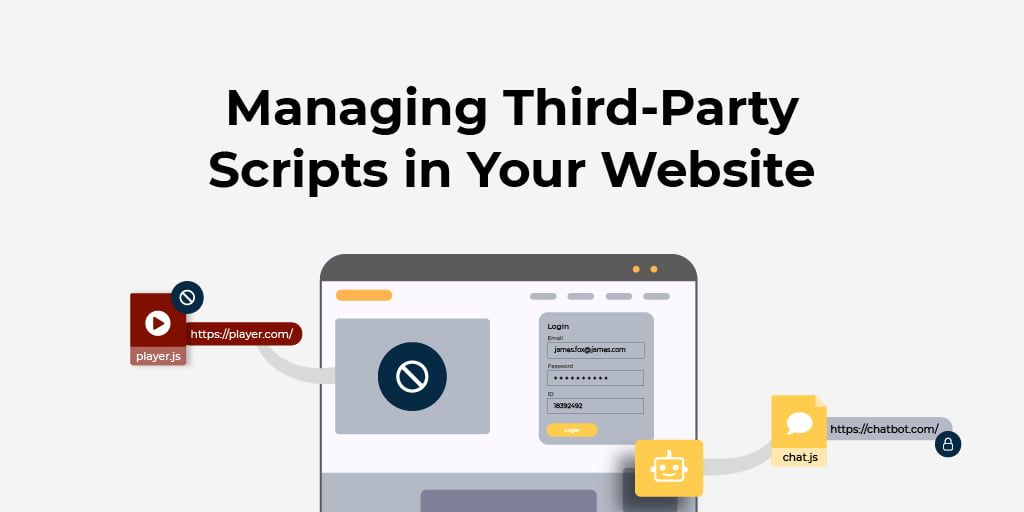
How To Vet and Manage The Behavior of Third-Party Scripts in Your Website
Vetting and managing the behavior of third-party scripts on your website allows you to avoid websites sinking with third-party scripts. Also, the third-party JavaScript management Cheat Sheet is especially relevant…