
🗓️ November 5 – 6, 2026
Meet Jscrambler at OWASP Global AppSec USA 2026
AI Is Moving Risk to Runtime
SAST, SCA and code review catch a lot before deploy. But with AI tools generating front-end code at scale, third-party scripts updating on their own schedule, and AI agents operating inside live sessions, more of what runs in your users’ browsers never passed through your pipeline in its current form. That browser runtime sits beyond the edge, where build-time testing and server-side controls don’t reach.
Close the AI Execution Gap with Jscrambler
Jscrambler adds runtime enforcement to the client side, so your security controls cover the code as it actually executes, not only as it was tested.
- AI-Generated Code Security: AI-generated JavaScript can ship with subtle logic flaws and non-standard patterns that slip through review. Because that code runs on the user’s device, an exploitable flaw opens the door to DOM tampering, formjacking and data exfiltration. Jscrambler enforces runtime behavior so a flaw can’t be turned into an attack in production.
- Third-Party Script Enforcement: Scripts that were clean at review can change behavior later, outside your release cycle. Jscrambler applies behavioral rules to every first- and third-party script in the browser, blocking unauthorized DOM changes and data access as they happen. This addresses the client-side side of OWASP Top 10:2025 A03 Software Supply Chain Failures.
- AI Data Governance: AI agents and AI-powered tags now read and act on page content in live sessions. Jscrambler inventories what runs on your pages and enforces what each script and agent is allowed to touch.
- LLM-Resilient Code Protection: LLMs make it faster to de-obfuscate and reverse engineer client-side logic. Jscrambler’s polymorphic code protection is built to resist AI-assisted analysis, protecting proprietary logic from reverse engineering, automated scraping and tampering.
Attending OWASP San Francisco 2026? Let’s Meet.
Stop by booth S16 for a technical session with Pedro Fortuna, Co-Founder & CTO, and Jeffrey Cleveland, Pre-Sales Engineer. Bring your client-side questions about securing AI-generated code, locking down third-party scripts, or protecting your front-end logic from LLM-assisted reverse engineering, and we’ll walk through how runtime enforcement handles them.
Reserve time with our team at booth S16. We look forward to seeing you in San Francisco.
Meet Jscrambler at OWASP Unfiltered
 November 5th, 2026 • 7:00 – 9:00 PM
 Perry’s Embarcadero
🤖 Get a Chance to Win a LEGO® Star Wars™ R2-D2
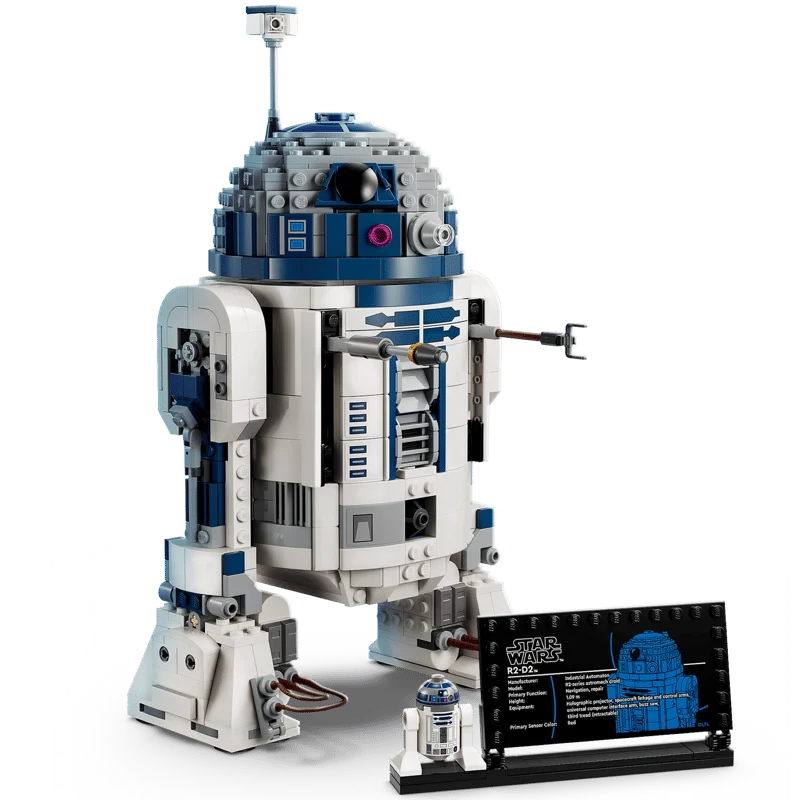
Visit the Jscrambler booth (S16) at OWASP Global AppSec USA for a chance to take home a LEGO® Star Wars™ R2-D2 set. Entering is simple: get your badge scanned at our booth, collect your numbered raffle ticket, and join us at 5:00 PM on Thursday, November 5, during the networking reception, when we draw the winner live.
Meet the Team

Related Resources
LLMs Just Made Your IP Easier to Steal: Here’s the Fix
Read Now
Jscrambler Enhances Code Integrity Product to Be LLM-Resilient
Read Now
Agentic SOC: Completing the Context Layer with the Browser
Read Now