


Browser-in-the-browser (BitB) attacks have different approaches, usually targeting credentials. Today, we will explore this deception technique further.
As a new phishing technique, it falls under the umbrella of social engineering attacks, which account for more than 80% of reported security incidents.
What is a browser-in-the-browser attack?
The main goal of a browser-in-browser attack is to lure users into accessing a cloned website through a fake window, taking advantage of the growing use of single sign-on systems that let users log in to different websites with a single account.
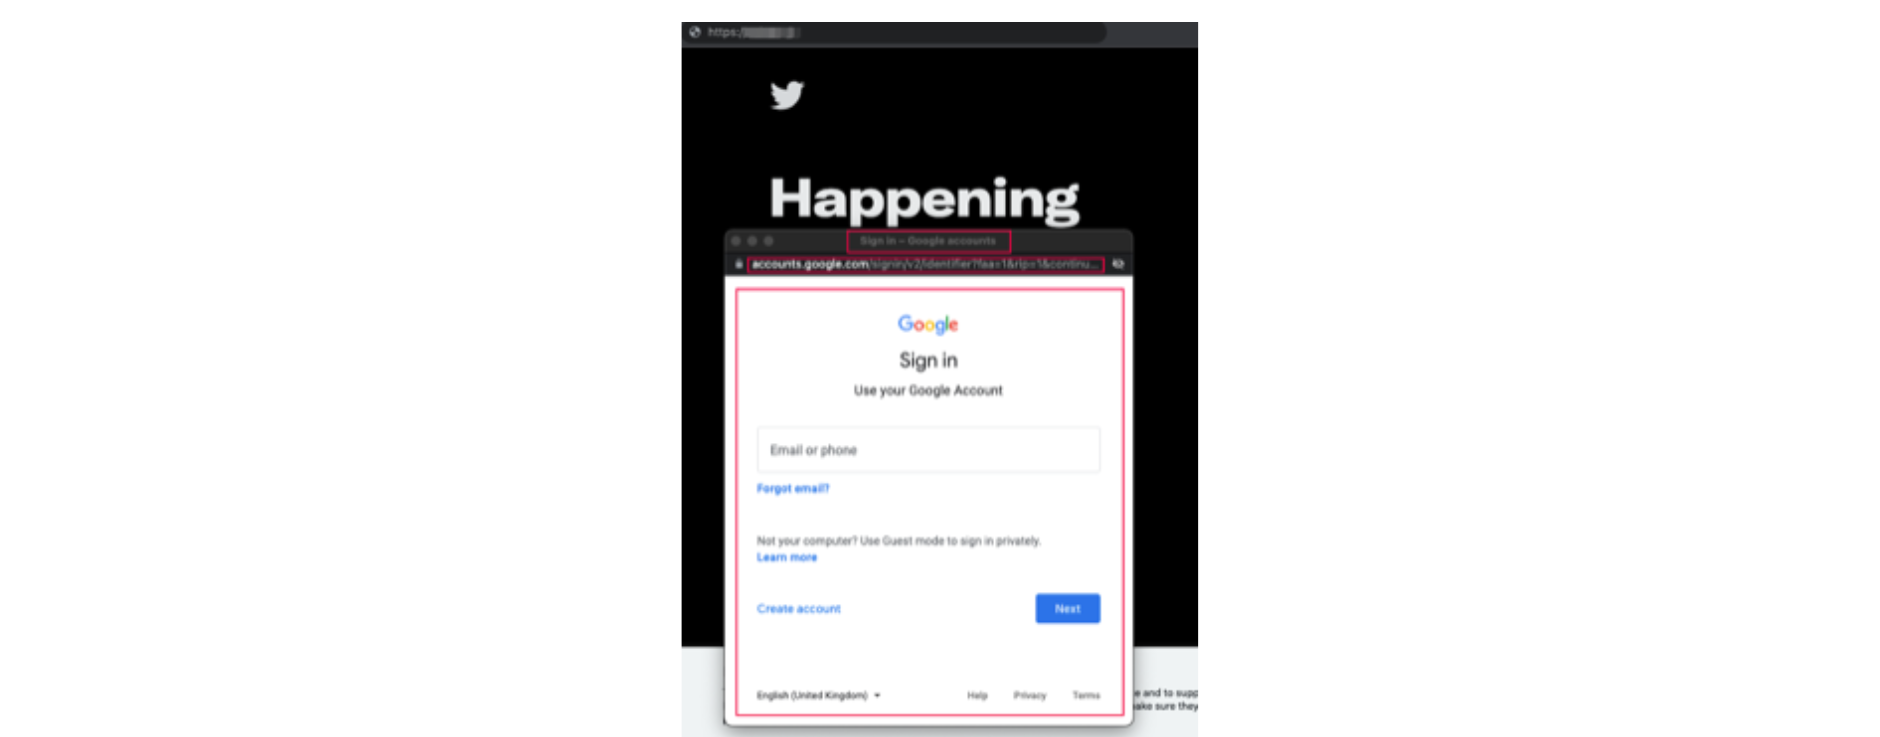
This “fake window” is created inside the website viewport and will replicate very accurately all the components of the popup window.
Some aspects of this method include the URL, which can show any URL, the Certificate Lock, and the draggable effect.
The image below shows an example of a cloned website using this technique. The highlighted sections show how visually accurate this window can be.
This approach is not new. We can trace it back to some attacks in the past two decades.
In 2019, a fake Steam skins giveaway site stole credentials from Counter-Strike players, but this wasn’t an isolated incident.
Phishing campaigns also targeted Facebook using this technique. Going back to 2007, we find remarks about a “picture-in-picture attack” in a Microsoft publication. They claim that “picture-in-picture attacks showing a fake browser window were as effective as the best other phishing technique, the homograph attack.”.
Other approaches to this deception technique
While the BitB technique is used in the wild on fake cloned websites, similar methods could apply in other scenarios, such as a supply chain attack.
Browser Extensions
Browser extensions provide a great way to customize your web browser or even enhance a website’s functionality.
Today, users most likely have an ad blocker, a password manager, or a cryptocurrency wallet extension installed in their browser. As helpful as they can be, some of them may also pose a security risk.
Suppose a malicious script draws one of these extension windows on a webpage, similar to the BitB attack we described before.
An unaware user may see this window and mistake it for the legitimate one, enter their credentials or keys, and naively send them to the attacker.
Browser Notifications
Although this type of notification typically doesn’t ask the user to type anything in the notification window, a fake one could still make the user click it.
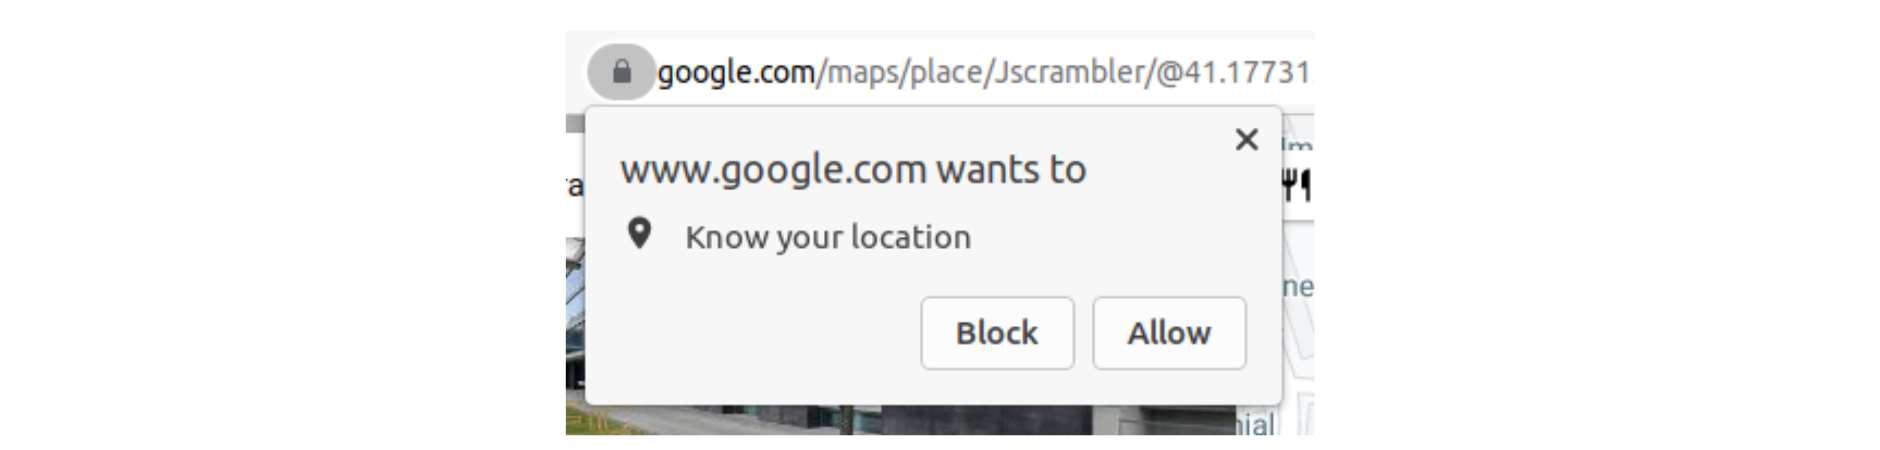
Clickjacking, where a user clicks something different from what they perceive, is a potentially dangerous attack that can reveal confidential information or trigger unintended behavior in the website or browser.
Sometimes clicking seemingly innocuous objects can let an attacker take control of your computer.
Javascript alerts
Some applications may use JavaScript functions like alert, confirm, or prompt to ask the user for important information. These functions trigger a box to appear, usually at the top of the screen, but this may vary depending on the message provided.
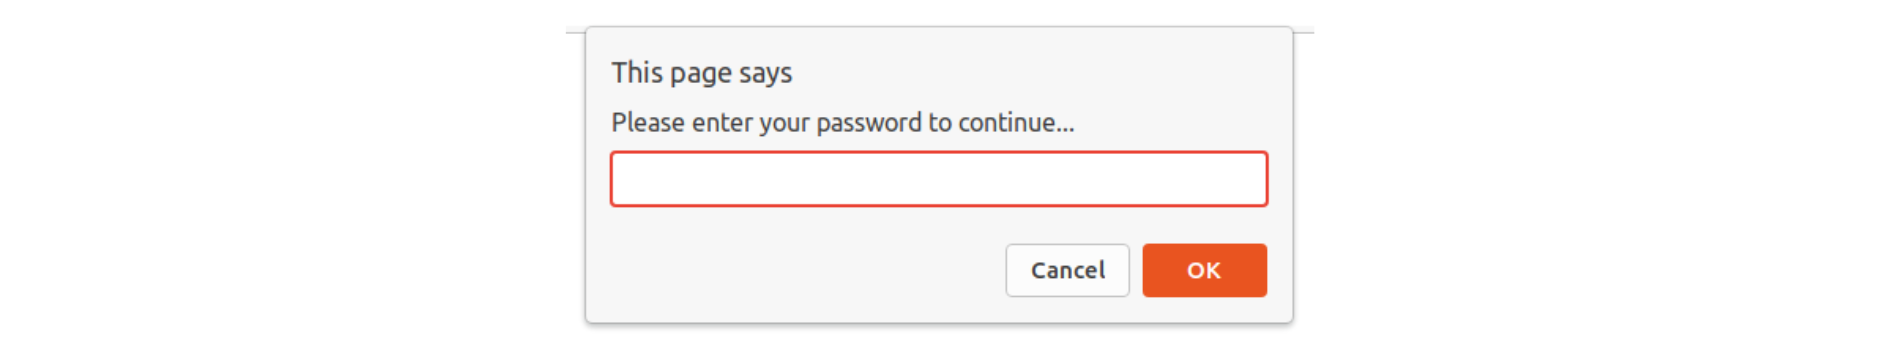
This is another example of a window that can be drawn inside a webpage, inviting users to type private information.
Summing Up
As we can see, many deception techniques can lure users into performing unwanted actions. But there are ways to mitigate this.
From a company perspective, organizations are responsible for the user experience they provide and the security of their applications. Thus, they should implement systems or mechanisms on their web pages to mitigate these attacks.
In short, the types of attacks we saw consisted of:
- Creating and appending elements, e.g., creating an iframe
- Poisoning functions, e.g., altering the login function
- Editing element attributes, e.g., changing a link
These malicious behaviors can be detected or blocked if a client-side security solution is implemented on web pages.
User-Awareness Guidelines
Even though we describe attacks that may deceive even the savviest users, a few subtle clues can help detect this kind of attack.
- Users can click the suspect window title bar and drag it around the screen. A legitimate window can be dragged anywhere, while a fake window stays within the boundaries of its parent browser window.
- Users can hover over the browser icon in the taskbar. If the popup is a real browser window, there should be (at least) two instances of the browser running, but if not, then the user would only see one instance.
- Users can right-click the suspect window’s title bar. The context menu of a legitimate popup should display window-related options like New Tab or Close, but a fake window will show content-related options like Back, View Page Source, or Inspect.
- Users can look for active or focused windows. There should only be one active window at a time. A fake window will appear focused while the real window is still focused.
Conclusion
Many companies protect their users with client-side solutions like the Webpage Integrity by Jscrambler. These solutions provide an additional layer of protection that will render most of these attacks unfeasible or impractical.
But most websites lack this kind of protection, leaving responsibility with the user. This is why User awareness is crucial for user and information security.